

Windows มีฟีเจอร์ Built-in สำหรับติดตามว่าใคร View, Edit, หรือ Delete ไฟล์ในโฟลเดอร์ที่ระบุ ไม่ต้องโปรแกรมภายนอก
ฟีเจอร์นี้เป็นส่วนของ Group Policy ที่ IT Pro ใช้จัดการคอมพิวเตอร์ใน Corporate Network ผ่าน Server แต่ใช้ Local บน PC ได้โดยไม่ต้องมี Server ข้อจำกัด: ไม่มีใน Windows รุ่นต่ำ Windows 7 ต้อง Pro ขึ้นไป Windows 8 ต้อง Pro/Enterprise
Group Policy คือชุด Registry Settings ที่ควบคุมผ่าน GUI เปิด/ปิด Setting แล้ว Registry จะอัปเดต
Windows XP: Start → Run พิมพ์ gpedit.msc
Windows 7: Start พิมพ์ gpedit.msc ใน Search Box
Windows 8: Start Screen พิมพ์ หรือ Charms Bar (มุมขวาบน/ล่าง) → Search → gpedit
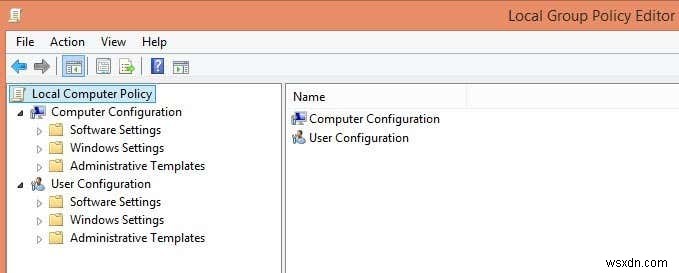
มี 2 หมวด: User และ Computer User Policies = ต่อ User, Computer Policies = System-wide เราต้องการทุก User → ขยาย Computer Configuration
ขยายต่อ: Windows Settings → Security Settings → Local Policies → Audit Policy ด้านขวาจะเห็น Policies และ Setting ปัจจุบัน
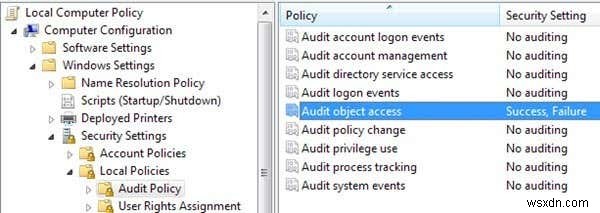
Double-click Audit Object Access เลือก Success และ Failure OK → เสร็จส่วนบอก Windows ให้พร้อม Monitor ต่อไปบอกว่า Track อะไร ปิด Group Policy Console
ไปที่โฟลเดอร์ที่ต้องการ Monitor ใน Explorer คลิกขวา → Properties → Tab Security
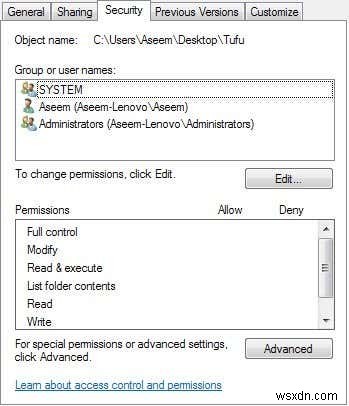
คลิก Advanced → Tab Auditing ตรงนี้ตั้งค่าอะไรที่จะ Monitor
คลิก Add → Dialog ใส่ User/Group พิมพ์ users → Check Names → จะกลายเป็น COMPUTERNAME\Users
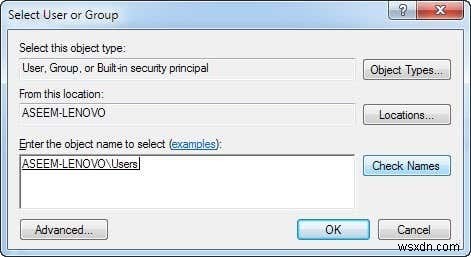
OK → Dialog Audit Entry นี่คือหัวใจ: เลือก Activity ที่ต้องการ Track เช่น Delete, Create files/folders ฯลฯ แนะนำเลือก Full Control จะเลือกทั้งหมดอัตโนมัติ ทำทั้ง Success และ Failure ทุกการกระทำจะมีบันทึก
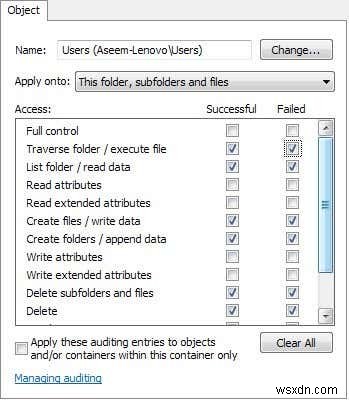
OK × 3 ออกจาก Dialog ทั้งหมด → ตั้งค่า Auditing โฟลเดอร์เสร็จ!
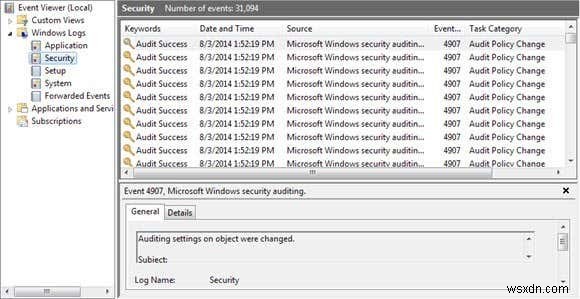
ดู Event ยังไง? Control Panel → Administrative Tools → Event Viewer → Section Security ด้านขวาจะมี Event มากมาย
ลองสร้างไฟล์/เปิดโฟลเดอร์ กด Refresh (ไอคอนลูกศรเขียว 2 อัน) จะเห็น Event Category File System = Delete, Create, Read, Write บนโฟลเดอร์/ไฟล์ที่ Audit Windows 7 ทุกอย่างอยู่ใน File System Task Category ต้องคลิกแต่ละ Event ดู
เพื่อให้ง่าย ใช้ Filter: View Menu → Filter (หรือ Right-click Security Log → Filter Current Log) Event ID ใส่ 4656 = User ทำ File System Action จะได้ข้อมูลสำคัญโดยไม่ต้องอ่านพันรายการ
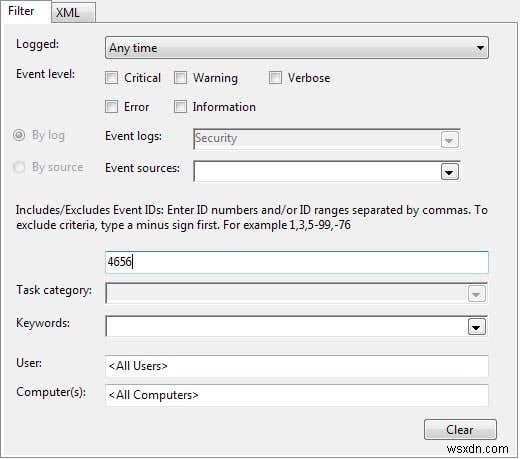
Double-click Event เพื่อดูรายละเอียด
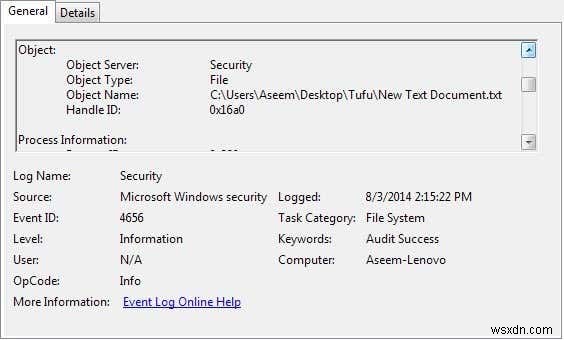
ตัวอย่าง Event: ลบไฟล์ New Text Document.txt ในโฟลเดอร์ Tufu บน Desktop Accesses: DELETE, SYNCHRONIZE, ReadAttributes
อีกตัวอย่าง: เปิด Address Labels.docx ด้วย WINWORD.EXE Accesses: READ_CONTROL, SYNCHRONIZE, ReadData, WriteData, AppendData ฯลฯ
ต้องลองทดสอบสร้างโฟลเดอร์ทดสอบ ทำ Action ต่างๆ ดู Event Viewer จะเข้าใจรูปแบบ ระบบนี้เชื่อถือได้ หากมีคำถาม 留言ได้ครับ ขอให้สนุก!
