

ผู้ดูแลระบบ Windows ส่วนใหญ่ที่คุ้นเคยกับ PKI รู้จักเครื่องมือ MakeCert.exe ซึ่งอนุญาตให้สร้าง Self-Signed Certificate เครื่องมือนี้เป็นส่วนหนึ่งของ Microsoft .NET Framework SDK และ Microsoft Windows SDK บน Windows เวอร์ชันสมัยใหม่ (Windows 10/8.1 และ Windows Server 2019/2016/2012R2) คุณสามารถสร้าง Self-Signed Certificate ได้โดยใช้ Cmdlet PowerShell ในตัว New-SelfSignedCertificate โดยไม่ต้องใช้เครื่องมือเพิ่มเติม
การใช้ Cmdlet New-SelfSignedCertificate ของ PowerShell เพื่อสร้าง Self-Signed Certificate
เพื่อสร้าง Self-Signed Certificate ด้วย PowerShell คุณสามารถใช้ Cmdlet New-SelfSignedCertificate ซึ่งเป็นส่วนหนึ่งของโมดูล PoSh PKI (Public Key Infrastructure):
เพื่อแสดงรายการ Cmdlets ทั้งหมดที่พร้อมใช้งานในโมดูล PKI ให้รันคำสั่ง
Get-Command -Module PKI
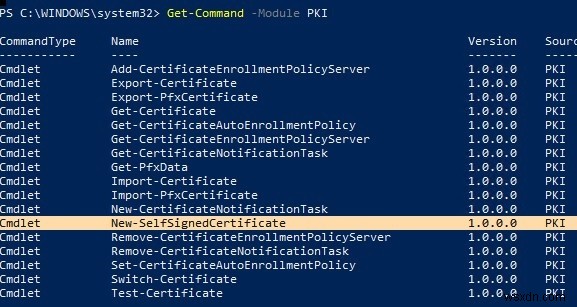
แนะนำให้ใช้ Self-Signed Certificates สำหรับการทดสอบ หรือเพื่อให้ Certificate กับบริการ Intranet ภายใน (IIS, Exchange, Web Application Proxy, LDAPS, ADRMS, DirectAccess ฯลฯ) หากคุณไม่สามารถปรับใช้โครงสร้างพื้นฐาน PKI/CA หรือซื้อ Certificate ที่เชื่อถือได้จากผู้ให้บริการภายนอก
เคล็ดลับ อย่าลืมว่าคุณสามารถรับ SSL Certificate ฟรีจาก Let's Encrypt ได้ง่าย ๆ นี่คือตัวอย่างวิธีการออก Let's Encrypt SSL Certificate และผูกกับไซต์ IIS บน Windows Server
เพื่อสร้าง Certificate คุณต้องระบุค่าของ –DnsName (ชื่อเซิร์ฟเวอร์ ชื่ออาจเป็นอะไรก็ได้และต่างจากชื่อ localhost) และ -CertStoreLocation (Local Certificate Store ที่ Certificate ที่สร้างจะถูกวาง) คุณสามารถใช้ Cmdlet นี้เพื่อสร้าง Self-Signed Certificate บน Windows 10 (ในตัวอย่างนี้) Windows 8.1 และ Windows Server 2019/2016/2012 R2/2012
เพื่อสร้าง SSL Certificate ใหม่ (ประเภท SSLServerAuthentication เริ่มต้น) สำหรับ DNS Name test.contoso.com (ใช้ชื่อ FQDN) และวางไว้ในรายการ Personal Certificates บนคอมพิวเตอร์ ให้รันคำสั่งต่อไปนี้:
New-SelfSignedCertificate -DnsName test.contoso.com -CertStoreLocation cert:\LocalMachine\My
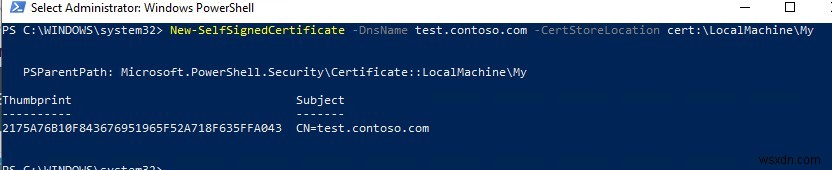
Directory: Microsoft.PowerShell.Security\Certificate::LocalMachine\My Thumbprint Subject ---------- ------- 2175A76B10F843676951965F52A718F635FFA043 CN=test.contoso.com
หากคุณรันคำสั่งนี้ในเซสชัน PowerShell ที่ไม่ได้รับสิทธิ์ยกระดับ (ไม่มีสิทธิ์ Local Admin) จะเกิดข้อผิดพลาด:
New-SelfSignedCertificate : CertEnroll::CX509Enrollment::_CreateRequest: Access denied. 0x80090010 (-2146893808 NTE_PERM)
หากคุณระบุ Cryptographic Provider (CSP) ที่ไม่ใช่มาตรฐาน ตัวอย่างเช่น ใช้พารามิเตอร์ -KeyAlgorithm "ECDSA_secP256r1" -Provider "Microsoft Smart Card Key Storage Provider" ตรวจสอบให้แน่ใจว่ามันติดตั้งอยู่บนคอมพิวเตอร์ของคุณ (ค่าเริ่มต้นคือ Microsoft Enhanced Cryptographic Provider CSP) มิฉะนั้น จะเกิดข้อผิดพลาด:
New-SelfSignedCertificate: CertEnroll::CX509Enrollment::_CreateRequest: Provider type not defined. 0x80090017 (-2146893801 NTE_PROV_TYPE_NOT_DEF).
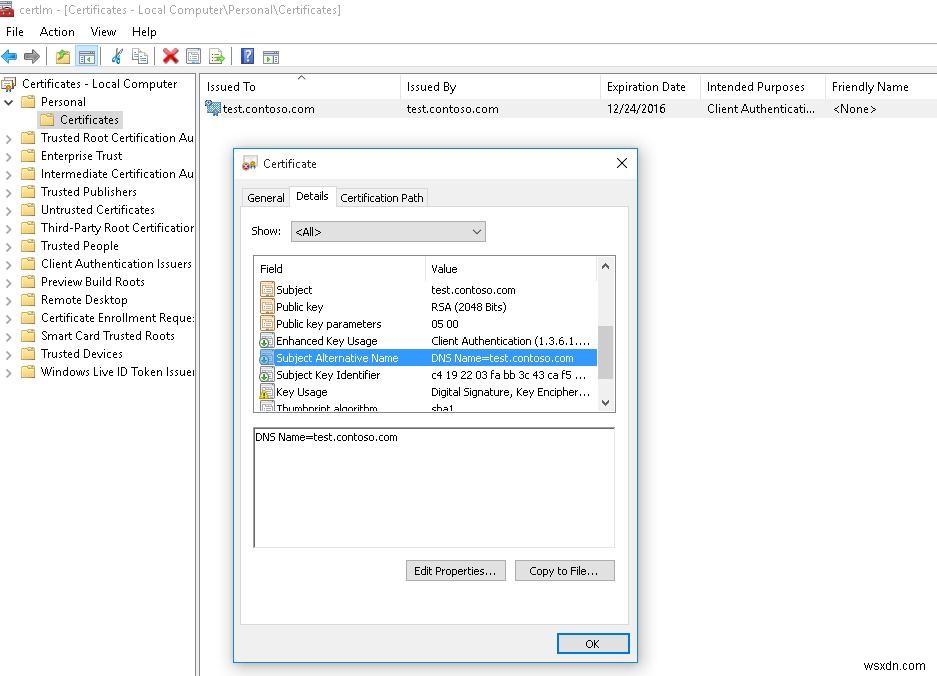
คำสั่งนี้สร้าง Certificate ใหม่และนำเข้าเข้าไปใน Personal Certificate Store ของคอมพิวเตอร์ เปิดสแนปอิน MMC certlm.msc ตรวจสอบว่า Certificate ใหม่ปรากฏในส่วน Personal ของ Certificate Store
ตามค่าเริ่มต้น Self-Signed Certificate ถูกสร้างด้วยการตั้งค่าต่อไปนี้:
- อัลกอริทึมการเข้ารหัส: RSA;
- ความยาวคีย์: 2048 bit;
- การใช้งานคีย์ที่ยอมรับ: Client Authentication และ Server Authentication;
- Certificate สามารถใช้สำหรับ: Digital Signature, Key Encipherment;
- ช่วงเวลาที่ Certificate ถูกต้อง: 1 ปี
ดังที่คุณเห็น คุณสมบัติของ Certificate ระบุว่าสามารถใช้สำหรับ Client Authentication ได้ แต่ก็ยังถูกต้องสำหรับ Server Authentication ด้วย
โดยใช้ Cmdlet Get-ChildItem คุณสามารถแสดงพารามิเตอร์ทั้งหมดของ Certificate ที่สร้างขึ้นโดย Thumbprint ของมัน:
Get-ChildItem -Path "Cert:\LocalMachine\My" | Where-Object Thumbprint -eq 2175A76B10F843676951965F52A718F635FFA043 | Select-Object *
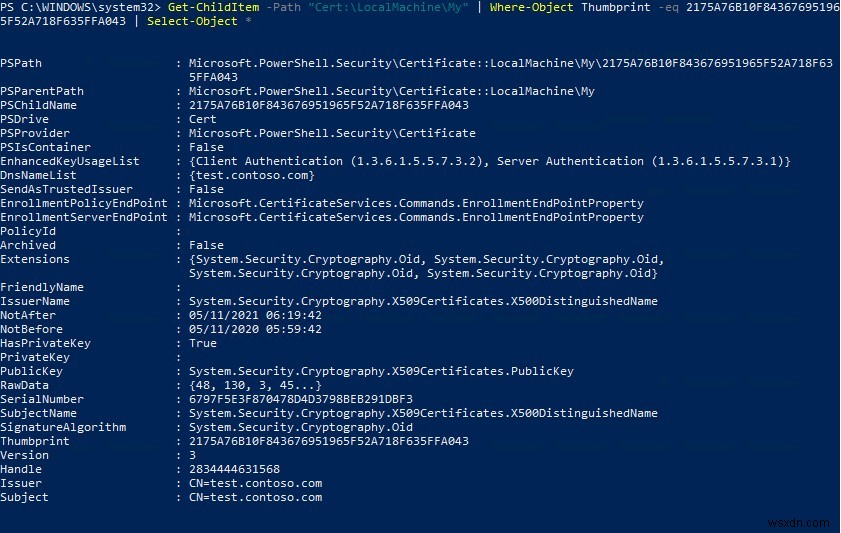
PSPath : Microsoft.PowerShell.Security\Certificate::LocalMachine\My\2175A76B10F843676951965F52A718F635FFA043 PSParentPath : Microsoft.PowerShell.Security\Certificate::LocalMachine\My PSChildName : 2175A76B10F843676951965F52A718F635FFA043 PSDrive : Cert PSProvider : Microsoft.PowerShell.Security\Certificate PSIsContainer : False EnhancedKeyUsageList : {Client Authentication (1.3.6.1.5.5.7.3.2), Server Authentication (1.3.6.1.5.5.7.3.1)} DnsNameList : {test.contoso.com} SendAsTrustedIssuer : False EnrollmentPolicyEndPoint : Microsoft.CertificateServices.Commands.EnrollmentEndPointProperty EnrollmentServerEndPoint : Microsoft.CertificateServices.Commands.EnrollmentEndPointProperty PolicyId : Archived : False Extensions : {System.Security.Cryptography.Oid, System.Security.Cryptography.Oid, System.Security.Cryptography.Oid, System.Security.Cryptography.Oid} FriendlyName : IssuerName : System.Security.Cryptography.X509Certificates.X500DistinguishedName NotAfter : 05/11/2021 06:19:42 NotBefore : 05/11/2020 05:59:42 HasPrivateKey : True PrivateKey : PublicKey : System.Security.Cryptography.X509Certificates.PublicKey RawData : {48, 130, 3, 45...} SerialNumber : 6797F5E3F870478D4D3798BEB291DBF3 SubjectName : System.Security.Cryptography.X509Certificates.X500DistinguishedName SignatureAlgorithm : System.Security.Cryptography.Oid Thumbprint : 2175A76B10F843676951965F52A718F635FFA043 Version : 3 Handle : 2834444631568 Issuer : CN=test.contoso.com Subject : CN=test.contoso.com
หมายเหตุ Self-Signed Certificate แบบนี้จะหมดอายุใน 1 ปี นับจากวันที่สร้าง คุณสามารถตั้งค่าช่วงเวลาที่ Certificate ถูกต้องแตกต่างออกไปโดยใช้ตัวเลือก –NotAfter ตัวอย่างเช่น คุณสามารถออก SSL/TLS Certificate ที่มีช่วงเวลาถูกต้อง 3 ปีได้ด้วยคำสั่งต่อไปนี้:
$todaydt = Get-Date
 $3years = $todaydt.AddYears(3)
 New-SelfSignedCertificate -dnsname test.contoso.com -notafter $3years -CertStoreLocation cert:\LocalMachine\My
คุณสามารถสร้าง Certificate Chain ได้ ก่อนอื่น สร้าง Root Certificate (CA) และจากนั้นสร้าง SSL Server Certificate จากมัน:
$rootCert = New-SelfSignedCertificate -Subject 'CN=TestRootCA,O=TestRootCA,OU=TestRootCA' -KeyExportPolicy Exportable -KeyUsage CertSign,CRLSign,DigitalSignature -KeyLength 2048 -KeyUsageProperty All -KeyAlgorithm 'RSA' -HashAlgorithm 'SHA256' -Provider 'Microsoft Enhanced RSA and AES Cryptographic Provider'
 New-SelfSignedCertificate -CertStoreLocation cert:\LocalMachine\My -DnsName "test2.contoso.com" -Signer $rootCert -KeyUsage KeyEncipherment,DigitalSignature
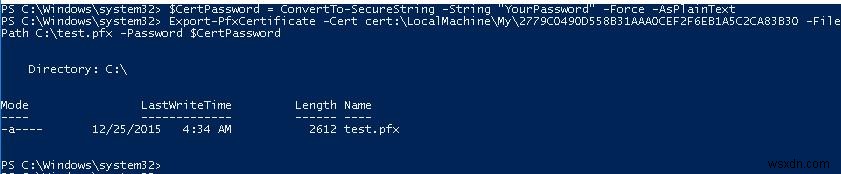
เพื่อส่งออก Certificate ที่สร้างขึ้นพร้อม Private Key ไปยังไฟล์ PFX ที่ป้องกันด้วยรหัสผ่าน คุณต้องระบุ Thumbprint ของมัน สามารถคัดลอกได้จากผลลัพธ์ของคำสั่ง New-SelfSignedCertificate คุณยังต้องระบุรหัสผ่านความปลอดภัยของ Certificate และแปลงเป็นรูปแบบ SecureString:
$CertPassword = ConvertTo-SecureString -String "YourPassword" -Force –AsPlainText
 Export-PfxCertificate -Cert cert:\LocalMachine\My\2779C7928D055B21AAA0Cfe2F6BE1A5C2CA83B30 -FilePath C:\test.pfx -Password $CertPassword
Public Key ของ Certificate สามารถส่งออกได้ดังนี้:
Export-Certificate -Cert Cert:\LocalMachine\My\2779C7928D055B21AAA0Cfe2F6BE1A5C2CA83B30 -FilePath C:\tstcert.cer
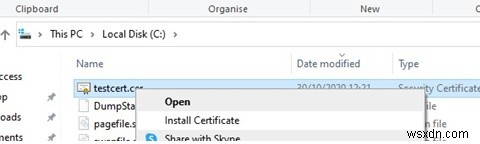
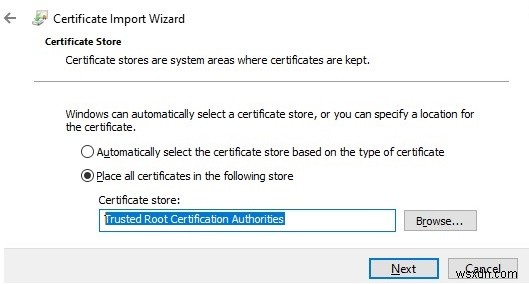
ตรวจสอบว่าไฟล์ *.cer (PFX) ปรากฏในไดเรกทอรีที่ระบุ หากคุณคลิกขวาที่มันและเลือกเมนู "Install Certificate" คุณสามารถใช้ Certificate Import Wizard เพื่อเพิ่ม Certificate ไปยัง Trusted Root Certificates บนคอมพิวเตอร์ของคุณ
เลือก Cert Store Location -> Local Machine, Place all certificates in the following store -> Trusted Root Certification Authorities
คุณสามารถสร้าง Certificate และนำเข้าไปยัง Trusted Root Certificate Store ของคอมพิวเตอร์ทันทีโดยใช้คำสั่ง:
$SelfSignCert=New-SelfSignedCertificate …..
 $certFile = Export-Certificate -Cert $SelfSignCert -FilePath C:\ps\export-certname.cer
 Import-Certificate -CertStoreLocation Cert:\LocalMachine\AuthRoot -FilePath $certFile.FullName
Public Key นี้หรือไฟล์ Certificate เองสามารถปรับใช้ไปยังคอมพิวเตอร์และเซิร์ฟเวอร์ทั้งหมดในโดเมน Active Directory โดยใช้ GPO (How to deploy certificates on domain computers using GPO?)
สร้าง Self-Signed Certificate พร้อม Subject Alternative Names
หนึ่งในฟีเจอร์ที่มีประโยชน์ของ Cmdlet New-SelfSignedCertificate คือความสามารถในการสร้าง Certificate พร้อมชื่อที่แตกต่างกันหลายชื่อ Subject Alternative Names (SAN)
หมายเหตุ เครื่องมือ Makecert.exe ไม่สามารถสร้าง SAN และ Wildcard Certificates ได้ ต่างจาก Cmdlet New-SelfSignedCertificate
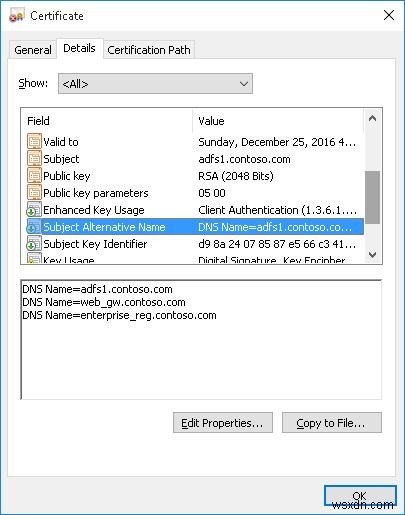
หากคุณต้องการสร้าง Certificate พร้อมหลายชื่อ ชื่อแรกของพารามิเตอร์ DnsName จะถูกใช้เป็น CN (Common Name) ของ Certificate ตัวอย่างเช่น มาสร้าง SAN Self-Signed Certificate พร้อมชื่อต่อไปนี้:
- Subject Name (CN): adfs1.contoso.com
- Subject Alternative Name (DNS): web_gw.contoso.com
- Subject Alternative Name (DNS): enterprise_reg.contoso.com
คำสั่งสำหรับการสร้าง Certificate จะมีลักษณะดังนี้:
New-SelfSignedCertificate -DnsName adfs1.contoso.com,web_gw.contoso.com,enterprise_reg.contoso.com -CertStoreLocation cert:\LocalMachine\My
นอกจากนี้ คุณยังสามารถสร้าง Wildcard Certificate สำหรับเนมสเปซโดเมนทั้งหมดได้ โดยระบุ *.contoso.com เป็นชื่อเซิร์ฟเวอร์
New-SelfSignedCertificate -certstorelocation cert:\localmachine\my -dnsname *.contoso.com
สร้าง Self-Signed Certificate สำหรับ Code Signing บน Windows
ใน PowerShell 3.0 Cmdlet New-SelfSignedCertificate สร้างเฉพาะ SSL Certificates ที่ไม่สามารถใช้เซ็นโค้ด Driver, Application หรือ Script ได้ (ต่างจาก Certificate ที่สร้างโดย MakeCert Utility)
ใน PowerShell เวอร์ชัน 5.0 และใหม่กว่า เวอร์ชันใหม่ของ Cmdlet New-SelfSignedCertificate สามารถใช้สร้าง Code Signing Certificates ได้แล้ว
เพื่อสร้าง Self-Signed Application Code Signing Certificate ให้รันคำสั่ง:
$cert = New-SelfSignedCertificate -Subject "My Code Signing Certificate" -Type CodeSigningCert -CertStoreLocation cert:\LocalMachine\My
ตอนนี้คุณสามารถเซ็น PowerShell Script ของคุณด้วย Self-Signed Certificate:
Set-AuthenticodeSignature -FilePath C:\PS\my_posh_script.ps1 -Certificate $cert
หากคุณได้รับคำเตือน UnknownError เมื่อรันคำสั่ง หมายความว่า Certificate ไม่ได้รับความไว้วางใจ เนื่องจากอยู่ใน Personal Certificate Store ของผู้ใช้
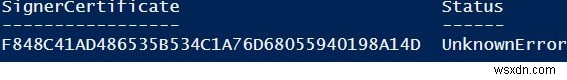
คุณต้องย้ายมันไปยัง Trusted Root Certificate Store (อย่าลืมสแกน Windows Certificate Root Store สำหรับ Certificate ที่ไม่ไว้วางใจและน่าสงสัยเป็นประจำ และอัปเดตรายการ Trusted Root Certificates)
Move-Item -Path $cert.PSPath -Destination "Cert:\CurrentUser\Root"
หลังจากนั้น คุณสามารถเซ็น PowerShell Script ของคุณด้วย Self-Signed Certificate นี้
การใช้ SHA-256 Self-Signed SSL Certificate ใน IIS บน Windows Server IIS
โปรดทราบว่าเมื่อสร้าง Self-Signed Certificate สำหรับ IIS ผ่านคอนโซล Internet Information Manager (Create Self-Signed Certificate เมนู Action) SSL Certificate จะถูกสร้างโดยใช้อัลกอริทึมการเข้ารหัส SHA-1 Certificate แบบนี้ถูกมองว่าไม่น่าเชื่อถือโดยเบราว์เซอร์หลายตัวและไม่สามารถใช้สร้างการเชื่อมต่อที่ปลอดภัยได้ (หรือคุณอาจเห็น SSL Errors อื่นๆ) Cmdlet New-SelfSignedCertificate อนุญาตให้คุณสร้างประเภท Certificate ที่นิยมมากกว่าที่ใช้ SHA-256 Encryption Algorithm
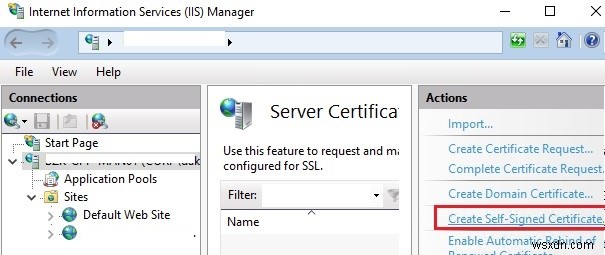
คุณสามารถผูก Self-Signed SHA-256 Certificate ที่สร้างด้วย PowerShell กับไซต์ IIS บน Windows Server หากคุณสร้าง SSL Certificate โดยใช้ PowerShell และวางไว้ใน Certificate Store ของคอมพิวเตอร์ มันจะพร้อมใช้งานสำหรับไซต์ IIS โดยอัตโนมัติ
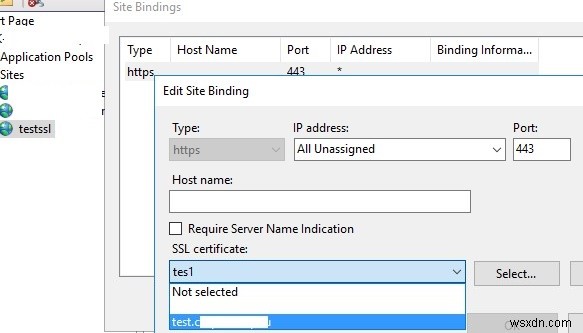
เริ่มคอนโซล IIS Manager เลือกไซต์ของคุณ และในตัวเลือก Site Binding ให้เลือก Certificate ที่คุณสร้างและบันทึกการเปลี่ยนแปลง
