

(User Account Control) เป็นองค์ประกอบสำคัญของความปลอดภัย Windows เมื่อคุณรันแอปพลิเคชันหรือกระบวนการใดๆ ที่ต้องการสิทธิ์ Administrator พยายามเปลี่ยนการตั้งค่าระบบ Registry Keys ที่ได้รับการป้องกัน หรือไฟล์ระบบ องค์ประกอบ UAC จะสลับ Desktop ไปโหมดที่ได้รับการป้องกัน (Secure Desktop) และขอการยืนยันจาก Administrator สำหรับการดำเนินการเหล่านี้ ด้วยวิธีนี้ UAC ช่วยป้องกันการเปิดตัวของกระบวนการและมัลแวร์ที่อาจทำลายคอมพิวเตอร์ของคุณ
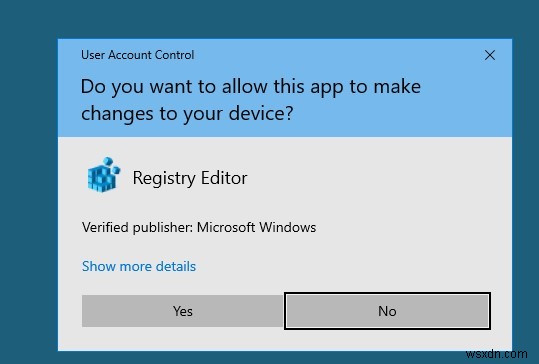
ภาพหน้าจอด้านล่างแสดงว่าเมื่อพยายามรัน Registry Editor (regedit.exe) บน Windows 10 หน้าต่างยืนยัน UAC จะปรากฏ:
User Account Control Do you want to allow this app to make changes to your device?
UAC ไม่ได้เปิดใช้งานสำหรับ Built-in Administrator Account ซึ่งถูก Disable โดย Default ใน Windows 10
ในบทความนี้ เราจะดูวิธีจัดการการตั้งค่า UAC บนคอมพิวเตอร์เครื่องเดียว หรือหลายเครื่องในโดเมนโดยใช้ Group Policies
ระดับ Slider ของ User Account Control บน Windows 10
ใน Windows 7 (และใหม่กว่า) การตั้งค่า UAC บนคอมพิวเตอร์จัดการได้โดย Slider พิเศษ (เรียกผ่าน Control Panel หรือไฟล์ UserAccountControlSettings.exe) โดยใช้ Slider คุณสามารถเลือกหนึ่งใน 4 ระดับการป้องกัน User Account Control ที่กำหนดไว้ล่วงหน้า
- Level 4 — Always notify — ระดับการป้องกัน UAC สูงสุด;
- Level 3 — Notify only when programs try to make changes to my computer (default) – ระดับการป้องกัน Default;
- Level 2 — Notify only when programs try to make changes to my computer (do not dim my desktop) – เกือบเหมือนระดับก่อนหน้า แต่ไม่สลับไป Secure Desktop พร้อมล็อก Desktop;
- Level 1 — Never notify – ปิด UAC
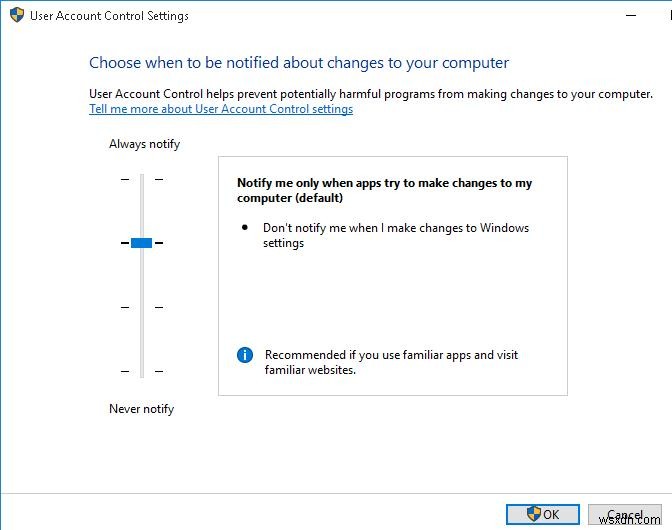
โดย Default ใน Windows 10 ใช้การป้องกัน UAC Level 3 ซึ่งแสดงการแจ้งเตือนเฉพาะเมื่อคุณพยายามเปลี่ยนไฟล์ระบบหรือการตั้งค่า
วิธีปิด User Account Control ใน Windows โดยใช้ GPO
ในส่วนใหญ่ ไม่แนะนำให้ปิด UAC อย่างสมบูรณ์ User Account Control เป็นเครื่องมือความปลอดภัย Windows ที่เรียบง่ายแต่อย่างมีประสิทธิภาพ ในทางปฏิบัติของผม ผมไม่เคยปิด UAC บนคอมพิวเตอร์ของผู้ใช้โดยไม่แน่ใจว่า UAC บล็อกฟังก์ชันบางอย่าง แม้ในกรณีเหล่านี้ ก็มีวิธีแก้ไขง่ายๆ เพื่อปิด UAC สำหรับแอปพลิเคชันเฉพาะ หรือรันแอปโดยไม่มีสิทธิ์ Admin และปิด UAC Prompt
คุณสามารถปิด UAC โดยใช้ Group Policy บนคอมพิวเตอร์ Standalone คุณสามารถใช้ Local Group Policy Editor gpedit.msc หากคุณต้อง Deploy Policy ไปยัง Domain Computers คุณต้องใช้ Group Policy Management Console – gpmc.msc (มาพิจารณาตัวเลือกนี้)
- ใน Domain GPO Management Console คลิกที่ OU ที่มีคอมพิวเตอร์ที่คุณต้องการปิด UAC และสร้าง Policy Object ใหม่;
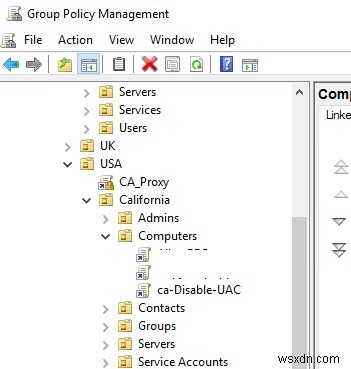
- แก้ไข Policy และไปที่ส่วน Computer Configuration -> Policies -> Windows Settings -> Security Settings -> Local Policies -> Security Options;
- ส่วนนี้มีตัวเลือกหลายอย่างที่ควบคุมการตั้งค่า UAC ชื่อของพารามิเตอร์เหล่านี้ขึ้นต้นด้วย User Account Control;
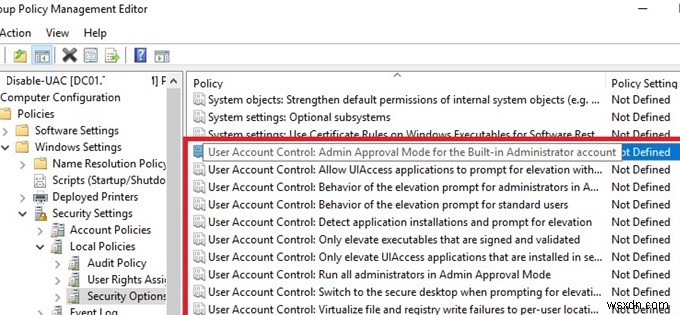
- เพื่อปิด UAC อย่างสมบูรณ์ ให้ตั้งค่าพารามิเตอร์ดังต่อไปนี้:
- User Account Control: Behavior of the elevation prompt for administrators in Admin Approval Mode =
Elevate without prompting; - User Account Control: Detect application installations and prompt for elevation =
Disabled; - User Account Control: Run all administrators in Admin Approval Mode =
Disabled; - User Account Control: Only elevate UIAccess applications that are installed in secure locations =
Disabled.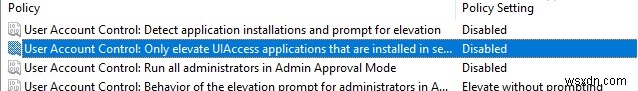
- User Account Control: Behavior of the elevation prompt for administrators in Admin Approval Mode =
- คุณต้อง Restart Client Computer เพื่ออัปเดตการตั้งค่า Group Policy และปิด UAC หลัง Reboot UAC จะเปลี่ยนไปโหมด "Never notify"
คุณยังสามารถปิด UAC เฉพาะบาง User/Computers ผ่าน Registry และ Deploy การตั้งค่าผ่าน Group Policy Preferences ได้
สร้าง Registry Parameter ใหม่ภายใต้ส่วน GPO Computer Configuration -> Preferences -> Windows Settings -> Registry ด้วยการตั้งค่าต่อไปนี้:
- Action: Replace
- Hive: HKEY_LOCAL_MACHINE
- Key Path: SOFTWARE\Microsoft\Windows\CurrentVersion\Policies\System
- Value name: EnableLUA
- Value type: REG_DWORD
- Value data: 0
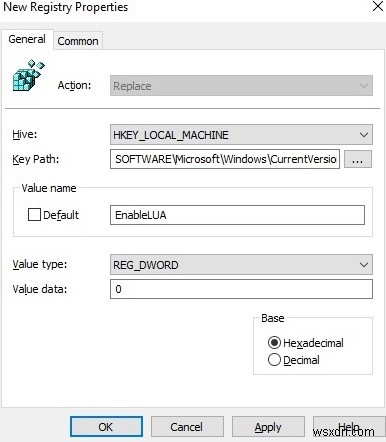
จากนั้นไปที่แท็บ Common และเปิดใช้งานตัวเลือก:
- Remove this item when it is no longer applied
- Item-Level targeting
คลิกปุ่ม Targeting และระบุคอมพิวเตอร์หรือกลุ่มความปลอดภัยโดเมนที่คุณต้องการนำ Policy ปิด UAC ไปใช้
แม้ UAC จะถูกปิด แอปบางอย่างอาจยังถูกบล็อกจากการ Launch พร้อมข้อความ This app has been blocked for your protection.
การตั้งค่า UAC Registry Key
คุณสามารถจัดการการตั้งค่า UAC ผ่าน Registry พารามิเตอร์ที่รับผิดชอบพฤติกรรมของ User Account Control อยู่ภายใต้ Registry Key HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Policies\System
เมื่อคุณเปลี่ยนค่าของ UAC Slider ใน Control Panel Windows จะเปลี่ยนค่าการตั้งค่า Registry จาก Reg Key นี้ดังนี้ (ด้านล่างคือไฟล์ REG สำเร็จรูปสำหรับระดับต่างๆ ของ UAC Slider):
UAC Level 4 (Always notify):
Windows Registry Editor Version 5.00 [HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Policies\System] "ConsentPromptBehaviorAdmin"=dword:00000002 "ConsentPromptBehaviorUser"=dword:00000003 "EnableInstallerDetection"=dword:00000001 "EnableLUA"=dword:00000001 "EnableVirtualization"=dword:00000001 "PromptOnSecureDesktop"=dword:00000001 "ValidateAdminCodeSignatures"=dword:00000000 "FilterAdministratorToken"=dword:00000000
UAC Level 3 (Notify only when programs try to make changes to my computer):
"ConsentPromptBehaviorAdmin"=dword:00000005 "ConsentPromptBehaviorUser"=dword:00000003 "EnableInstallerDetection"=dword:00000001 "EnableLUA"=dword:00000001 "EnableVirtualization"=dword:00000001 "PromptOnSecureDesktop"=dword:00000001 "ValidateAdminCodeSignatures"=dword:00000000 "FilterAdministratorToken"=dword:00000000
UAC Level 2:
"ConsentPromptBehaviorAdmin"=dword:00000005 "ConsentPromptBehaviorUser"=dword:00000003 "EnableInstallerDetection"=dword:00000001 "EnableLUA"=dword:00000001 "EnableVirtualization"=dword:00000001 "PromptOnSecureDesktop"=dword:00000000 "ValidateAdminCodeSignatures"=dword:00000000 "FilterAdministratorToken"=dword:00000000
UAC Level 1 (Never notify — ปิด UAC อย่างสมบูรณ์):
"ConsentPromptBehaviorAdmin"=dword:00000000 "ConsentPromptBehaviorUser"=dword:00000003 "EnableInstallerDetection"=dword:00000001 "EnableLUA"=dword:00000001 "EnableVirtualization"=dword:00000001 "PromptOnSecureDesktop"=dword:00000000 "ValidateAdminCodeSignatures"=dword:00000000 "FilterAdministratorToken"=dword:00000000
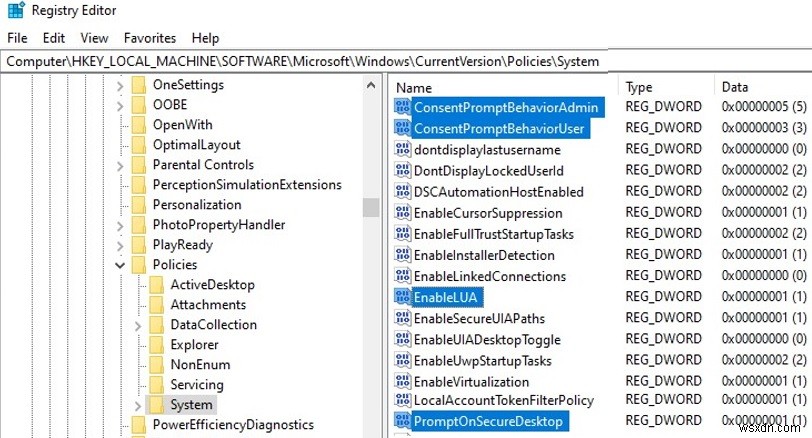
คุณสามารถเปลี่ยนค่าของพารามิเตอร์ใดๆ โดยใช้ Registry Editor GUI หรือจาก Command Prompt ตัวอย่างเช่น เพื่อปิด UAC บนคอมพิวเตอร์ (ต้อง Reboot) คุณสามารถรันคำสั่ง:
reg.exe ADD HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Policies\System /v EnableLUA /t REG_DWORD /d 0 /f.
หรือคำสั่ง PowerShell ที่คล้ายกัน:
New-ItemProperty -Path HKLM:Software\Microsoft\Windows\CurrentVersion\policies\system -Name EnableLUA -PropertyType DWord -Value 0 -Force
มี Registry Parameter อีกตัวหนึ่งในเธรดนี้ LocalAccountTokenFilterPolicy ซึ่งมักถูกเรียกว่า Remote UAC พารามิเตอร์นี้จำกัดการเชื่อมต่อ Remote ไปยัง Default Administrative Shares ภายใต้ Local User Accounts ที่มีสิทธิ์ Administrator
User Account Control บน Windows Server
User Account Control ใน Windows Server ทำงานและจัดการได้ในลักษณะเดียวกับบน Windows Desktop Editions
ยอมรับได้ที่จะปิด UAC อย่างสมบูรณ์ใน Windows Server 2016/2019 หากเงื่อนไขต่อไปนี้เป็นจริง:
- มีเฉพาะ Administrators ที่มี Remote Access ไปยัง Server Desktop (RDP Access ไปยัง Server สำหรับ Non-Admin Users ต้อง Disable) บน RDS Hosts ให้เปิด UAC ไว้;
- Administrators ควรใช้ Windows Server สำหรับ Administrative Management Tasks เท่านั้น Administrator ควรทำงานกับเอกสาร Office, Messengers, Web Browsers เฉพาะบน Workstation ภายใต้ Non-Privileged User Account ที่มี UAC เปิดอยู่ ไม่ใช่บน Server Hosts (ตรวจสอบบทความ Best Practices สำหรับการรักษาความปลอดภัยบัญชี Administrator)
UAC ถูกปิดเสมอใน Windows Server Core Editions
เมื่อ UAC เปิดอยู่ Windows Server ไม่อนุญาตให้เชื่อมต่อ Remote ภายใต้ Local Computer Accounts (ผ่าน net use, winrm, Powershell Remoting) Token ของผู้ใช้จะถูก Filter โดย UAC Parameter LocalAccountTokenFilterPolicy ที่เปิดใช้งาน (อภิปรายในส่วนก่อนหน้า)
UAC Slider และการตั้งค่า Group Policy
คุณสามารถจัดการการตั้งค่า UAC ทั้งด้วย Slider และ GPO แต่ไม่มีพารามิเตอร์ Group Policy เดียวที่อนุญาตให้เลือกหนึ่งใน 4 ระดับการป้องกัน UAC (ตรงกับตำแหน่งของ UAC Slider) แนะนำให้จัดการการตั้งค่า UAC โดยใช้ GPO Parameters 10 ตัวแทน นโยบายเหล่านี้อยู่ในส่วนต่อไปนี้ของ GPO Editor: Computer Configuration -> Policies -> Windows Settings -> Security Settings -> Local Policies -> Security Options พารามิเตอร์ GPO ที่เกี่ยวข้องกับ UAC เริ่มต้นด้วย User Account Control
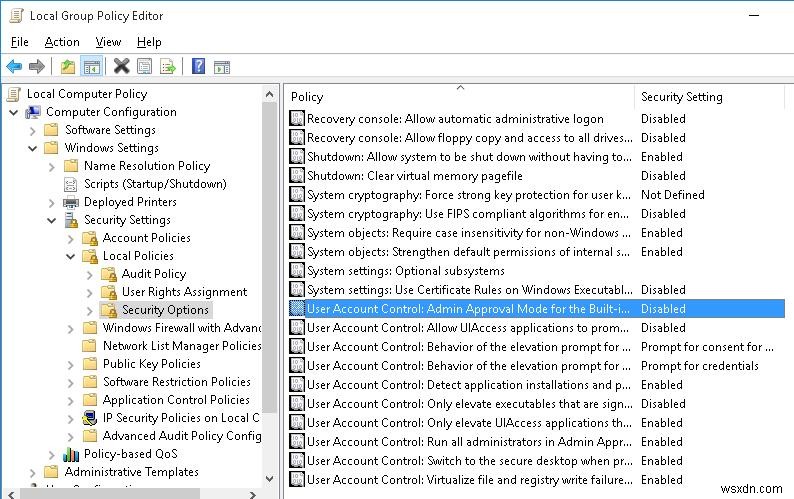
ตารางต่อไปนี้แสดงรายการพารามิเตอร์ UAC Group Policy และ Registry Keys ที่สอดคล้องกัน
| Policy Name | Registry Parameter Set by the Policy |
| User Account Control: Admin Approval Mode for the Built-in Administrator account | FilterAdministratorToken |
| User Account Control: Allow UIAccess applications to prompt for elevation without using the secure desktop | EnableUIADesktopToggle |
| User Account Control: Behavior of the elevation prompt for administrators in Admin Approval Mode | ConsentPromptBehaviorAdmin |
| User Account Control: Behavior of the elevation prompt for standard users | ConsentPromptBehaviorUser |
| User Account Control: Detect application installations and prompt for elevation | EnableInstallerDetection |
| User Account Control: Only elevate executables that are signed and validated | ValidateAdminCodeSignatures |
| User Account Control: Only elevate UIAccess applications that are installed in secure locations | EnableSecureUIAPaths |
| User Account Control: Run all administrators in Admin Approval Mode | EnableLUA |
| User Account Control: Switch to the secure desktop when prompting for elevation | PromptOnSecureDesktop |
| User Account Control: Virtualize file and registry write failures to per-user locations | EnableVirtualization |
โดย Default UAC Level 3 ใช้การตั้งค่า Group Policy ดังต่อไปนี้:
UAC Level 3 (Default)
Admin Approval Mode for the Built-in Administrator account = Disabled
Allow UIAccess applications to prompt for elevation without using the secure desktop = Disabled
Behavior of the elevation prompt for administrators in Admin Approval Mode = Prompt for consent for non-Windows binaries
Behavior of the elevation prompt for standard users = Prompt for credentials on the secure desktop
Detect application installations and prompt for elevation = Enabled (สำหรับ Workgroup), Disabled (สำหรับ Domain-joined Windows Device)
Only elevate executables that are signed and validated = Disabled
Only elevate UIAccess applications that are installed in secure locations = Enabled
Run all administrators in Admin Approval Mode = Enabled
Switch to the secure desktop when prompting for elevation = Enabled
Virtualize file and registry write failures to per-user locations = Enabled
