

ฟังก์ชัน Multi-user ใน Windows ทำให้ใช้งานสะดวกในสถานที่สาธารณะ เช่น โรงเรียน, มหาวิทยาลัย, สำนักงาน ที่มักมี Administrator ดูแลกิจกรรมผู้ใช้ บางครั้งผู้ใช้ทำเกินขอบเขตและแก้ไขบัญชีที่ตั้งค่าในโหมด Workgroup อาจมีผลกระทบด้านความปลอดภัย จึงควรกำหนดค่า Windows ให้ติดตามกิจกรรมผู้ใช้
ด้วยการกำหนดค่า Windows สำหรับติดตามกิจกรรมผู้ใช้ เราสามารถเพิ่มความปลอดภัยของการบริหารจัดการ และลงโทษผู้ใช้ที่ผิดได้จากบันทึกในกรณีมีความผิด บทความนี้จะแจ้งวิธีติดตามกิจกรรมผู้ใช้ใน Windows 11/10/8.1/8/7 ด้วย Audit Policy ดังนี้:
ติดตามกิจกรรมผู้ใช้ด้วย Audit Policy ในโหมด WorkGroup
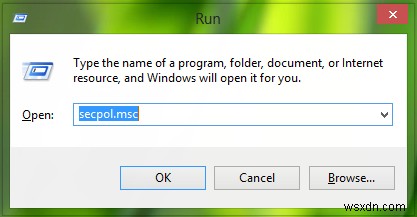
1. กด Windows Key + R พิมพ์ secpol.msc ใน Run กด Enter เปิด Local Security Policy
2. ในหน้าต่าง Local Security Policy ขยาย Security Settings > Local Policies > Audit Policy จะได้หน้าต่างคล้ายนี้:
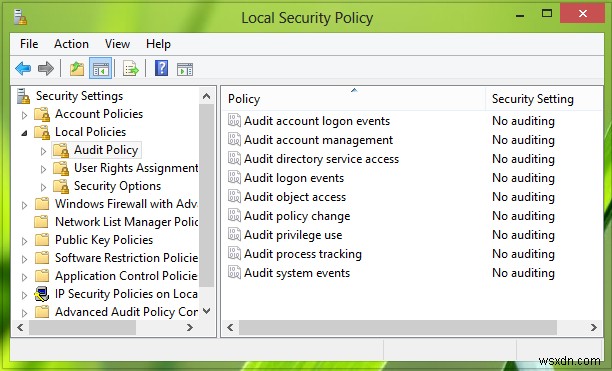
3. ใน Fruit pane ด้านขวาเห็น 9 นโยบาย Audit…[] มี No auditing เป็น pre-defined security setting คลิกทีละนโยบาย เลือก Success และ Failure คลิก Apply ตามด้วย OK ทุกนโยบาย
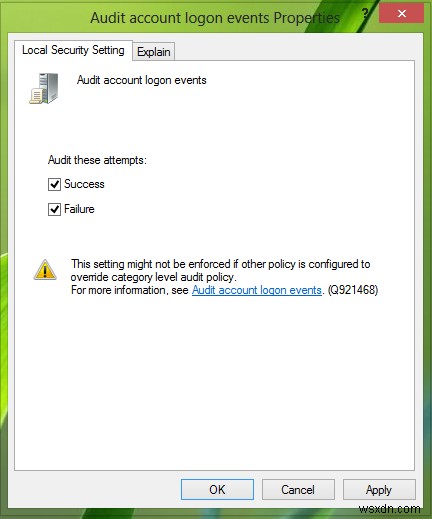
เช่นนี้เราจะตั้งค่า Windows ให้ติดตามกิจกรรมผู้ใช้
ทำตามขั้นตอนเพื่อดูบันทึกที่ติดตาม:
ติดตามกิจกรรมผู้ใช้ด้วย Event Viewer
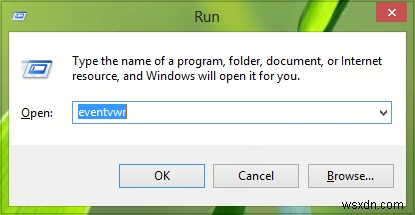
1. กด Windows Key + R พิมพ์ eventvwr ใน Run กด Enter เปิด Event Viewer
2. ในหน้าต่าง Event Viewer จากแผงซ้าย เลือก Windows Logs > Security Windows เก็บบันทึกทุกเหตุการณ์ด้านความปลอดภัย
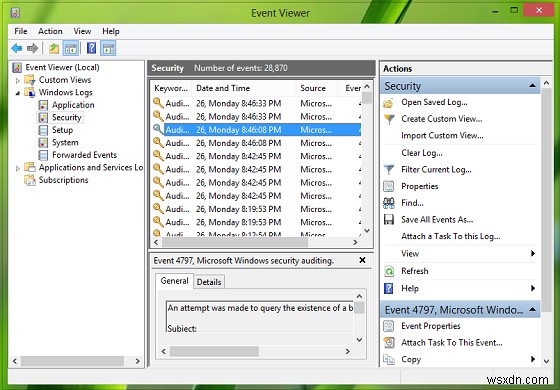
3. จากแผงกลาง คลิกเหตุการณ์ใดก็ได้เพื่อดูรายละเอียด:
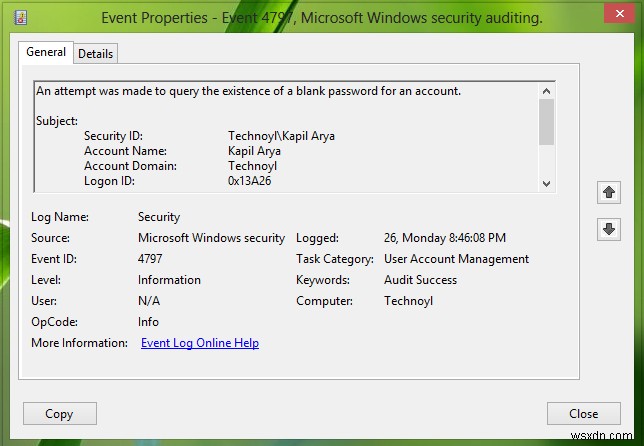
นี่คือรายการ Event IDs ที่ครอบคลุมกิจกรรมผู้ใช้สำหรับบัญชีในโหมด Workgroup:
1. Create User: Event IDs ที่บันทึกเมื่อสร้างผู้ใช้
- Event ID: 4728 | Type: Audit Success | Category: Security Group Management | Description: เพิ่มสมาชิกใน Security-enabled global group
- Event ID: 4720 | Type: Audit Success | Category: User Account Management | Description: สร้าง User account
- Event ID: 4722 | Type: Audit Success | Category: User Account Management | Description: เปิดใช้งาน User account
- Event ID: 4738 | Type: Success Audit | Category: User Account Management | Description: เปลี่ยนแปลง User account
- Event ID: 4732 | Type: Success Audit | Category: Security Group Management | Description: เพิ่มสมาชิกใน Security-enabled local group
2. Delete User: Event IDs เมื่อลบผู้ใช้
- Event ID: 4733 | Type: Success Audit | Category: Security Group Management | Description: ลบสมาชิกจาก Security-enabled local group
- Event ID: 4729 | Type: Success Audit | Category: Security Group Management | Description: เพิ่มสมาชิกใน Security-enabled global group
- Event ID: 4726 | Type: Success Audit | Category: User Account Management | Description: ลบ User account
3. User Account Disabled: Event IDs เมื่อปิดใช้งานผู้ใช้
- Event ID: 4725 | Type: Success Audit | Category: User Account Management | Description: ปิดใช้งาน User account
- Event ID: 4738 | Type: Success Audit | Category: User Account Management | Description: เปลี่ยนแปลง User account
4. User Account Enabled: Event IDs เมื่อเปิดใช้งานผู้ใช้
- Event ID: 4722 | Type: Success Audit | Category: User Account Management | Description: เปิดใช้งาน User account
- Event ID: 4738 | Type: Success Audit | Category: User Account Management | Description: เปลี่ยนแปลง User account
5. User Account Password Reset: Event IDs เมื่อรีเซ็ตรหัสผ่าน
- Event ID: 4738 | Type: Success Audit | Category: User Account Management | Description: เปลี่ยนแปลง User account
- Event ID: 4724 | Type: Success Audit | Category: User Account Management | Description: พยายามรีเซ็ตรหัสผ่านบัญชี
6. User Account Profile Path Set: Event ID เมื่อตั้งค่า Profile Path
- Event ID: 4738 | Type: Success Audit | Category: User Account Management | Description: เปลี่ยนแปลง User account
7. User Account Rename: Event IDs เมื่อเปลี่ยนชื่อผู้ใช้
- Event ID: 4781 | Type: Success Audit | Category: User Account Management | Description: เปลี่ยนชื่อบัญชี
- Event ID: 4738 | Type: Success Audit | Category: User Account Management | Description: เปลี่ยนแปลง User Account
8. Create Local Group: Event IDs เมื่อสร้าง Local Group
- Event ID: 4731 | Type: Success Audit | Category: Security Group Management | Description: สร้าง Security-enabled local group
- Event ID: 4735 | Type: Success Audit | Category: Security Group Management | Description: เปลี่ยนแปลง Security-enabled local group
9. Add User to Local Group: Event ID เมื่อเพิ่มผู้ใช้ใน Local group
- Event ID: 4732 | Type: Success Audit | Category: Security Group Management | Description: เพิ่มสมาชิกใน Security-enabled local group
10. Remove User from Local Group: Event ID เมื่อลบผู้ใช้จาก Local group
- Event ID: 4733 | Type: Success Audit | Category: Security Group Management | Description: ลบสมาชิกจาก Security-enabled local group
11. Delete Local Group: Event ID เมื่อลบ Local Group
- Event ID: 4734 | Type: Success Audit | Category: Security Group Management | Description: ลบ Security-enabled local group
12. Rename Local Group: Event IDs เมื่อเปลี่ยนชื่อ Local Group
- Event ID: 4781 | Type: Success Audit | Category: User Account Management | Description: เปลี่ยนชื่อบัญชี
- Event ID: 4735 | Type: Success Audit | Category: Security Group Management | Description: เปลี่ยนแปลง Security-enabled local group
ด้วยวิธีนี้ สามารถติดตามผู้ใช้กับกิจกรรมของพวกเขาได้ บทความนี้ใช้ได้กับ Windows 11/10/8.1 ในโหมด Workgroup สำหรับ Active Directory Domain ขั้นตอนจะต่างออกไป
