

การจับแพ็กเก็ต (Packet Capture) เป็นวิธีที่มีประโยชน์มากในการวิเคราะห์การทำงานภายในของ Network มี Tools หลากหลายที่พัฒนาขึ้นมาเพื่อวัตถุประสงค์นี้ หนึ่งในนั้นคือ tcpdump ที่นี่เราจะแสดงวิธีใช้ Tool ยอดเยี่ยมนี้สำหรับ Network Engineers และ Penetration Testers
tcpdump คืออะไร?
tcpdump เป็น Network Packet Analyzer Tool ที่พัฒนาและ Release ในปี 1988 โดยทีม Computer Scientists ที่ Lawrence Berkeley Laboratory และ Network Research Group ใช้แสดง Contents ของ Packets ที่ Computer ส่งและรับ Utility มาพร้อม Options หลากหลาย ทำให้ Packet Capture Specific และ Focused มากขึ้น Options บางอย่างรวม Different Networking Protocols และ Network Interfaces
Installation
Linux Distributions หลายตัวมาพร้อม Utility ติดตั้ง Out of the Box อย่างไรก็ตาม ถ้า Distro ที่เลือกไม่มี Installation ก็ Quick และ Simple
ถ้าใช้ Ubuntu หรือ Debian ติดตั้งด้วย apt:
sudo apt install tcpdump
บน CentOS ทำเหมือนกันด้วย yum:
sudo yum install tcpdump
และบน Arch Linux ด้วย pacman:
sudo pacman -S tcpdump
The Basics
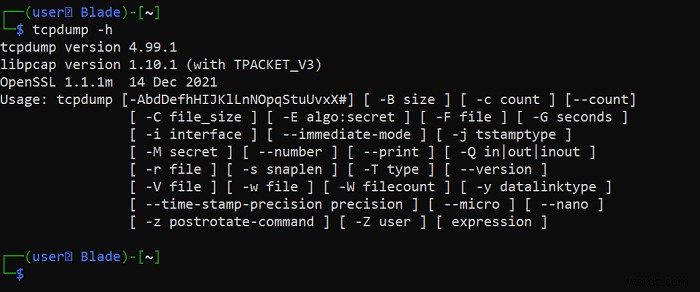
ติดตั้ง tcpdump แล้ว คุณสามารถดู Manual ด้วย Flag -h:
tcpdump -h
แสดง List ของ Flags ที่ใช้ได้กับ Tool
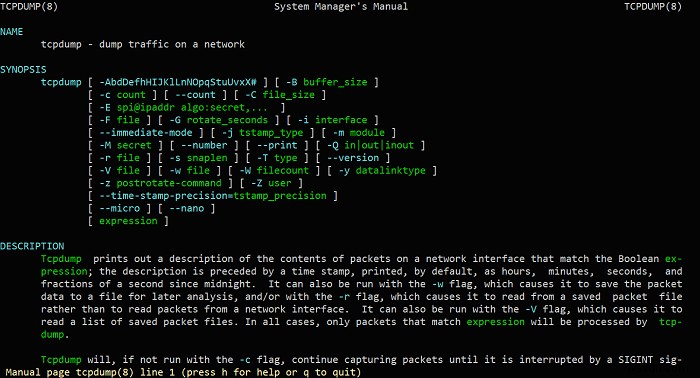
ถ้าอยากดู Manual ที่ Comprehensive และ Detailed มากกว่า ใช้ man Command:
man tcpdump
คุณสามารถ Run Basic Packet Capture ด้วยการพิมพ์:
tcpdump
ใช้ Command เพียงตัวมันโดยไม่ Specify Network Interface Tool จะเลือกหนึ่งจาก Available Interfaces บน System
ถ้าไม่อยากให้ tcpdump Resolve Hostnames และอยาก Output แค่ IP Addresses ใช้ Flag -n:
tcpdump -n
ถ้าอยาก Specify จำนวน Packets ที่ต้องการ Capture ใช้ Flag -c:
tcpdump -c [number of packets]
ระบุ Network Interface
คุณสามารถระบุ Network Interface ที่ต้องการด้วย Flag -i:
tcpdump -i [interface]
Network Interface Names ที่พบบ่อยที่สุดบน System ส่วนใหญ่คือ eth0 และ wlan0:
tcpdump -i eth0 tcpdump -i wlan0
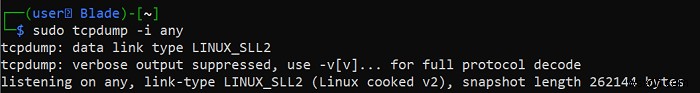
ถ้าอยาก Capture Data บน All Interfaces ใช้ Option any:
tcpdump -i any
ระบุ Port/Port Range
ถ้าอยาก Capture Data ที่ใช้ Port Number เฉพาะ ใช้คำสั่ง:
tcpdump -i [interface] port [port number]
สมมติอยาก Capture Traffic บน Interface eth0 และ Port 443 (HTTPS) พิมพ์:
tcpdump -i eth0 port 443
เพิ่มเติม tcpdump อนุญาตให้ Specify Port Range:
tcpdump -i [interface] portrange [port range]
ระบุ Host หรือ Subnet
จะมีคราวที่อยาก Limit Captured Packets เฉพาะที่ Sent/Received จาก Host หรือ Subnet เฉพาะ โชคดีที่ tcpdump อนุญาต
คุณสามารถระบุ Host ได้ด้วย Format:
tcpdump -i [interface] host [host]
ตัวอย่าง Capture Traffic บน eth0 และ Specify Host เป็น 127.0.0.1 (Loopback IP ของคุณ):
tcpdump -i eth0 host 127.0.0.1
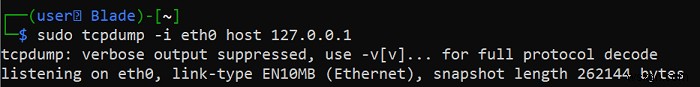
ถ้าอยากระบุ Network Subnet ด้วย CIDR Notation ใช้ Format:
tcpdump -i [interface] net [subnet]
ตัวอย่าง:
tcpdump -i eth0 net 10.0.0.0/8
คุณยังระบุ Source Host โดยตรงได้:
tcpdump -i [interface] src [host]
และ Destination Host:
tcpdump -i [interface] dst [host]
ระบุ Verbosity
tcpdump ให้ Specify Verbosity ของ Packet Capture นี่ Very Useful เมื่อไม่อยาก Overwhelmed โดย Information Amount ระหว่าง Capture
มี 3 Incremental Options สำห Verbosity Flags -v, -vv และ -vvv:
tcpdump -i [interface] -v tcpdump -i [interface] -vv tcpdump -i [interface] -vvv

Option แรก Specify Least Verbosity Option ที่สาม Specify Most
บันทึก Capture ลง File
มัก Useful ที่จะ Save Captured Data ไป File เพื่อ Analyze และ Interpret ต่อ
ทำได้ด้วย Flag -w:
tcpdump -i [interface] -w [filename]
ตัวอย่าง Save Captured Data ไป File "capture.txt":
tcpdump -i eth0 -w capture.txt
Frequently Asked Questions
1. ได้ Error "Operation not permitted" แก้ยังไง?
Error ทั่วไปที่ User อาจได้เมื่อลองใช้ tcpdump:
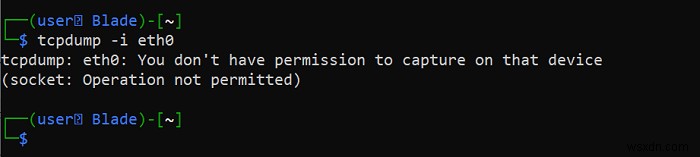
tcpdump ให้ Error นี้เมื่อคุณไม่มี Permissions จำเป็นสำหรับ Packet Capture ใน Most Scenarios แก้ได้โดยใช้ sudo ตัวอย่าง:
sudo tcpdump -i eth0
2. รู้ยังไงว่า Network Interfaces ไหน Available?
tcpdump มี Built-in Functionality Check Available Network Interfaces บน System
เช็ค Interfaces ใช้ Flag -D:
tcpdump -D
