

กระบวนการ Generate SSL/TLS Certificates เป็น Common Task สำหรับ Linux System Administrators หลายคน โชคดีที่แม้คุณจะไม่ใช่ Admin ก็ทำได้ง่ายด้วย OpenSSL Open-source Tool ที่ติดตั้ง Default บน Linux Distributions หลายตัว ที่นี่เราอธิบาย OpenSSL คืออะไร การติดตั้ง และสำคัญที่สุด การใช้สร้าง SSL และ TLS Certificates บน System
OpenSSL คืออะไร?
OpenSSL เป็น Library ที่พัฒนาโดย OpenSSL Project เพื่อ Provide Open-source SSL และ TLS Implementations สำหรับ Encryption ของ Network Traffic พร้อมใช้สำหรับ Unix-based Distributions หลากหลาย และใช้ Generate Certificates, RSA Private Keys, และทำ General Cryptography-related Tasks ได้
ข้อจำกัดของ Self-signed SSL Certificate
เมื่อใช้ OpenSSL Generate SSL Certificate ถือว่า "Self-signed" หมายความว่า SSL Certificate ถูก Sign ด้วย Private Key ของมันเอง ไม่ใช่จาก Certificate Authority (CA)
ดังนั้น SSL Certificate ไม่สามารถ "Trusted" ได้ และไม่ควรใช้สำหรับ Public-facing Sites หากใช้ Users จะเห็น Warnings จาก Browsers เกี่ยวกับ Certificate
Self-signed Certificate Useful สำหรับ Local Development หรือ Apps ที่รันใน Background ไม่ Face Internet
ทางเลือกอื่น ใช้ LetsEncrypt หรือได้ Certificate ที่ Verified โดย Trusted Authority อย่าง Comodo CA
Installation
Linux Distributions ส่วนใหญ่มี OpenSSL Version หนึ่ง Built-in Default แล้ว ถ้าไม่มี ติดตั้งได้ง่าย
ติดตั้งบน Ubuntu และ Debian ด้วย apt:
sudo apt install openssl
บน CentOS (หรือ Alternative) ติดตั้งด้วย yum:
sudo yum install openssl
คุณยัง Download ได้ง่ายจาก Website เป็น File ".tar.gz"
Basic Usage
ตอนนี้ OpenSSL Installed แล้ว มาดู Basic Functions บางอย่างที่ Program Provide
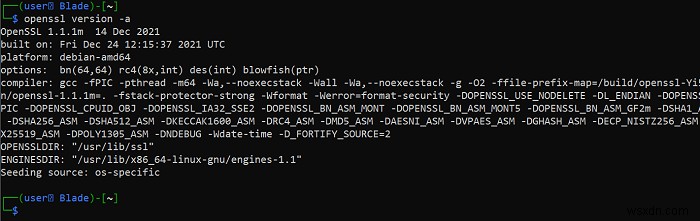
เริ่มด้วย View Version และ Info อื่นๆ ของ OpenSSL Installation:
openssl version -a
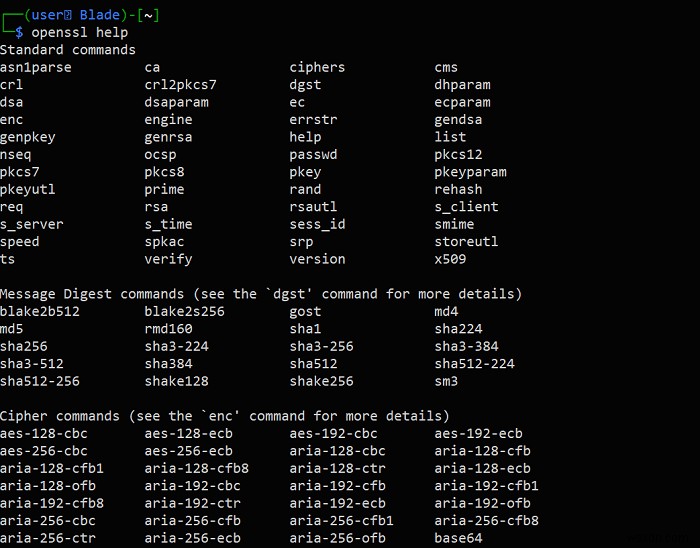
Check Out Manual ที่ Provide:
openssl help
Generate Certificate ด้วย Configuration File
Generate Certificate ด้วย OpenSSL Possible หลายวิธี หนึ่งคือใช้ Configuration File ระบุ Details เกี่ยวกับ Organization
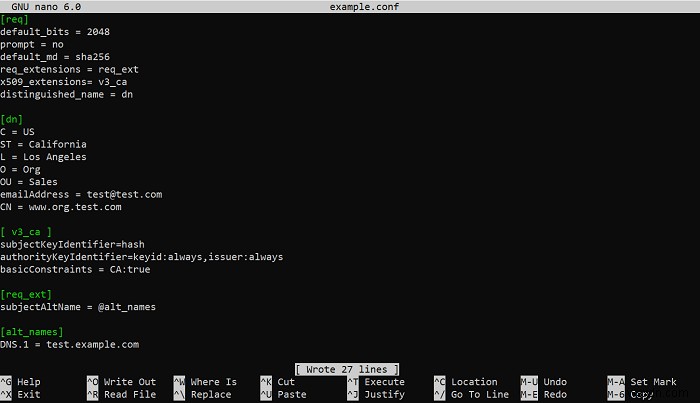
เริ่มด้วยสร้าง Config File ชื่อ "config.conf" และ Edit ด้วย Nano:
sudo nano example.conf
นี่คือ Example เนื้อหา Config File:
[req] default_bits = 2048 prompt = no default_md = sha256 req_extensions = req_ext x509_extensions= v3_ca distinguished_name = dn [dn] C = US ST = California L = Los Angeles O = Org OU = Sales emailAddress = test@test.com CN = www.org.test.com [ v3_ca ] subjectKeyIdentifier=hash authorityKeyIdentifier=keyid:always,issuer:always basicConstraints = CA:true [req_ext] subjectAltName = @alt_names [alt_names] DNS.1 = test.example.com
คุณ Copy และ Paste เข้าไฟล์ และทำ Necessary Changes ให้สะท้อน Organization Info ของคุณ
ต่อไป ต้อง Generate RSA Private Key ซึ่งจะใช้ Generate Root Certificate:
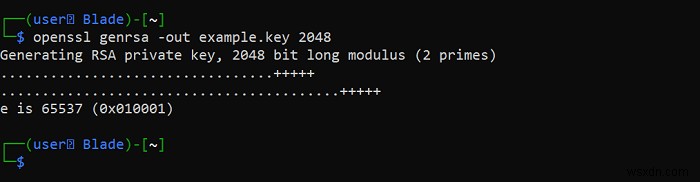
openssl genrsa -out example.key 2048
Flag -out ใช้ Specify Name ของ Key ที่จะ Generate Key Size 2048 Bits ระบุไว้ ซึ่งเป็น Default สำหรับ RSA Keys
คุณยังต้อง Generate Certificate Signing Request (CSR):
openssl req -new -key example.key -out example.csr -config example.conf
ในกรณีนี้ Flag -key Specify RSA Key, -out Specify CSR Filename และ -config Specify Config Filename
หลังจากนี้ Generate Root Certificate ซึ่งใช้ Generate Final Certificate:
openssl req -x509 -sha256 -nodes -new -key example.key -out example.crt -config example.conf
ในกระบวนการ Generate Root Certificate Flag -sha256 ใช้ Specify SHA256 เป็น Message Digest
ตอนนี้ Step สุดท้าย เราสามารถพิมพ์คำสั่งต่อไปนี้เพื่อ Generate Certificate:
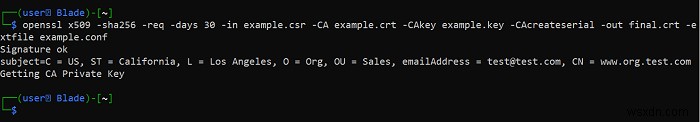
openssl x509 -sha256 -CAcreateserial -req -days 30 -in example.csr -extfile example.conf -CA example.crt -CAkey example.key -out final.crt
Flag -CA Specify Root Certificate, -CAkey Specify Private Key และ -extfile Specify Config Filename ไฟล์ "final.crt" จะเป็น SSL Certificate ที่คุณต้องการ
Generate Certificate โดยไม่ใช้ Configuration File
ทางเลือกอื่น คุณ Generate Certificate ด้วย OpenSSL โดยไม่ใช้ Config File ได้
เริ่มด้วย Generate RSA Private Key:
openssl genrsa -out example.key 2048
ต่อไป Generate CSR:
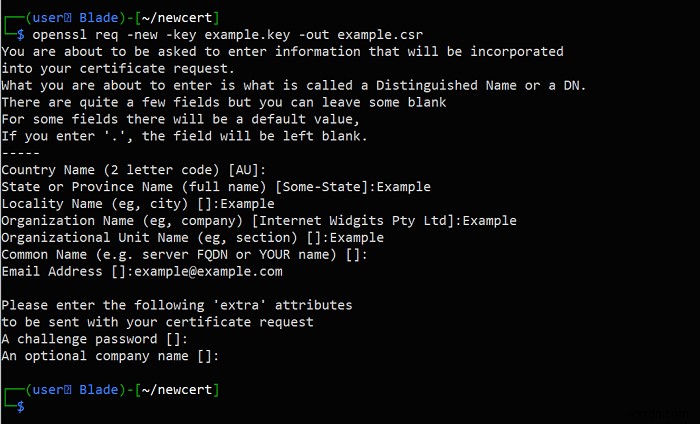
openssl req -new -key example.key -out example.csr
ตอน Generate CSR คุณจะ Prompt ถาม Organization Info
สุดท้าย Generate Certificate เอง:
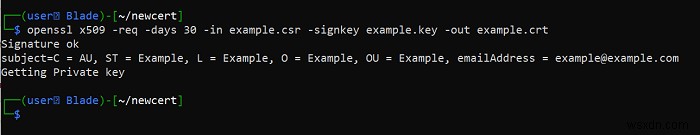
openssl x509 -req -days 30 -in example.csr -signkey example.key -out example.crt
Verification of Keys และ Certificates
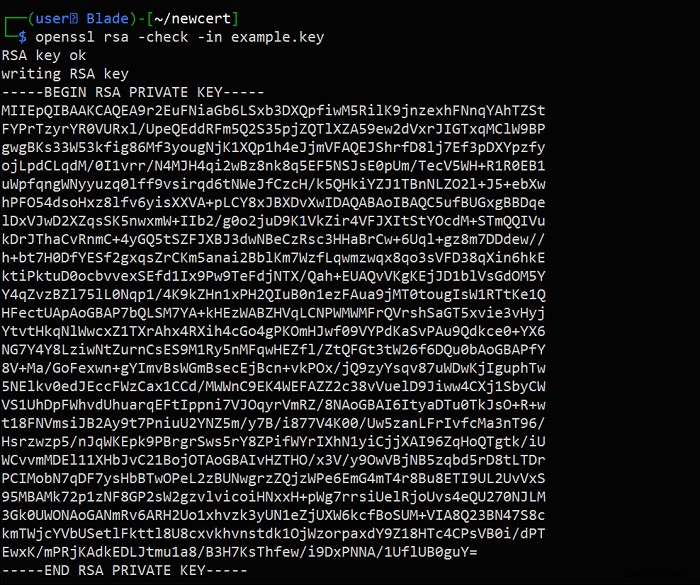
Keys และ Certificates เช็คและ Verify ได้ง่ายด้วย OpenSSL ด้วย Flag -check:
openssl rsa -check -in example.key
คุณ Check Certificate Signing Requests ได้:
openssl req -text -noout -in example.csr
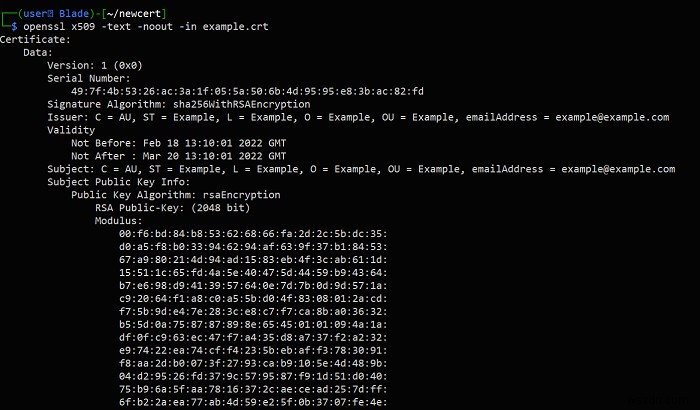
และ Certificates ด้วย:
openssl x509 -text -noout -in example.crt
Frequently Asked Questions
1. ยังต้องกังวล Heartbleed ไหม?
Heartbleed (CVE-2014-0160) เป็น Old Vulnerability ใน OpenSSL พบ 2014 TLS-servers และ Clients ที่รัน OpenSSL ถูก Affected Patch Release ไว้ไม่กี่วันหลัง Discovery และ Vulnerability นี้ไม่ควรกังวลในปี 2022 ตราบใดที่คุณรัน Modern และ Up-to-date OpenSSL Version
ถ้าใช้ OpenSSL บน Debian และ Ubuntu-based Systems คุณ Update ได้ตลอดด้วย Commands:
sudo apt update && sudo apt upgrade openssl
2. SSL Certificates ใช้ได้นานแค่ไหนก่อน Expire?
ขึ้นกับ Value ที่เลือกตอน Generate Certificate ระบุได้ด้วย Flag -days ตอน Generate Certificate
