

SSH เป็นโปรโตคอลยอดนิยมและมีประสิทธิภาพ สำหรับล็อกอินและจัดการ remote hosts จากเครื่อง local คู่มือนี้เดินทางผ่านคำสั่งต่างๆ สำหรับตรวจสอบ active SSH connections บน remote host
หมายเหตุ: ขึ้นกับ system configuration บางคำสั่งอาจต้องการ root หรือ sudo privileges
1. ใช้คำสั่ง WHO
คำสั่งแรกสำหรับแสดง active SSH connections คือ who
who ใช้แสดงว่าใครกำลังล็อกอินอยู่ในระบบ ให้ดู connected users และ source IP addresses
ใช้ who โดยไม่มี parameters:
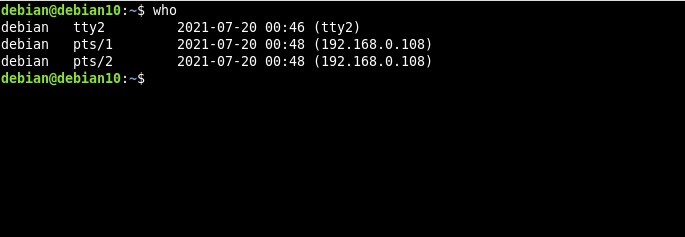
จาก output ข้างต้น เห็น debian user 1 คน เชื่อมต่อผ่าน tty และ SSH sessions 2 จาก remote IP address
เพิ่ม parameters ให้ who เพื่อรายละเอียดมากขึ้น เช่น แสดง last boot ของ connected users ด้วย -b -u:
who -b -u
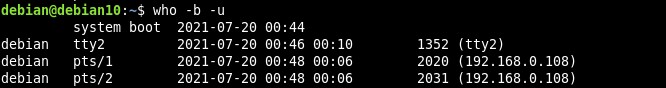
who มี options อื่นๆ ให้ผลลัพธ์ที่ปรับแต่งได้ อ่าน manual page เพื่อรายละเอียด
2. ใช้คำสั่ง W
คำสั่งถัดไปคือ w แสดง status ของ SSH sessions และ users ที่เชื่อมต่อ ต่างจาก who ที่ w ให้ข้อมูล running processes สำหรับแต่ละ user
เพิ่มเติม w ให้ข้อมูล idle SSH connections ซึ่งช่วยมากตอนต้อง terminate พวกมัน
รันคำสั่งโดยไม่มี options จะได้ output ประมาณนี้:
จากตัวอย่าง w ให้ detailed information เช่น username, TTY method, source IP, login time, idle time และอื่นๆ
เหมือน who ใช้ w กับ parameters ต่างๆ ได้ ตารางด้านล่างแสดง parameters ต่างๆ ของ w:
| Parameter | What it does |
|---|---|
| -h, --no-header | บอก terminal อย่าพิมพ์ header |
| -u, --no-current | บอก terminal ไม่สน username ขณะแสดง processes และ CPU time ของ connected users |
| -s, --short | บอก terminal พิมพ์ output แบบสั้น – exclude login time, JCPU และ PCPU |
| -f, --from | Enable/disable FROM option ของ print output |
| --help | แสดง w command options/parameters และ exit |
| -v, --version | แสดง version info และ exit |
| user | จำกัดผลลัพธ์เฉพาะ user ที่ระบุ |
ตัวอย่างด้านล่าง ใช้ w กับ -s และ -f แสดง abridged output ของ SSH sessions พร้อม truncate FROM part
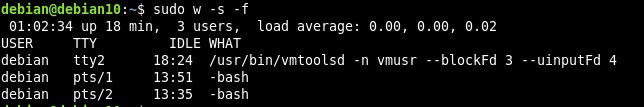
แม้จะใช้บ่อยน้อย แต่ w กับ environmental และ file parameters ก็ได้ ดู man pages เพื่อรายละเอียด
3. ใช้คำสั่ง Last
ใช้ last แสดง SSH sessions ที่เชื่อมต่อทั้งหมด last แสดง list ของ last logged-in users
ทำงานโดยตรวจสอบ designated file เช่น /var/log/wtmp แสดง users ที่ล็อกอิน/ออก ตั้งแต่สร้างไฟล์ คำสั่งยังให้ข้อมูลเกี่ยวกับ SSH sessions ที่สร้างระหว่าง client และ server
Syntax ทั่วไป:
last
ตัวอย่าง:
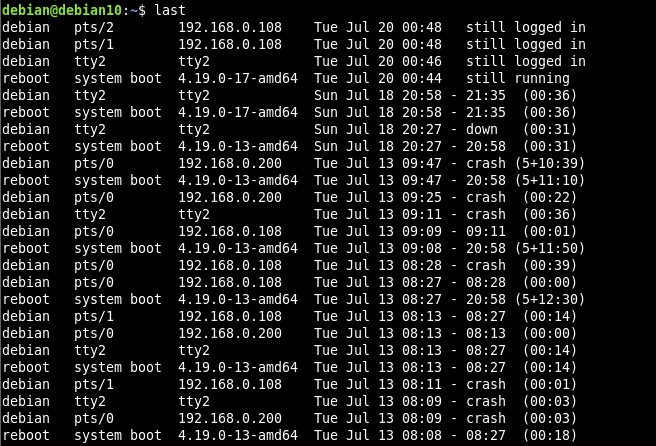
เนื่องจาก output จาก last ใหญ่มาก ใช้ grep แสดง active sessions เฉพาะ
ตัวอย่าง:
last | grep still

ปรับ output จาก last ให้ detailed ได้ เช่น แสดง full usernames และ domains ด้วย -w:
last -w
last รองรับ options มาก นี่คือ commonly used options:
| Parameter | What it does |
|---|---|
| -a, --hostlast | แสดง hostname ในคอลัมน์สุดท้าย |
| -d, --dns | Linux เก็บ hostname และ IP ของ remote hosts parameter นี้แปลง IP เป็น hostname |
| -file, --file | บอก last ใช้ designated file อื่นแทน /var/log/wtmp |
| -F, --fulltimes | บอก last พิมพ์ login/logout dates และ times ทั้งหมด |
| -i, --ip | คล้าย --dns แต่แสดง IP number แทน hostname |
4. ใช้คำสั่ง Netstat
ไม่สามารถลืม netstat ได้ netstat แสดง network connections, network interfaces, routing tables และอื่นๆ
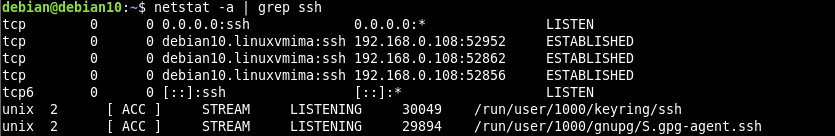
ใช้ netstat กรอง established หรือ connected SSH sessions บน Linux server:
netstat | grep ssh
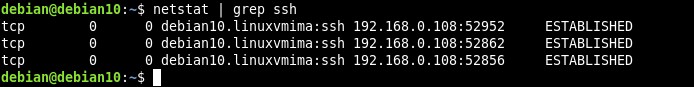
คำสั่งแสดงเฉพาะ established SSH connections
แสดง all connections รวม listening และ non-listening ด้วย flag -a:
nestat -a | grep ssh
5. ใช้คำสั่ง SS
หากต้องการข้อมูลเพิ่มเติมเกี่ยวกับ connected SSH sessions ใช้ ss ซึ่งแสดง socket data คล้าย netstat
ตัวอย่าง grep output จาก ss ด้วย -a (all) แสดง SSH sessions ที่เชื่อมต่อทั้งหมด:
ss -a | grep ssh
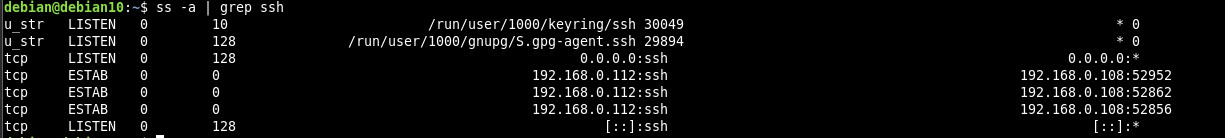
Output แสดง SSH connections ทั้งหมดบน remote host รวมถึง SSHD daemon
กรองเฉพาะ established SSH connections pipe output กลับไป grep:
ss -a | grep ssh | grep ESTAB
คำสั่งข้างต้นจะคืนแค่ active SSH connections
ss มี options อีกเยอะ เรียนรู้เรื่อง active server connections ต่างๆ เช่น ใช้ -e flag แสดง socket information เพิ่มเติม
สรุป
ควร monitor remote hosts สำหรับ unauthorized SSH logins และดำเนินการ เช่น secure server หรือ disable password authentication อีกทางหนึ่ง ใช้ reverse SSH tunneling อนุญาต external connection ไปยัง PC ของคุณ
