

Windows 10/Server 2016+ ไม่เขียน WindowsUpdate.log แบบ Text จริงแล้ว ใช้ ETW (Event Tracing for Windows) เพื่อ Performance และ Disk Space
File %windir%\WindowsUpdate.log ยังมีแต่เขียนว่า "ใช้ ETW แล้ว ใช้คำสั่ง Get-WindowsUpdateLog"
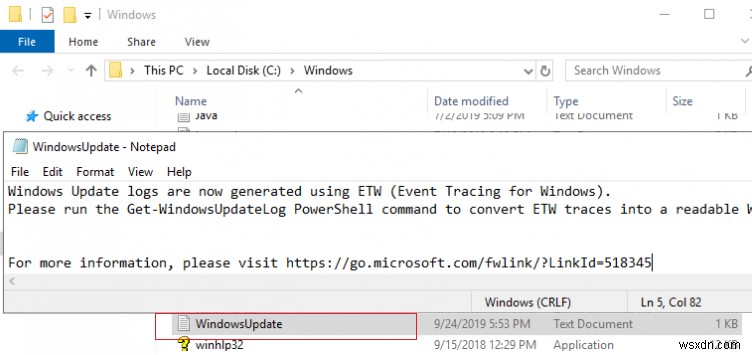
แปลง ETW เป็น Text Log ด้วย PowerShell
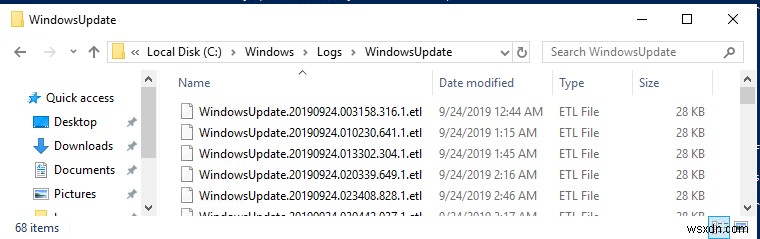
คำสั่ง: Get-WindowsUpdateLog รวบรวม .etl จาก C:\Windows\Logs\WindowsUpdate สร้าง Text Log
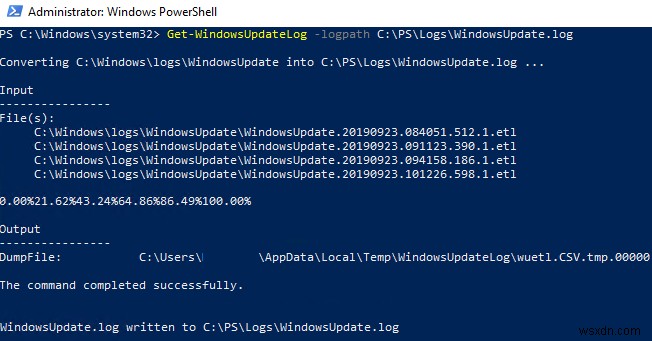
บันทึกที่ C:\PS\Logs: Get-WindowsUpdateLog -logpath C:\PS\Logs\WindowsUpdate.log
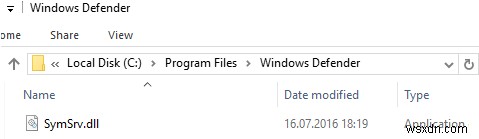
ปัญหา SymSrv.dll Missing (Server 2016)
Copy-Item : Cannot find path 'C:\Program Files\Windows Defender\SymSrv.dll'...
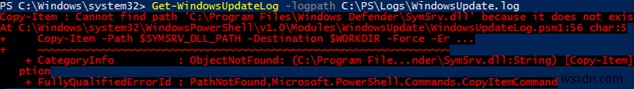
Windows Defender ไม่ได้ติดตั้ง → ไม่มี SymSrv.dll แก้: Install Defender, หรือ Copy จากเครื่องอื่น, หรือหาใน WinSxS → Copy ไป C:\Program Files\Windows Defender
การทำงานของ Get-WindowsUpdateLog
- อ่าน .etl ทั้งหมด
- แปลงเป็น CSV/XML
- สร้าง Text Log ตาม -LogPath (Default: Desktop)
วิธีอ่าน: Invoke-Item -Path C:\PS\Logs\WindowsUpdate.log
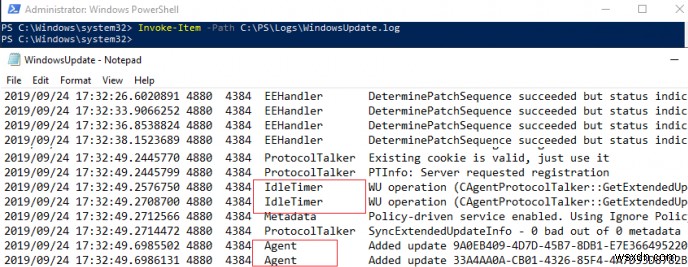
เจอ Unknown(140): GUID... (No Format Information found) = ไม่มี Symbol Server (ดาวน์โหลดจาก Azure อัตโนมัติ) Offline Symbols ใช้ได้
หมายเหตุ: Log ไม่ Real-time ต้องรันคำสั่งใหม่ทุกครั้ง หรือทำ Scheduled Task
Parse Log ด้วย PowerShell
Log รวมหลาย Event Source: AGENT, AU, AUCLNT, HANDLER, MISC, PT, REPORT, SERVICE, SETUP, DownloadManager ฯลฯ
Filter 30 Event ล่าสุดของ Agent:
Select-String -Pattern '\sagent\s' -Path C:\PS\Logs\WindowsUpdate.log | Select-Object -Last 30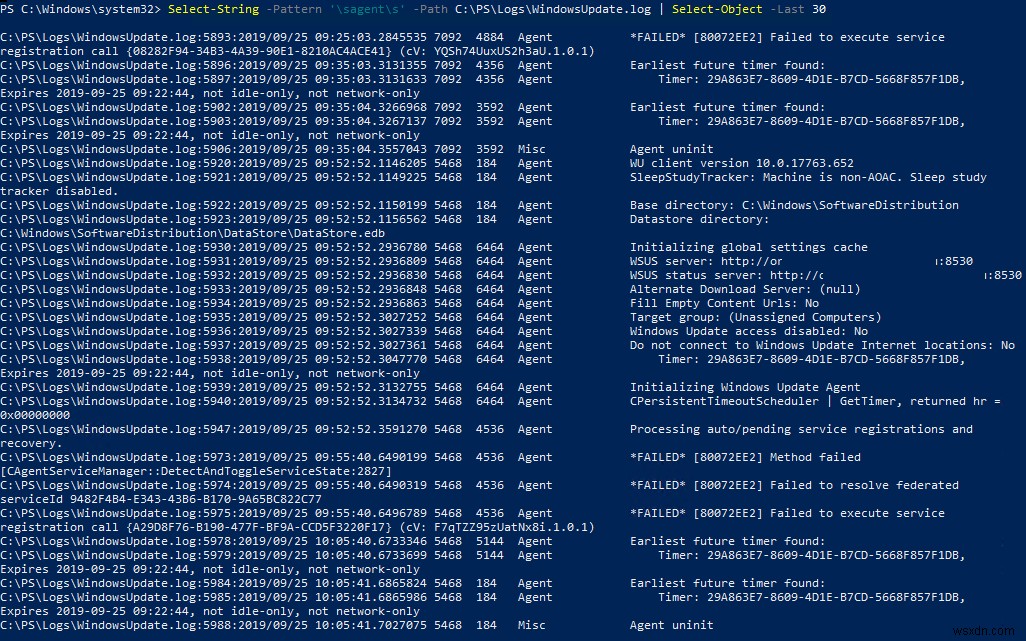
Filter หลาย Source (Agent + Misc) 50 Event:
Select-String -Pattern '\sagent\s|\smisc\s' -Path c:\PS\Logs\WindowsUpdate.log | Select-Object -Last 50ค้นหา KB Number, Errors (FAILED, Exit Code, FATAL) ได้
Remote Computer: Get-WindowsUpdateLog -ETLPath \\server\C$\windows\Logs\WindowsUpdate -LogPath C:\PS\Logs\windowsupdate-remote.log
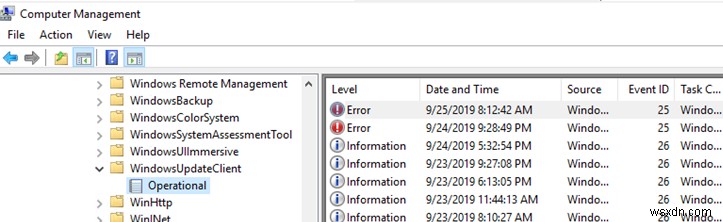
ใช้ Event Viewer แทน
Applications and Services Logs → Microsoft → Windows → WindowsUpdateClient → Operational
Module PSWindowsUpdate จัดการ Update ผ่าน PowerShell CLI ได้
 No