

ผู้ดูแลระบบหลายคนมักใช้เครื่องมือคอนโซล netstat หรือกราฟิก TCPView เพื่อแสดงข้อมูลเกี่ยวกับการเชื่อมต่อ TCP/IP ที่ใช้งานอยู่และพอร์ต TCP ที่เปิดอยู่ใน Windows แทน netstat คุณสามารถใช้ cmdlet Get-NetTCPConnection ใน PowerShell เพื่อรับข้อมูลเกี่ยวกับการเชื่อมต่อเครือข่ายที่ใช้งานอยู่ใน Windows พอร์ต TCP ที่เปิด และกระบวนการที่กำลังทำงานซึ่งใช้โปรโตคอล TCP/IP PowerShell ทำให้ง่ายต่อการเขียนสคริปต์ที่ซับซ้อนเพื่อรับข้อมูลและติดตามพอร์ต TCP ที่เปิด กระบวนการ และการเชื่อมต่อเครือข่ายที่สร้างขึ้น
ลองรันคำสั่ง Get-NetTCPConnection โดยไม่มีตัวเลือกใดๆ
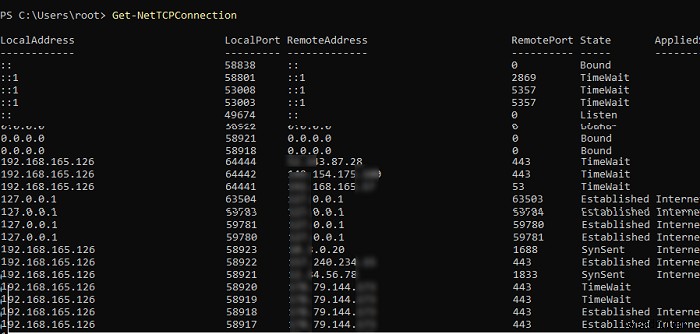
เหมือน netstat คำสั่งได้แสดงรายการการเชื่อมต่อทั้งหมดที่ใช้งานอยู่พร้อมที่อยู่ IP ท้องถิ่นและระยะไกล พอร์ต สถานะการเชื่อมต่อ (Listen, Established Internet, TimeWait, Bound, CloseWait, SynReceived, SynSent) และ Process ID (PID) ที่ใช้การเชื่อมต่อ TCP นี้
คุณสามารถแสดงรายการพอร์ตที่เปิด (Listening) บนคอมพิวเตอร์ท้องถิ่นของคุณ:
Get-NetTCPConnection -State Listen | Select-Object -Property LocalAddress, LocalPort, RemoteAddress, RemotePort, State | Sort-Object LocalPort |ft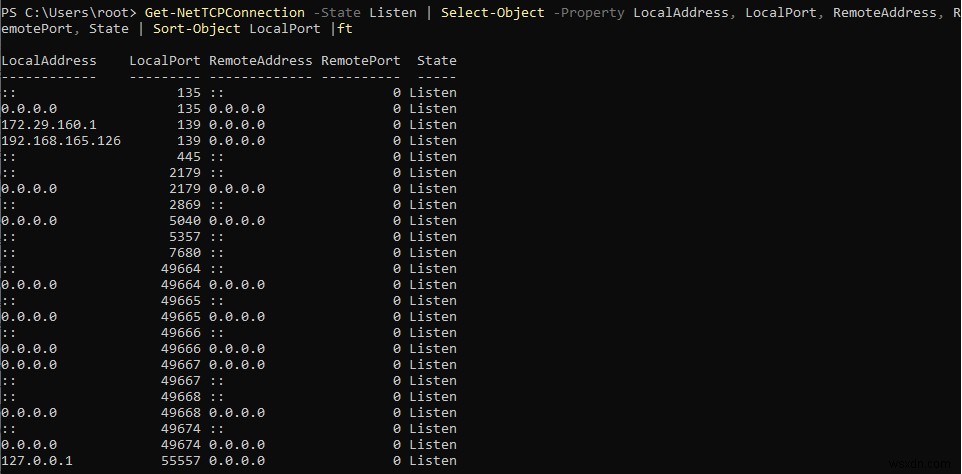
Cmdlet Get-NetUDPEndpoint ใช้สำหรับรับข้อมูลเกี่ยวกับพอร์ต UDP
คุณสามารถแสดงการเชื่อมต่อภายนอก (Internet) เท่านั้น:
Get-NetTCPConnection -AppliedSetting Internetคุณสามารถแสดงชื่อ DNS ของโฮสต์ระยะไกลและชื่อกระบวนการสำหรับการเชื่อมต่อ TCP:
Get-NetTCPConnection -State Established |Select-Object -Property LocalAddress, LocalPort,@{name='RemoteHostName';expression={(Resolve-DnsName $_.RemoteAddress).NameHost}},RemoteAddress, RemotePort, State,@{name='ProcessName';expression={(Get-Process -Id $_.OwningProcess). Path}},OffloadState,CreationTime |ftสคริปต์ PowerShell นี้ Resolve ที่อยู่ IP ของโฮสต์ทั้งหมดเป็นชื่อ DNS และระบุชื่อกระบวนการสำหรับการเชื่อมต่อทั้งหมด
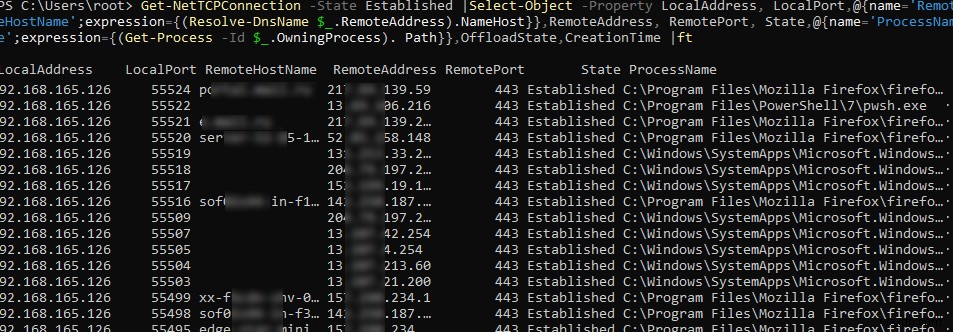
จากชื่อกระบวนการพาเรนท์ PID คุณสามารถแสดงรายการบริการ Windows ที่เกี่ยวข้องซึ่งใช้เครือข่าย:
Get-WmiObject Win32_Service | Where-Object -Property ProcessId -In (Get-NetTCPConnection).OwningProcess | Where-Object -Property State -eq Running | Format-Table ProcessId, Name, Caption, StartMode, State, Status, PathNameคุณสามารถดูเฉพาะการเชื่อมต่อเครือข่ายที่เริ่มต้นโดยกระบวนการเฉพาะได้ โดยใช้สคริปต์ PowerShell ต่อไปนี้:
$TrackProcessName = "*chrome*"
$EstablishedConnections = Get-NetTCPConnection -State Established |Select-Object -Property LocalAddress, LocalPort,@{name='RemoteHostName';expression={(Resolve-DnsName $_.RemoteAddress).NameHost}},RemoteAddress, RemotePort, State,@{name='ProcessName';expression={(Get-Process -Id $_.OwningProcess). Path}}, OffloadState,CreationTime
Foreach ($Connection in $EstablishedConnections)
{
If ($Connection.ProcessName -like $TrackProcessName)
{
$Connection|ft
}
}
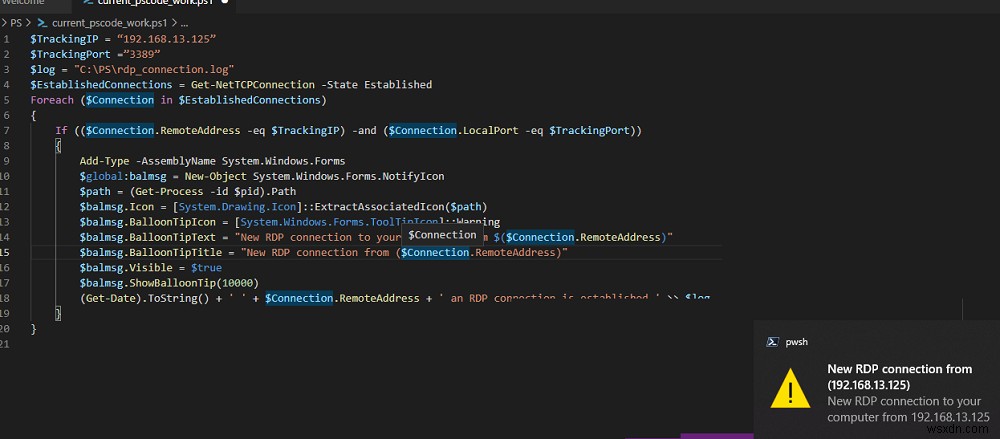
คุณสามารถใช้ Get-NetTCPConnection cmdlet ในสถานการณ์ต่างๆ เช่น คุณสามารถสร้างสคริปต์ PowerShell เรียบง่ายเพื่อติดตามว่าการเชื่อมต่อถูกสร้างจากที่อยู่ IP เฉพาะไปยังพอร์ตท้องถิ่นที่ระบุ และแสดงการแจ้งเตือนป๊อปอัปให้ผู้ดูแลระบบ
ในตัวอย่างต่อไปนี้ สคริปต์ PowerShell ตรวจสอบว่าการเชื่อมต่อจากที่อยู่ IP ที่ระบุปรากฏบนพอร์ต RDP เริ่มต้น 3389 หรือไม่ หากการเชื่อมต่อปรากฏ สคริปต์จะแสดงการแจ้งเตือนป๊อปอัป และบันทึกวันที่และเวลาของการเชื่อมต่อลงในไฟล์ข้อความ:
$SourceIP = "192.168.13.125"
$TargetPort ="3389"
$log = "C:\PS\rdp_connection_log.txt"
$EstablishedConnections = Get-NetTCPConnection -State Established
Foreach ($Connection in $EstablishedConnections)
{
If (($Connection.RemoteAddress -eq $SourceIP) -and ($Connection.LocalPort -eq $TargetPort))
{
Add-Type -AssemblyName System.Windows.Forms
$global:balmsg = New-Object System.Windows.Forms.NotifyIcon
$path = (Get-Process -id $pid).Path
$balmsg.Icon = [System.Drawing.Icon]::ExtractAssociatedIcon($path)
$balmsg.BalloonTipIcon = [System.Windows.Forms.ToolTipIcon]::Warning
$balmsg.BalloonTipText = "New RDP connection to your computer from $($Connection.RemoteAddress)"
$balmsg.BalloonTipTitle = "New RDP connection from ($Connection.RemoteAddress)"
$balmsg.Visible = $true
$balmsg.ShowBalloonTip(10000)
(Get-Date).ToString() + ' ' + $Connection.RemoteAddress + ' an RDP connection is established ' >> $log
}
}
ด้วยวิธีเดียวกัน คุณสามารถติดตามและบันทึกการเชื่อมต่อเครือข่ายผ่านโปรโตคอลอื่นๆ เช่น SSH, SMB, FTP, SMTP ฯลฯ สคริปต์ PowerShell นี้อาจถูกแปลงเป็นบริการ Windows ที่จะเริ่มต้นโดยอัตโนมัติ
คุณสามารถใช้สคริปต์นี้ร่วมกับที่เราอภิปรายก่อนหน้านี้: RDP Brute Force Attack Protection with Powershell
คุณสามารถรับรายการพอร์ต TCP ที่เปิดและการเชื่อมต่อบนคอมพิวเตอร์ระยะไกลโดยใช้ PowerShell remoting cmdlets (Enter-PSSession และ Invoke-Command)
Invoke-Command -ComputerName be-dc01 {Get-NetTCPConnection -State Established}Get-NetTCPConnection cmdlet (เช่นเดียวกับ Test-NetConnection) อาจเป็นประโยชน์มากในการติดตามและวินิจฉัยการเชื่อมต่อเครือข่ายใน Windows
