

Bluetooth security เป็นหัวข้อความปลอดภัยที่ under-rated มากที่สุดในวันนี้ แทนที่เราจะมี blue-capable device อย่างน้อยหนึ่งเครื่อง เรากادไม่เคยสนใจว่ามันทำอะไรและ configure อย่างไร บน mobile devices Bluetooth เปิด by default และเราไม่เคยเปลี่ยน default PIN code จาก four-digit combination ปกติ เช่น 0000, 1234 หรือคล้ายๆ กัน
มัน remind คุณของคนที่ทิ้ง wireless routers ไว้กับ default password และไม่มี encryption อุปกรณ์เหล่านี้ถูก abuse บ่อย บางครั้งโดย accident เพราะคอมพิวเตอร์ auto-connect ไป network สะดวกที่สุด ซึ่งมัก unsecured, unencrypted, free-for-all access points
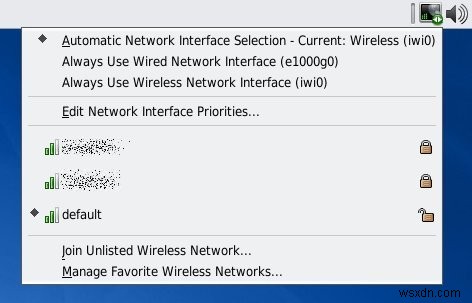
ใน這方面 Bluetooth เหมือน router security แต่มากกว่านั้น เพราะ routers อยู่บ้าน แต่ phones, palm devices และ laptops ไปทุกที่ exposed to threats มากกว่า
ในบทความนี้ จะพยายาม address basic aspects ของ Bluetooth security และวิธี assess และ negate potential risks ด้วย simple practices พยายามไม่ technical เกินไป
มา看看ว่าคุณสามารถทำอะไรได้บ้าง เพื่อให้ Bluetooth devices ของคุณไม่ expose digital throats ให้กับ wicked fangs of the web
Pairing of devices
นี่คือส่วนสำคัญที่สุด - และ vulnerable ที่สุด - ของ Bluetooth communications: initial exchange of keys ระหว่างสอง devices ที่อยากคุยกัน
ทำ analogy ให้ดี: คิดถึง wireless security ของ router คุณอยาก encrypt wireless traffic ให้ никто לאสามารถ decipher contents ของ data ไหลระหว่าง router และ devices ต่างๆ ที่เชื่อมต่อกับ internal network ของ router รวมถึง desktops, laptops, mobile devices ฯลฯ
เพื่อทำให้ router wireless communications secure คุณสร้าง password และ password นี้ inserted เข้า router Web interface ใน plain text! คิดดู คุณ connect ไป router ผ่าน browser มักใช้ address 192.168.x.x หรือ 10.x.x.x ให้ credentials มักทำผ่าน wired connection แบบ unencrypted
ทฤษฎีแล้ว ถ้ามี malicious hosts บน internal network อาจ sniff administrative password ที่คุณใช้ connect router รวมถึงข้อมูลอื่นๆ ที่แลกเปลี่ยนกับ router: IP ranges, MAC filtering, port forwarding และ passphrase ที่ encrypt wireless communications
แต่วันนี้ส่วนใหญ่ไม่มี rogues ฟังบน home network ดังนั้น initial configuration stage ทำได้ปลอดภัย หลังจากนั้น radio transmissions ที่ emitted โดย wireless devices แม้ detect และ capture ได้ง่ายโดย rogues แต่มัน encrypted และ unreadable รักษาความ confidential ของ communications
กลับไป Bluetooth initial key exchange คือ weakest link ของ Bluetooth security ทั้งหมด และทำให้แย่กว่า: ในขณะที่คุณใช้ wired connections secure routers Bluetooth devices ต้อง transmit wireless signals ซึ่ง receivable โดย Bluetooth-capable device ใดๆ ใน range
ดังนั้น Bluetooth security ของคุณเริ่มจากการ ensure ว่า key exchange ปลอดภัย
Safe key exchange
วิธีที่ดีที่สุด pair devices คือทำใน isolated rooms ห่างจาก prying eyes และ ears Bluetooth devices ส่วนใหญ่มี range สั้นมาก ถ้าไม่มี antennas ภายในไม่กี่เมตร คุณควรปลอดภัย
Pairing devices ใน crowded public places เช่น airports ไม่ recommended
Know which device to pair with
เหมือน routers Bluetooth devices ส่วนใหญ่ใช้ generic identifiers มัก based on vendor name และ model type ทำให้ identification ยากเมื่อมี multiple choices ควรให้ meaningful but not too descriptive names กับ Bluetooth devices ของคุณ เพื่อรู้ว่าอันไหนเป็นของคุณ
เช่น Dedo ดีกว่า RG4453C ไม่ว่าจะเป็น brand และ firmware revision อะไร คุณไม่ได้เรียกคนด้วย ID numbers หรือ Social Security Numbers เพราะ generic เกินจดจำ คุณใช้ names
Key length is important
อีกปัจจัยสำคัญใน security scheme ทั้งหมด แม้ Bluetooth traffic จะ encrypted ไม่ว่าคุณจะเลือก key อะไร ความยากในการ crack encrypted messages ขึ้นอยู่กับ key length
ทฤษฎีทุก encrypted messages crack ได้ ต้องใช้เวลาทั้ง universe และมากกว่านั้น run ทุก possible combination ของ keyboard symbols ต่อทุก possible combination ของ text บน huge grid of computers
ในความเป็นจริง สิ่งที่ทำให้ encrypted messages secure คือเวลาที่ต้องใช้ crack algorithm หรือ key ถ้าเวลานี้เกิน reasonable period brute force attempts จะ useless
นี่คือสิ่งที่คุณอยากป้องกัน communications - automated guesswork ต่อ network คุณไม่ต้องมี perfect solution แค่ adequate enough to defeat most common attack methods ใน common situations over reasonable exposure time นั่นคือ several hours หรือ days นั่นแหละ
การเลือก strong PIN code จะ ensure device communications ของคุณ safe SANS Institute แนะนำ 12-digit PIN code
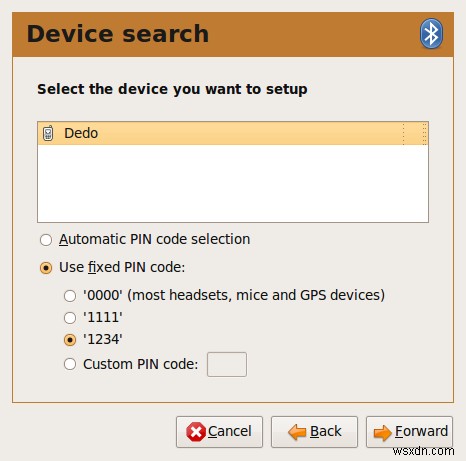
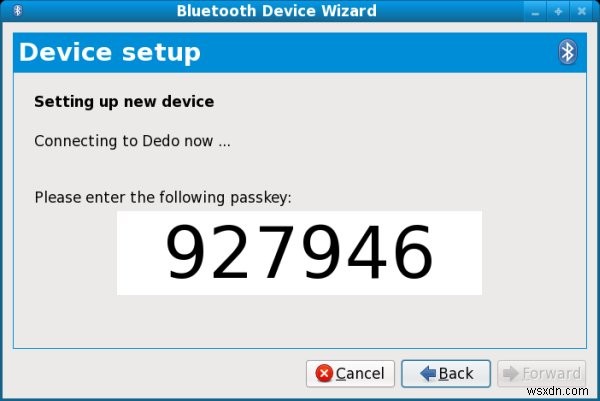
มาดู screenshot ข้างบนอีกครั้ง:
Screenshot ถ่ายบน Ubuntu Jaunty Jackalope ระหว่าง pairing attempt กับ Nokia cell phone ผมตั้งชื่อ Dedo ตามก่อนหน้า อีกอย่างต้องเลือกคือ PIN code
เห็นได้ว่า Bluetooth wizard บน Ubuntu เสนอ most common, known PINs ที่ vendors ใช้ มักโคจร easily guessable set - 0000, 1111, 1234 ฯลฯ ไม่ต่างจาก routers ที่ ship with admin/12345 username/password combo
Combinations นี้เป็น first choice ของ Blue attacker any time easy picking of low-hanging fruit แม้คุณใช้ non-default four-digit code คุณเพิ่ม security ทันที แม้ choice pool เล็กและ work through ได้ง่ายโดย attackers
ตัวอย่างน่าสนใจอีกอย่างคือ approach ของ Fedora ใน Leonidas release เมื่อ pairing กับ external device Fedora สร้าง random PIN ที่คุณต้อง input ลงอีก device เพื่อให้ pairing สำเร็จ Approach นี้ automatically เพิ่ม security ทั้งเพราะ key random และยาวกว่า standard four-digit combinations
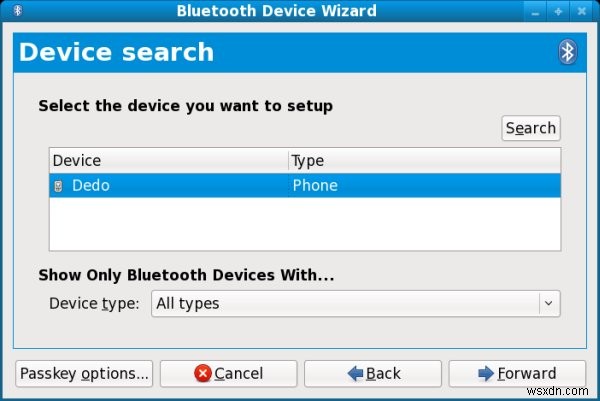
12-digit PIN แนะนำ อาจบ่นิดหน่อย remember หรือ input ลง desired devices แต่ทำเพียงครั้งเดียวต่อ pairing attempt
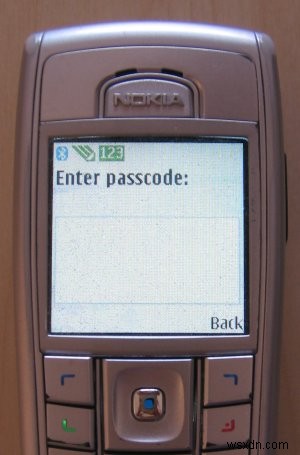
เมื่อ pair successfully และ safely คุณพร้อมแล้ว ต่อไปจะดูว่าควรทำอะไรหลัง configure gadgets แล้ว
Safe practices
จะ review few simple common-sense rules ที่ช่วย maintain security ของ Bluetooth devices Principle เหมือน any type of data exchange และ sharing คุณอยากให้ other party เข้าถึงไฟล์คุณไหม? มากแค่ไหน? Read only หรือ write ด้วย? ไฟล์ไหนอยาก share? คำถามเหล่านี้ valid สำหรับ any data exchange over wired หรือ wireless network ไม่ว่าจะเป็น P2P sharing, Samba, NFS, Bluetooth, FTP หรือ protocol อื่นๆ
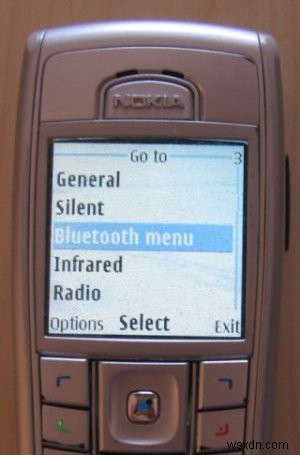
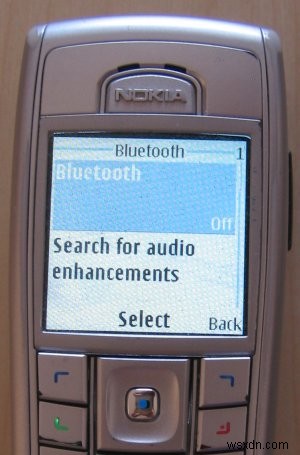
ปิด Bluetooth devices เมื่อไม่ใช้
ประการแรก ประหยัด battery life ประการสอง ไม่มีเหตุผล advertise presence ของคุณให้ wide world ใช้งาน Bluetooth device เมื่อต้องการ transmit data แล้วปิด มากกว่าคนใช้ Bluetooth น้อยมาก ถ้าเลย เปิดไว้ simply unnecessary
Deny unsolicited connections
นี่คือ basic security principle ทั้งหมด - default deny หมายถึง ไม่ให้อะไรผ่าน ยกเว้น small whitelist ของ trusted connections ใช้กับ Bluetooth ได้ดีเท่ากัน
ทุกครั้งที่ new, unknown device ขอ connect ไปยังของคุณ ควร examine situation อย่างรอบคอบ คุณรู้จัก other host นี้ไหม? Connection expected ไหม? ถ้าตอบ 'yes' ไม่ได้ - ควร deny attempts เรียบร้อยอย่างนั้น
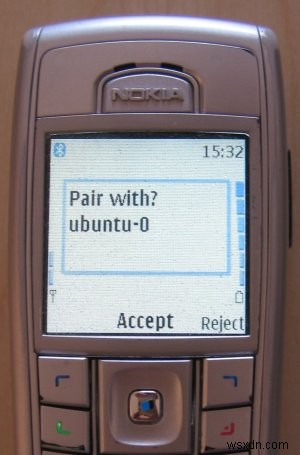
อาจสังเกตว่า cellphone หลายตัวเสนอ Accept เป็น default choice ตัวอักษรใหญ่ bold ใน general หมายถึง phone geared toward usability แต่สำหรับคนส่วนใหญ่หมายถึง less security
เช่นกัน เมื่อ device พยายามส่งข้อมูลมาให้ แม้คุณ paired แล้ว ต้อง ensure ว่าคุณ actually accept data transfer หรือ attempt to browse files Bluetooth connections มัก deliberate ดังนั้น unexpected surprise น่าจะ not desired
ตัวอย่าง เมื่อผมคลิก Send files to device ...
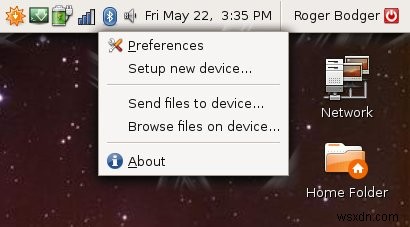
โทรศัพท์ของผมจะ prompt เนื่องจาก expected contact ผม allow แต่ถ้าคุณได้ nudges เหล่านี้ out of the blue น่าจะ undesired
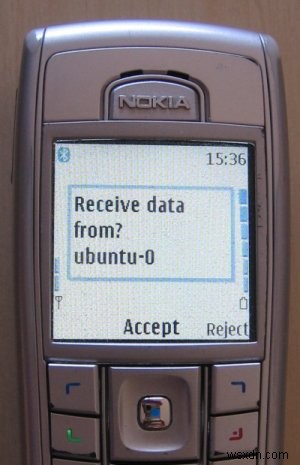
แล้วเราก็เห็น fancy screenshot ที่ผมถ่ายตอนเขียน VMware secrets article บน tiny display ของ cellphone


Same applies เมื่อ browse device ถ้าคุณ allow connection ไฟล์คุณจะ visible to other party สิ่งนี้ควร consider อย่างรอบคอบ เช่น คุณอาจให้ colleague ส่งรูปที่ถ่ายด้วย 0.1Kp camera แต่อาจไม่อยาก expose phone contents

Bluetooth devices ของคุณจะ behave อย่างไร ขึ้นกับ exact model และ type ที่ใช้ ผมไม่สามารถให้ exact recipe แต่แน่นอน recommend general settings
ไม่ว่า device อะไร พยายาม keep off เมื่อไม่ใช้ ensure activate security features ถ้ามี รวมถึง way to monitor (และ reject) incoming Bluetooth connections Device ควร prompt คุณสำหรับ any individual data transfer attempt แม้คุณเพิ่ง allow ไปแล้ว ทำไม? ถ้า device ที่คุณเพิ่ง pair ถูกขโมย? ถ้าคน pinched friend's phone พยายาม harass ทุกคน? crude example แตเป็น definite possibility เพราะ lightweight small mobile devices easily misplaced, forgotten, lost, stolen
อาจดูเหมือน nuisance ต้อง authorize every connection แต่ความจริง ไม่มีมากนัก ไปไหน แค่ไหน คุณ Blue กับเพื่อนบ่อยแค่ไหน?
เพราะ exact reason นี้ scarcity of Bluetooth connections คนส่วนใหญ่ลืม security precautions involved with protocol this potentially exposing data ให้ unwanted third parties ใน most cases phone จะมี junk และ contacts สำคัญบ้าง แต่อาจมี sensitive data ด้วย
เช่นกัน คุณสามารถ configure computers สำหรับ Bluetooth sharing เช่น Fedora 11 Leonidas มี dedicated menu File Sharing Preferences ที่ cover Blue devices

ดู menu เห็น options เยอะ เช่น share files only with bonded devices หรือ disallow remote devices delete files forcing read-only mode เหมือนกัน อาจ accept files only for bonded devices และ receive notifications
Next steps
Next step ใน tutorial นี้คือ overview different Bluetooth tools available บางอย่างสำหรับ Linux บางอย่าง Windows สำหรับ scan active Bluetooth devices, sniff connections ฯลฯ แต่ยังไม่ทำตอนนี้
จะมี dedicated network analysis tutorial ในอนาคต การใช้ tools ประเภทนี้ต้องการ expertise และ responsibility การ abuse security skills แม้ innocent pranks ก็ easily done
Stay tuned for sequels ที่เราจะ ethically เรียนรู้ security scanning เพื่อ assess risks, audit own networks สำหรับ vulnerabilities และ develop right countermeasures ต่อ possible threats
สรุป
แค่นี้แหละ Just a few simple rules และ Bluexperience ของคุณจะเป็น joyful matter สำหรับคนส่วนใหญ่ Bluetooth คือ something akin to first image ใน tutorial นี้ สוגของ oral ornament ที่ rappers ใส่หรือแบบนั้น Bluetooth แม้ popular และ practical แต่ very obscure ตอน usage models และ security practices คนส่วนใหญ่ completely unaware ว่าอุปกรณ์ทำงานยังไง และ expose อะไรให้ wide world
โชคดี configuring Bluetooth devices ไม่ different จาก radio-happy device ใดๆ basic principles เหมือนกัน ใช้ encryption ทำให้ transmitted data unreadable โดยใครยกเว้น intended parties Ensure initial exchange of encryption keys ทำ privately ใช้ strong keys กลับคือ strong password ปิด devices เมื่อไม่ใช้ Individually accept/deny incoming pairing requests พร้อม clearly identifying other device ใช้ caution เมื่อ sharing files ทั้งสองทาง
หวังว่าทutorial นี้ useful สำหรับคุณ Have fun และ see you around
Cheers.
