

ตอนนี้คุณรู้ว่า Microsoft Enhanced Mitigation Experience Toolkit (EMET) เป็นซอฟต์แวร์ความปลอดภัยที่ดีที่สุดสำหรับ Windows เหตุผลหลายประการ: ติดตั้งและตั้งค่า Simple และ Transparent ไม่มีคำถาม愚蠢 ฟรี และ Effective ในสิ่งที่มันทำ ไม่หยุดคุณจากการเป็นโง่ แต่หยุด Software ไม่ให้ Misbehave นั่นทำให้มัน Awesome และเป็นเหตุผลที่มันได้ Spotlight น้อยในโลก Pay-for-security
เวอร์ชัน Public จริงแรกออกมา หมายเลข 4.0 เวอร์ชันก่อนหน้ายังใช้ได้ แต่เป็น Beta/Interim editions สำหรับ Geeks ตัวนี้ Normal people ใช้ได้ ลองให้ภาพรวมและ Tutorial รายละเอียดช่วยให้คุณใช้และ Implement EMET ใน Security setup ด้วยความสบายใจ
การติดตั้ง
Installation ค่อนข้าง Trivial แต่มีอย่างหนึ่งต้องคำนึง: EMET v4 ต้องการ Microsoft .NET Framework v4 詩的ですね ก่อนอื่นต้อง Install .NET Framework 4 ก่อนถึงจะใช้ EMET ล่าสุดได้
คลิกผ่าน Wizard เร็วที่สุด โดยไม่อ่านรายละเอียด Seriously มันง่าย ขั้นตอนที่ควรสนใจคือ Post-install wizard แรก
Configuration wizard ให้ตั้งค่า EMET ก่อน Launch ครั้งแรก ขั้นตอนแนะนำสำหรับ User ส่วนใหญ่ ตามที่ระบุชัดเจน: จะ Reset application settings จากการติดตั้งก่อนหน้า เพิ่ม Protections สำหรับโปรแกรมที่ใช้กันทั่วไปและถูก Target บ่อย รวมถึง Internet Explorer, Adobe Reader, Oracle Java เพิ่ม Trust rules สำหรับ Online services ยอดนิยม เพื่อไม่ให้ Trigger mitigations ใน Browser และ Enable detailed reporting ผ่าน System log facilities ข้อเสนอ: ควรทำ เพราะไม่ทำร้าย และคนส่วนใหญ่จะตั้งค่าเหล่านี้เองอยู่ดี รวมถึง Rerun wizard ได้ตลอด
ขั้นตอนแรกและ Basic configurations
Wizard เสร็จ EMET จะ Launch มาประเมิน UI และ Functions 左到右 上到下 หากเคยใช้ EMET ตั้งค่าจะคุ้นเคย แค่จัดเรียง Visual แตกต่าง
Import/Export & Configuration
Import/Export buttons บันทึกและดึง EMET configurations กลับมา เป็น XML files เก็บ Settings และ Application rules ควร Save configuration ก่อนทำ Drastic changes หรือ Re-run wizard เพราะอาจ Reset entire setup เราเคยพูดถึง Import/export rules ใน Review EMET 3.5 TP สำหรับทุกประการ นี่คือ Save/Open เทียบเท่า Software ปกติ
Apps button เปิดหน้าต่าง Configure programs Trust button เปิดหน้าต่าง Configure certificates สำหรับ Online services เร็วๆ นี้
Profiles & Reporting
Profiles คือ Collection of settings เก็บใน XML รวม Rules สำหรับ Machine แต่มันส่งผลต่อ Behavior ของ Entire system เมื่อ Applied สลับได้ระหว่าง Existing setup (Custom) และอีกสองตัว: Recommended และ Maximum
Recommended profile ตั้ง Mitigations แบบที่ Microsoft คิดว่า Least disruptive แต่ให้ Security ดี Maximum profile Toggle ทุก Option on หมายถึง Incompatible software อาจ Suffer หรือ Crash
แนะนำไม่ใช้ Maximum profile เพราะ Strict เกินไป โปรแกรมเยอะไม่ได้ Code และ Compile อย่าง Safe/Compliant อาจมี Weird behavior เมื่ออยู่ภายใต้ Mitigations
ตัวอย่าง: Google Chrome อาจ Aw, Snap! errors VLC Player ไม่ Auto-update ได้กับ Mitigations เป็บทุกตัว Skype (ก่อน Microsoft acquire) ไม่ทำงานดีกับบาง Options เราจะอธิบาย Settings ต่างๆ เร็วๆ นี้ สุดท้าย เปลี่ยน Application skin ได้ แต่ไร้ความหมาย
Reporting หมวดที่สี่จากซ้าย ครอบคลุม Messages เมื่อ EMET ทำงาน จะเห็น Desktop popups เมื่อ Mitigations Activated และ Entries ใน Event Log สกรีนช็อตจาก Review EMET ก่อนหน้านี้แสดง Functionality
System Status
System Status field แสดง 4 ประเภท Mitigations สำหรับ Software โดย Default จะเห็นภาพแบบ Permissive โปรแกรมที่ใช้ DEP และ ASLR ได้จะใช้ ไม่มี SEHOP protection เปิด Default และ Certificate Trust เปิดอยู่
คุณอาจถาม Acronyms ย่อมาจากอะไร? ผมจะไม่บอก เพราะมัน MEANINGLESS สำหรับคนที่ไม่ใช่ Programmer หรือเรียน Computer Science 大学 เราอาจพูดถึง Kernel, Scheduler, Memory management, Process space ฯลฯ
สำหรับ Normal people สิ่งที่ต้องรู้: Mitigations นี้จะส่งผลต่อ Software ของคุณ สิ่งเดียวที่ควรสนใจคือ Sane และ Correct functionality ของระบบ ระหว่าง Maximum settings และ Permissive settings (Defined by profiles) มี Options หลายอย่าง
ถ้า Mitigation ตั้งเป็น Disabled: ไม่ใช้ Opt In: Activate mitigations เฉพาะ System files, binaries, functions ขึ้นกับ Features ที่ OS, BIOS, Applications รองรับ Opt Out: รigoros มากกว่า พยายามใช้ Mitigations ทั้งหมดกับทุก Applications เว้นแต่คุณ Deselect สำหรับ Non-supported หรือ Misbehaving programs Always On: Activate mitigation โดยไม่มีความสามารถ Reset ตามหนังสือคือ Secure มากที่สุด และ Troublesome มากที่สุด เพราะอาจ Crash legitimate programs เยอะเกินไป
ข้อเสนอ: เริ่มด้วย Recommended profile หรือถ้าเก่งพอ Custom configuration Max settings ไว้จนกว่าจะเข้าใจใช้ EMET ได้ถูกต้องและมั่นใจ Certificate trust เรียบง่าย Enable หรือ Disable
Running Processes
Table นี้แสดง Process table และ Status ของแต่ละ Process ว่าถูก EMET Cover หรือยัง ณ จุดนี้ไม่สำคัญมาก แต่ภายหลังจะดูว่า Mitigations ของเรามาเล่นอย่างไร
Applications
จนถึงตอนนี้เรา Configure System แล้ว เลือก Profile ที่ต้องการ ซึ่ง Toggle on/off Specific mitigations และ Level สำหรับ Core system files และ Define Default behavior ตอนนี้ Configure Applications
นอกจาก General behavior ที่ Governed by DEP, ASLR, SEHOP และ Mitigations อื่นๆ สามารถ Fine-tune System protection ด้วย Application rules สำหรับ Programs ของคุณ เข้าถึงผ่าน Apps button ใน Toolbar
ภาพรวมสั้นๆ: Export/Export Selected บันทึก Rules สำหรับ Applications Add Application เปิด Wizard ค้นหา Program โดย Full path Add Wildcard ระบุ Generic phrase ทุก Programs ที่ Match จะถูก Cover ตัวอย่าง: IE มี 32-bit และ 64-bit ใช้ Full path ต้อง List 2 rules Wildcard ครอบคลุมทั้งคู่ Toggle Show Full Path เพื่อดู Rules
โปรดสังเกต Recommended settings จาก First-time wizard ใช้ Wildcards ทั้งหมด ทำให้ Deploy และ Govern ง่ายขึ้น เราจะพูดถึง Mass administration เร็วๆ นี้
Default Action กำหนด Application behavior - แค่ Log (Audit) หรือ Stop running process เมื่อพบ Exploit โปรดสังเกต ไม่ได้หมายถึง Malware แค่ Illegal instruction ที่ Mitigation ห้าม
ใต้ Mitigation Settings Check on/off Mitigation types รวมถึง Deep Hooks (Disabled by default ใน Recommended), Anti Detours, Banned Functions ถือว่าเป็น Holy grail ของ Sane coding practices
Mitigations field แสดง Applications ทั้งหมดที่ Covered รวมถึง Manual added, Imported, หรือ Cooked by wizard มี 3 ประเภท Mitigations: Memory, ROP, Other ไร้ความหมายพยายามอธิบายหากไม่รู้ Kernel works ตัวอย่าง: รู้ไหม Code, Data, Heap คืออะไร? Stack? System call? Instruction pointer บน x86 architecture? หากตอบ No ใดๆ ไม่ต้องรู้ Internals ของ Mitigations
แค่ถือว่าเป็น Settings หนึ่งที่ส่งผลต่อ Behavior ของ Programs หากทำงานดี ให้เป็น อย่า Disable ทีละตัว จนกว่าจะรู้ว่าปัญหาอยู่ที่ไหน ภายหลังจะพูดเพิ่ม
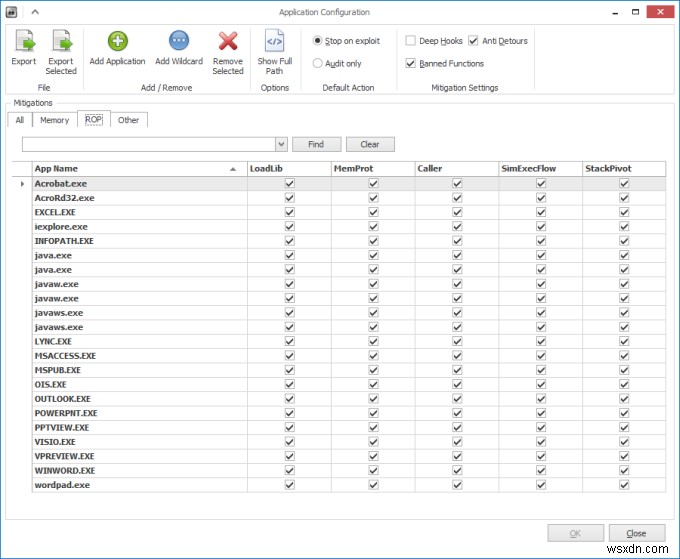
Application added
หลัง Add application ของคุณเอง (ซึ่งอาจไม่อยู่ใน List) อาจต้อง Restart โปรแกรมเพื่อ Load ด้วย EMET hooks มีตัวอย่างในบทความแรก และการใช้ Process Explorer Verify
Certificate Trust
Section นี้ Config websites ที่ควร Covered by Certificates เพื่อ Trust behavior ของพวกเขา เพื่อ Mitigations ไม่ Kick in และ Kill stuff ใน False positive action
Export rules ได้ Add/Remove websites ได้ หลัง Config จะ List ใน Protected Websites table พร้อม Pin Rule หมายถึง Sites จะ Trusted ก็ต่อเมื่อ Digitally signed by Certificate authority ที่แสดงใน Rule ใช้ Drop-down menu เปลี่ยน Rule ได้ แต่ข้อนิรूतไม่แนะนำ เทียบเท่า Tamper digital certificates ใน Browser ด้วยมือ
Pinning Rules Fine-tune effect ได้ เช่น Expiration date, Countries, Blocked hashes, Public key match ฯลฯ สาเหตุที่ดี ส่วนใหญ่ Settings ไม่มี Effect หมายถึง Certificate defaults ใช้โดยไม่มี Filtering ขอแนะนำ: อย่า Fiddle กับเหล่านี้ ทั้งหมด
Safe practices
คำถามยากที่สุด: ใช้ EMET อย่างฉลาดอย่างไร? หากต้อง Manual changes และ Tweaks คุณ Invalidate Security software เพราะคุณกลายเป็น Weakest link ใน Chain คุณต้องการ EMET v4 รัน Smoothly ไม่มี Disruptions ต้อง Transparent ทั้งหมด สิ่งเดียวที่อาจสนใจคือ Occasional exception เช่น VLC, Skype ฯลฯ
กลับไปที่ข้อเสนอแนะก่อนหน้า: ใช้ First-time wizard ใช้ Recommended settings Add programs ของคุณ ให้ทุกอย่าง Work และ Run ตามคาด ให้ Simmer ไว้ระยะหนึ่ง เมื่อมั่นใจแล้ว อาจ Notch up เล็กน้อย ทีละขั้นตอน และ Examine software ทั้งหมดอย่างระมัดระวัง หาก Programs Crash หรือไม่ Function ให้ Disable mitigations ทีละตัว จนถึง Minimal level ที่ทำให้ Run ได้ดี
เรื่องนี้ Tedious แต่อย่าหतोฝ่าฟอน ประสบการณ์ของผมแสดงว่าแค่ 1-2 โปรแกรม ต้อง Adjust บ้าง VLC, Chrome, Skype เข้ามาในใจ ไม่เจอโปรแกรมอื่นที่ไม่ทำงานดี
เรื่อง Certificate Trust: Feature ใหม่และค่อนข้าง Experimental มุ่งเน้น Merging ของ Web และ App และสิ่งที่ Combo ทำได้บน Local host กล่าวคือ Software ซื้อผ่าน App store และ/หรือรันเป็น Web app อาจมี Potential ทำ Risky changes หรือถูก Exploit หาก Code ไม่ดี ข้างอีกมือ Mitigations Aggressive เกินไปอาจทำลาย User experience นั่นคือที่มาของ Trust idea
ประสบการณ์สั้นของผม: Default settings พอดี Browser security เพิ่มเติมได้ผ่าน Security extensions แต่นั้นเป็นหัวข้อแยก สรุป: ทิ้ง Certificate trust ไว้เหมือนเดิม Add sites ช้าๆ และระมัดระวัง หากจำเป็น และอย่าเปลี่ยน Pinning rules เพราะอาจได้ Weird และ Unexpected behavior
Enterprise deployment & profiles in depth
Protection Profiles พูดถึงตอน EMET version 3 จะ Recap สั้นๆ แต่ควรอ่านอย่างละเอียด Section นี้ครอบคลุม Group Policies สำหรับ Management ที่ง่ายขึ้น
EMET profiles อยู่ที่ Deployment\Protection Profiles ใน Default installation directory ใน XML form มี 3 profiles default: CertTrust.xml, Recommended Software.xml, Popular Software.xml
Profile หรือ Profile change ที่เพิ่ม वहां จะถูกใช้สร้าง Cross-section ของ Mitigations สำหรับ Applications ครั้งต่อไปที่ EMET Rereads rules Profiles ทดแทนได้เพื่อ Match Security granularity ใดๆ ที่ต้องการกับ EMET Format เช่น:
<Product Name="Windows Media player">
<Version Path="*\Windows Media Player\wmplayer.exe">
<Mitigation Name="SEHOP" Enabled="true" MinOS="6.1"/>
<Mitigation Name="MandatoryASLR" Enabled="false" />
<Mitigation Name="EAF" Enabled="false" />
</Version>
</Product>
<Product Name="Skype">
<Version Arch="x86" Path="*\Skype\Phone\Skype.exe">
<Mitigation Name="EAF" Enabled="false" />
</Version>
</Product>
นี่คืออะไร? XML มี Hierarchy structure ของ Value-key pairs ที่สุดท้ายสร้าง Profile logic มาดู 2 Sample rules จาก Popular Software.xml
Windows Media Player: Name definition Path มี Wildcard มี 3 Mitigations Listed และ Status false/true สำหรับ SEHOP มี Minimal OS version คือ Windows NT kernel version ที่ Mitigation นี้ใช้ได้ ถ้า Deploy profile ใน Windows XP จะไม่ทำงาน
Skype: Field ใหม่ Architecture Intel x86 หมายถึง Mitigation rules อาจไม่ทำงานบน Windows RT (ARM) บาง Mitigations ปิดไว้ เพราะ Microsoft รู้ว่าอาจทำให้ปัญหา เราพูดถึง Recommended settings คุณสามารถเปลี่ยนได้
นอกจากนี้ยังมี Defaults ไม่ต้อง Apply ทุกอย่างใหม่สำหรับทุก Application XML files มี Comment section ยาวค่อนข้าง ที่อธิบายใน Geek lingo ว่าสิ่งต่างๆ ทำงานจริงอย่างไร แต่คุณต้องการ Guide แบบมนุษย์อย่างนี้เพื่อเข้าใจให้ถูก Comment ยังมี Spelling errors อีกด้วย
สุดท้าย Group Policies: ได้ EMET.adml และ EMET.admx templates ใต้ Deployment\Group Policy Files สำหรับ Config hosts ใน Domain แต่ Tutorial นี้ aimed at Home users ข้าม Setup นี้ ไป Revisit หากมี Popular demand จริง
More reading
คุณจะ Wise ที่สุดหากอ่านทั้งหมดด้านล่างอย่างละเอียด:
Microsoft EMET v3 overview
Microsoft EMET v2 stuff
General safe web and mail security practices
Once upon a time, there was SuRun for Windows users
สรุป
ผมยืนยันคำพูด Microsoft EMET คือ Security toolbox ที่ดังที่สุดสำหรับ Windows Version 4 ไม่ใช่ข้อยกเว้น มันคือการสร้าง Fire-and-forget security setup ที่ไม่ Prompt คุณ Real-time ไม่ Toll resources ไม่ให้คุณทำ Silly yes/no mistakes ในขณะที่เสนอ Genuine, Proven security
นอกจากข้อความสำคัญนี้ คุณยังได้ Tutorial รายละเอียดมาก อธิบาย Ins and outs ของ Software และ Technology ที่เกี่ยวข้อง และวิธี Config EMET สำหรับ System และ Applications ของคุณ เพื่อให้เพลิดเพลินกับ Unobtrusive และ Efficient security setup หวังว่าชอบ มันไม่ได้ว่า ผม Negative กับ Microsoft ทุกอย่าง บางครั้งพวกเขาทำ Amazing products ได้ นั่นคือสิ่งที่มี
Cheers.
