

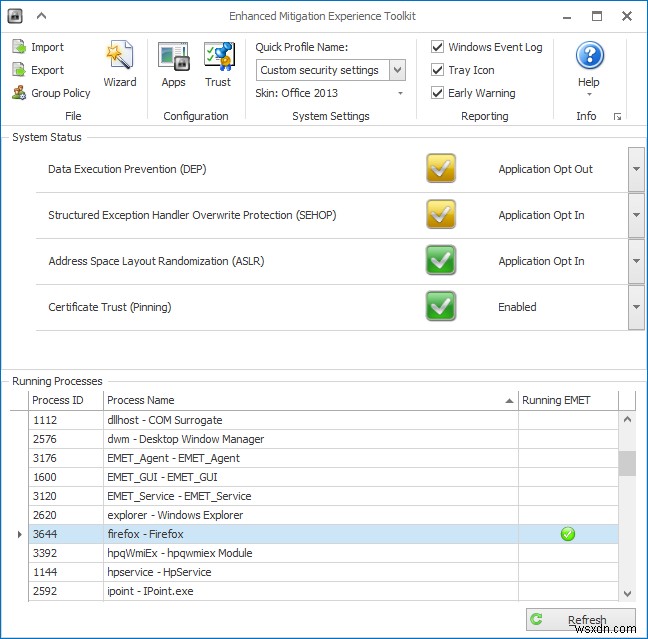
ตั้งแต่ Windows 10 Fall Creators Update (Build 1709) Enhanced Mitigation Experience Toolkit (EMET) ที่ยอดเยี่ยมและสง่างามที่สุด ไม่พร้อมใช้งานหรือติดตั้งบน OS นี้ได้อีกแล้ว แทนที่จะเป็น Standalone tool Mitigations เหล่านี้กลายเป็น Integral part ของ Windows 10
เพราะผมแฟน EMET ใหญ่ และใช้บน Windows machines ทั้งหมด ผมตัดสินใจเขียน Detailed, Practical, Real-life use guide สำหรับ Deploy และ Tweak Mitigations ใหม่ใน Windows 10 ตามมาถึง
สารบัญ
- Introduction & Preliminary reading
- Windows 10 Exploit Protection
- System settings
- Program settings
- Export และ Import Configuration
- Configuration file format
- Use old EMET configuration
- Application template
- Real-life usage และ Examples
- Import new configuration
- Configuration file contents
- Running และ Using exploit protection
- Edit และ Tweak configuration
- Overzealous protection
- Additional reading
- Conclusion
Introduction & Preliminary reading
หากคุณพบบทความนี้โดยบังเอิญ (ไม่น่าจะเป็นไปได้ เพราะ Niche และ Nerdy) ให้ผม Introduce EMET สั้นๆ: Utility ชุดนี้คือ System และ Program mechanisms ที่ป้องกัน Bad code ไม่ให้รัน บางครั้งสามารถ Stop และ Block Exploits ใน Running programs ได้
Microsoft Release EMET เป็น Standalone tool หลายปีก่อน สามารถ Deploy แบบ Manual บน System ไหนก็ได้ ยังคงมีใน Windows สองเวอร์ชันก่อนหน้าและ Windows 10 จนถึง Build 1709
EMET ทำงานโดย Restrict ประเภท Instructions และ Memory access ที่ Running programs สามารถ Execute ความงดงามของ Idea นี้คือมัน NOT Differentiate ระหว่าง Good programs และ Malware มัน Differentiate ระหว่าง Compliant (Legal code) และ Non-compliant (Illegal code) ดังนั้นแม้คุณจะมี Legitimate program อย่าง Chrome หรือ PowerPoint ที่ Encapsulated และ Protected โดย EMET libraries หากพวกเขา Misbehave เนื่องจาก Illegal instruction - ส่วนใหญ่เกิดจาก Mistake และ Sloppy programming practices หรือ Legacy constraints - EMET จะ Block execution และ Terminate program
สิ่งนี้ทำให้ EMET เป็น Security tool - หาก Configured ถูกต้อง คือ Fire-and-forget solution เบา Non-intrusive Extremely efficient และ Smart Concept การมอง Software จากมุมมอง Execution quality สายกว่าพยายาม Blacklist Bad programs
EMET ทำงานร่วมกับ System-level security mechanisms ใน Windows รวมถึง DEP, SEHOP, ASLR และอื่นๆ Very neat, Very handy, Supremely useful
ผมเขียน Tutorial ใช้ EMET แล้ว ทำด้วย Version 4 แต Guidelines 100% True และ Correct สำหรับ Later versions Review ล่าสุดของผมคือ Version 5.5 อ่านให้คุ้นเคย Concepts และ Protections ต่างๆ
แต่มัน No longer installable:
Windows 10 Exploit Protection
Functionality ของ EMET ตอนนี้พร้อมใน Windows 10 Build 1709 เป็น Built-in capability เข้าถึง UI ผ่าน Windows Defender Security Center ด้านซ้าย Sidebar คลิกไอคอนลำดับที่สองจากท้าย Scroll ลงท้ายรายการ คลิก Exploit protection settings
UI ใหม่ Simplified เทียบกับ EMET - และ Difficult to use มากกว่า เพราะ Less visibility ว่าอะไร Enabled อยู่ ไม่มี Full matrix-style view ของ Apps และ Enabled mitigations แต่ปล่อย Ergonomic considerations ไปก่อน โฟกัสที่ Raw functionality จะกลับมาพูดถึง Interface ควรปรับปรุงอย่างไรภายหลัง
System settings
Default view แสดง System settings เหมือน OS เก่าๆ Windows 10 มี Low-level mechanisms หลายอย่าง ป้องกัน Malicious (อ่านว่า Incorrect/Illegal) execution of code ไม่ได้พูด Malware โดยเฉพาะ พูดถึง Code ใดๆ ที่อาจทำให้ System crashes, Instability ฯลฯ
Protections 6 อย่างที่มาพร้อม Windows 10: CFG, DEP, Mandatory ASLR, Bottom-up ASLR, SEHOP, และ Heap integrity คล้ายกับที่ Windows เคยมี แต่ไม่มี Exact 1:1 translation เพราะมี Changes ใน Underlying kernel structures โดย Default ทั้งหมด ON
Program settings
คลิก Category ที่สอง จะ Expand รายการ Individual programs ที่ Exploit protection mechanism Cover เฉพาะ Programs ที่มี Overrides ถ้า Program มี Configuration ตรงกับ System defaults จะไม่ถูก Add
Windows 10 มาพร้อม Applications หลายตัวที่ Listed แล้วพร้อม Overrides ขณะนี้ควรทิ้งไว้ เพราะ Microsoft Configured แล้วสำหรับ Optimal security versus compatibility
Add programs ใหม่ได้ ทั้ง By path หรือ By name ตัวหล者ดีกว่า เพราะ Protect ทุก Version ของ Application ที่ Match Executable name ไม่ว่าจะ Install ที่ไหนบน Disk
เพิ่ม Program แล้ว Window ใหม่ Pop up ให้ Customize Exploit protection configuration มีรายการ Mitigations ยาวและ Confusing คุณสามารถ Turn on/off ได้แต่ละตัว จะสังเกตว่าบาง Protections Off by default และบางตัว On (มัก Match System config) Override defaults ได้
มี Mitigations ทั้งหมด 15 ตัว หาก Enable จะ Take precedence over System defaults มี Option Allow auditing - ถ้า Exception เกิดขึ้น System จะ Notify คุณ ต้อง Manual close/terminate program มิฉะนั้น System จะ Terminate programs ที่มี Illegal instructions matching mitigations
Export และ Import Configuration
ส่วนน่าสนใจและ Tricky: Mechanism ใหม่มาพร้อม Interface ที่ Cumbersome การ Config programs กลายเป็น Pain - พูดถึง 20-30 programs แต่ละตัวมี Mitigations สูงสุด 15 ตัว ใช้ Mouse clicks เยอะมาก
โชคดีที่ใช้ XML configuration files ได้ เพื่อ Update protections เร็วขึ้น Add/Remove programs, Tweak specific mitigations, Setup ได้ Quickly และ Efficiently ต้องเข้าใจ Basic format ของ Config file
ใน Main interface คลิก Export settings บันทึก XML file ใดๆ เปิดใน Text editor มาดู Configuration และ Directives/Values ต่างๆ
Configuration file format
Review:
<?xml version="1.0" encoding="UTF-8"?>
<root>
<SystemConfig>
<ASLR Enable="true" ForceRelocateImages="false" OverrideForceRelocateImages="false"></ASLR>
</SystemConfig>
<AppConfig Executable="DevicesFlow.exe">
<ExtensionPoints DisableExtensionPoints="true" OverrideExtensionPoint="false"></ExtensionPoints>
</AppConfig>
...
นี่คือบรรทัดแรกๆ ของ Actual configuration Indentation ช่วย Visually distinguish XML declaration บนสุด Root section Define block ที่มี System และ App configurations System configs declared by SystemConfig Apps declared by AppConfig Application names declared by variable Executable มี Mitigation types ต่างๆ: ExtensionPoints, Fonts, Payloads, DynamicCode, ฯลฯ ตัวอย่าง Almost full list สำหรับ Added application:
<AppConfig Executable="chrome.exe">
<StrictHandle Enable="true" OverrideStrictHandle="false"></StrictHandle>
<SystemCall DisableWin32kSystemCalls="false" OverrideSystemCall="false" Audit="true"></SystemCall>
<ExtensionPoints DisableExtensionPoints="true" OverrideExtensionPoint="false"></ExtensionPoints>
<DynamicCode BlockDynamicCode="false" AllowThreadsToOptOut="false" OverrideDynamicCode="false" Audit="true"></DynamicCode>
<Fonts DisableNonSystemFonts="false" AuditOnly="false" OverrideFontDisable="false" Audit="true"></Fonts>
<ImageLoad BlockRemoteImageLoads="false" OverrideBlockRemoteImageLoads="false" BlockLowLabelImageLoads="false" OverrideBlockLowLabel="false" AuditRemoteImageLoads="true" AuditLowLabelImageLoads="true"></ImageLoad>
<Payload EnableExportAddressFilter="true" OverrideExportAddressFilter="false" AuditEnableExportAddressFilter="true" EnableExportAddressFilterPlus="true" OverrideExportAddressFilterPlus="false" AuditEnableExportAddressFilterPlus="true" EnableImportAddressFilter="true" OverrideImportAddressFilter="false" AuditEnableImportAddressFilter="true" EnableRopStackPivot="true" OverrideEnableRopStackPivot="false" AuditEnableRopStackPivot="true" EnableRopCallerCheck="true" OverrideEnableRopCallerCheck="false" AuditEnableRopCallerCheck="true" EnableRopSimExec="true" OverrideEnableRopSimExec="false" AuditEnableRopSimExec="true"></Payload>
</AppConfig>
Ignore Actual values ไปก่อน เข้าใจ 3 Variables สำคัญ:
Value - true/false กำหนดว่า Mitigation enabled หรือไม่
Override - ตรงข้ามกับที่คิด: ไม่ได้บอกว่า Value ระบุ Override system defaults ไม่ใช่ นั่นเป็น Design แล้ว หากตัวนี้ True หมายถึงคุณ CANNOT edit settings ผ่าน UI Confusing มาก เพราะ False = คุณมี Control ผ่าน Defender Security Center, True = ไม่มี Control Best to ignore variable นี้
Audit - ว่า Program รันใน Audit mode หรือ Full enforced mode
พร้อม Basics แล้ว สร้าง Config file และ Import เข้า Exploits list โดย Import Old EMET config เพราะไม่อยากสูญเสีย Hard work
Use old EMET configuration
ใช้ Powershell Command line: Convert EMET config file เป็น New format แล้ว Import ต้องใช้ Powershell และ Admin access EMET file 長这样:
<EMET Version="5.1.5426.28431">
<Settings>
<ExploitAction Value="StopProgram" />
<AdvancedSettings DeepHooks="True" AntiDetours="True" BannedFunctions="True" />
<Reporting Telemetry="True" TrayIcon="True" EventLog="True" />
<SystemSettings DEP="Application Opt Out" SEHOP="Application Opt Out" ASLR="Application Opt In" Pinning="Enabled" />
</Settings>
<EMET_Apps>
<AppConfig Path="*" Executable="7z.exe">
<Mitigation Enabled="true" />
<Mitigation Enabled="true" />
<Mitigation Enabled="true" />
<Mitigation Enabled="true" />
Format นี้ Cleaner และ Nicer แต่ไม่เป็นไร Convert config file: อ่าน Online documentation ต้องใช้ Command:
ConvertTo-ProcessMitigationPolicy -EMETFilePath emetconfig.xml -OutputFilePath newconfig.xml
ได้ Errors เยอะ:
Error: Should read Win10 setting for some reason?: PinRuleMember
Error: Should read Win10 setting for some reason?: Active
Error: Should read Win10 setting for some reason?: PinnedSite
Error: Should read Win10 setting for some reason?: Domain
Error: Should read Win10 setting for some reason?: PinRuleMember
Error: Should read Win10 setting for some reason?: Active
Pinning rules สำหรับ Certificates ใน Pre-Windows 10 rules ไม่ Compatible กับ Format ใหม่ หาก Import config นี้จะ Fail ต้อง Clean up XML ก่อน Convert ใหม่
<Pinning>
<PinRules>
<PinRule>
<ID>{392c02ca-a7dd-49e3-888f-7fb505de9333}</ID>
<Name>FacebookCA</Name>
...
Note: ไม่มี Exact 1:1 match ระหว่าง EMET และ New exploit protection mechanism โดยเฉพาะหาก Move across multiple OSes แนะนำ: ใช้ Old config เป็น Advisory only
Converted file จะ长这样 - ในแง่ App mitigations:
<AppConfig Executable="AcroRd32.exe">
<DEP Enable="true" EmulateAtlThunks="false"/>
<ASLR ForceRelocateImages="false" RequireInfo="false" BottomUp="true" HighEntropy="false"/>
<StrictHandle Enable="false"/>
<SystemCalls DisableWin32kSystemCalls="false" Audit="false"/>
<ExtensionPoints DisableExtensionPoints="false"/>
<DynamicCode BlockDynamicCode="false" AllowThreadsToOptOut="false" Audit="false"/>
<ControlFlowGuard Enable="false" SuppressExports="false" StrictControlFlowGuard="false"/>
<SignedBinaries MicrosoftSignedOnly="false" AllowStoreSignedBinaries="false" EnforceModuleDependencySigning="false" Audit="false" AuditStoreSigned="false" AuditEnforceModuleDependencySigning="false"/>
<Fonts DisableNonSystemFonts="false" Audit="false"/>
<ImageLoad AuditPreferSystem32="false" AuditLowLabelImageLoads="false" AuditRemoteImageLoads="false" PreferSystem32="false" BlockLowLabelImageLoads="false" BlockRemoteImageLoads="false"/>
<Payload EAFModules="" EnableExportAddressFilter="true" AuditEnableExportAddressFilter="false" EnableExportAddressFilterPlus="true" AuditEnableExportAddressFilterPlus="false" EnableImportAddressFilter="false" AuditEnableImportAddressFilter="false" EnableRopStackPivot="true" AuditEnableRopStackPivot="false" EnableRopCallerCheck="true" AuditEnableRopCallerCheck="false" EnableRopSimExec="true" AuditEnableRopSimExec="false"/>
<SEHOP Enable="true" TelemetryOnly="false" Audit="false"/>
<Heap TerminateOnError="true"/>
<ChildProcess DisallowChildProcessCreation="false" Audit="false"/>
</AppConfig>
Application template
Mitigations ส่วนใหญ่จาก EMET Import จะเป็น False น่าเสียดาย - และ System ones ไม่ Match เต็มที่แล้ว แนะนำ: Six system mitigations ครอบคลุม Basics สามารถ Enable เพิ่มอีก Six mitigations ที่ Match 1:1 ระหว่าง EMET และ New protection mechanism: EAF, EAF+, IAF, StackPivot, CallerCheck, SimExec ดังนั้น Basic template สำหรับ Applications จากการใช้งานก่อนหน้า:
<?xml version="1.0" encoding="UTF-8"?>
<root>
<AppConfig Executable="executable.exe">
<Payload EnableExportAddressFilter="true" EnableExportAddressFilterPlus="true" EnableImportAddressFilter="true" EnableRopStackPivot="true" EnableRopCallerCheck="true" EnableRopSimExec="true">
</Payload>
</AppConfig>
</root>
ขยายด้วย Fonts protection (Format สำหรับ Visual clarity):
<?xml version="1.0" encoding="UTF-8"?>
<root>
<AppConfig Executable="executable.exe">
<Fonts DisableNonSystemFonts="true" AuditOnly="false" OverrideFontDisable="false" Audit="false"></Fonts>
<Payload EnableExportAddressFilter="true" EnableExportAddressFilterPlus="true" EnableImportAddressFilter="true" EnableRopStackPivot="true" EnableRopCallerCheck="true" EnableRopSimExec="true">
</Payload>
</AppConfig>
</root>
Template section สำหรับ Baseline:
<?xml version="1.0" encoding="UTF-8"?>
<root>
<AppConfig Executable="executable.exe">
<Fonts DisableNonSystemFonts="true" AuditOnly="false" OverrideFontDisable="false" Audit="false"></Fonts>
<Payload EnableExportAddressFilter="true" EnableExportAddressFilterPlus="true" EnableImportAddressFilter="true" EnableRopStackPivot="true" EnableRopCallerCheck="true" EnableRopSimExec="true"></Payload>
</AppConfig>
</root>
Real-life usage และ Examples
จนถึงตอนนี้ Cover: New UI, System/Program settings, Overview new exploit mitigations, Export/Import XML, Convert old EMET settings ตอนนี้ Import App templates และใช้
ใช้ App template ด้านบน Quickly และ Elegantly เพิ่ม Applications ใหม่เข้า System list จดไว้: System settings ควรทิ้งไว้ที่ Defaults พวกเขา Cover deal มากแล้ว บวก Six mitigations อื่นๆ ที่ Match ใกล้เคียง น่าจะทำงานดี นี่คือ MAIN reason ที่ผมเลือก Baseline นี้ บวก Fonts ที่ Make sense และไปพร้อมกับ Vulnerabilities เก่าบน Issue นี้
มี Mitigations อื่นๆ ที่ Enable ได้ แต่ถ้าไม่ Fully understand อาจ Cripple programs Developers ของ Software เองก็อาจไม่รู้ว่า App ของพวกเขาทำผิดอะไร ดังนั้นอาจไม่หา Easy answer ได้
- ACG, Low integrity และ Remote images - ควร OK
- Code integrity guard - เว้นแต่ Signed by Microsoft Images ไม่รัน - นี้คือ Windows 10 S ไม่แนะนำ
- Extension points - น่าจะ Cause problems ในการ Run software
- Disable system calls - Highly likely to cause problems
- Child processes - Definitely cripple programs
- Handle usage - Likely cause problems กับ Sloppily designed software
ส่วนที่เหลือเรา Covered แล้ว - Six basics, Six old mitigations, Fonts, และ Potential three ใน Bullet แรก ส่วนที่เหลือ Best left alone
Import new configuration
ทำได้ดังนี้ อีกครั้งจาก Powershell ด้วย Admin credentials:
Set-ProcessMitigation -PolicyFilePath .\config.xml
Configuration file contents
จาก Template เพิ่ม Applications ลงใน File สร้าง Single configuration หลาย Programs แล้ว Import ครั้งเดียว หรือ Per-app template Multiple imports ไม่ต่างกัน
พิจารณา: 1) ทำได้กับ Security Center รันอยู่ แต่จะ NOT Show changes on-the-fly Config โหลดครั้งเดียว และ/หรือเมื่อทำ Changes ผ่าน UI 2) Old app settings จะถูก Remove ด้วย New ones
Running และ Using exploit protection
ทดสอบกับ: Firefox, LibreOffice, VLC, IrfanView, Notepad++ รันได้ไม่มีปัญหา รวมถึง Updates Google Chrome ไม่รันด้วย ANY mitigation enabled ยกเว้น Fonts - Pages และ Extensions Crash ตลอด Contrast กับ EMET behavior ไม่มี Golden list ว่าอะไรทำงาน อะไรไม่ แต่ผมเชื่อว่า 7/15 หรือ 10/15 mitigations enabled ได้ Code signing, Child processes, System calls disabling ไม่จำเป็น เหลือแค่ Extension points และ Handle usage ที่อาจต้องดูใกล้ชิด Pretty good
Edit และ Tweak configuration
กลับไป Edit ได้ตลอด - ผ่าน GUI หลัง Import bulk configuration ตอนนี้ Fine tuning ถ้าไม่ Work Remove entry และ Start fresh
Overzealous protection
หาก Go wild (ผมลอง เพื่อดู) อาจ Cripple programs จนรันไม่ได้ มัน Easy เกินไป จงระมัดระวังอย่างสุด ตรวจสอบว่าคุณเข้าใจว่ากำลังทำอะไร Long-term investment ทำดีครั้งเดียว ไม่มีปัญหาต่อไป
Additional reading
Official Microsoft articles:
Apply mitigations to help prevent attacks through vulnerabilities
Customize exploit protection
สรุป
นี่คือ Very thorough, Hands-on, Real-life guide ใช้ New exploit protection mechanism ใน Windows 10 เราไม่ได้แค่มอง List และ Wonder Magic เราไป Behind the scene ได้ Autographs บนหน้าอก
Technical note: เราเรียนรู้ Exploit mechanism, New UI, System/Program settings, Types of exploits และ Roughly what they do, Export/Import XML config files, สร้าง Work template, Convert และ Use old EMET settings, พยายาม Match Protection level ของ EMET ขณะยังคง Sane และ Practical functionality กับ Most programs และ Most mitigations มี Coverage ประมาณ 80-90% โดยไม่ Break things ไม่มี Guarantees แต่ไกลกว่า Conventional security software มาก
Mitigation protection ยังคือ Best product ของ Microsoft ไกลโพ้น และหวังว่าจะ Improve workflow ให้ Accessible ให้ Advanced users ตอนนี้คุณมี Guide นี้ หวังว่าทำให้ Journey ใน Post-EMET world ของ Mitigations เรียบง่ายและรวดเร็วขึ้น และ Apps ของคุณยังทำงานอยู่! See you.
ถ้าชอบ Tutorial ให้ Support Dedoimedo นะ? Cheers.
