

บทความนี้จะแนะนำการตั้งค่า High-Available Failover Configuration ของ Squid (Linux) Proxy Servers 2 ตัว เพื่อเข้าถึง Internet จาก Corporate LAN จะสร้าง HA Cluster ด้วย keepalived
HA Cluster คือกลุ่ม Servers ที่มี Redundancy Built-in เพื่อลด App Downtime ต่ำสุดกรณี Hardware หรือ Software Issues ของ Server ใดๆ ในกลุ่ม ตามนิยามนี้ ต้อง Implement ต่อไปนี้สำหรับ HA Cluster ที่ทำงานถูกต้อง:
- Server State Check
- Automatic Switching ของ Resources กรณี Server Failure
Keepalived เปิดใช้งานทั้ง 2 อย่าง Keepalived คือ System Daemon ใน Linux Systems ที่เปิดใช้งาน Service Failover และ Load Balancing Failover ทำได้โดย Floating IP Address ที่ Switch ไป Server อีกตัวถ้า Main Fail เพื่อ Switch IP Address ระหว่าง Servers อัตโนมัติ keepalived ใช้ VRRP (Virtual Router Redundancy Protocol – https://www.ietf.org/rfc/rfc2338.txt)
หลักการทำงานของ VRRP
มาดู Theory และ VRRP Definitions หลัก:
- VIP — Virtual IP, Virtual IP Address ที่สามารถ Switch ระหว่าง Servers อัตโนมัติกรณี Failure
- Master — Server ที่ VIP Active อยู่ปัจจุบัน
- Backup — Servers ที่ VIP จะ Switch ไปกรณี Master Fail
- VRID — Virtual Router ID, Servers ที่แชร์ Virtual IP (VIP) จะสร้าง Virtual Router และ Unique Identifier มีค่า 1-255 Server อาจอยู่ใน Multiple VRIDs พร้อมกัน แต่ทุก VRID ต้องมี Virtual IP Address ที่ Unique
Basic Operation Algorithm:
- ทุกช่วงเวลาคงที่ Master Server ส่ง VRRP Packets (heartbeats) ไป Multicast Address 224.0.0.18 และ Slave Servers ทั้งหมด Listen ที่ Address นี้ Multicast หมายถึง 1 Sender หลาย Recipients Hint. เพื่อให้ Servers ทำงานใน Multicast Mode Network Equipment ต้องรองรับ Multicast Traffic
- หาก Slave Server ไม่ได้รับ Heartbeat Packets ใดๆ จะเริ่ม Master Selection Procedure หาก Server กลายเป็น Master ตาม Priority จะ Activate VIP และส่ง Gratuitous ARP Gratuitous ARP คือ ARP Response แบบพิเศษที่ Update MAC Table บน Network Switches แจ้งการเปลี่ยนแปลง Virtual IP Address Owner และ MAC Address ที่ Redirect Traffic ไป
ติดตั้งและตั้งค่า keepalived บน CentOS
จะติดตั้งและตั้งค่า keepalived บน Linux Servers 2 ตัว (proxy-serv01 และ proxy-serv02) รัน CentOS 7 พร้อม Squid Installed ใน Scheme จะใช้ Load Balancing Method เรียบง่ายที่สุด — Round Robin DNS Method นี้หมายถึง Single DNS Name มี Multiple Registered IP Addresses และ Clients ได้ Addresses ทีละตัว จึงต้องการ 2 Virtual IP Addresses ลงทะเบียนสำหรับ 1 DNS Name (proxy-serv) Network Diagram:
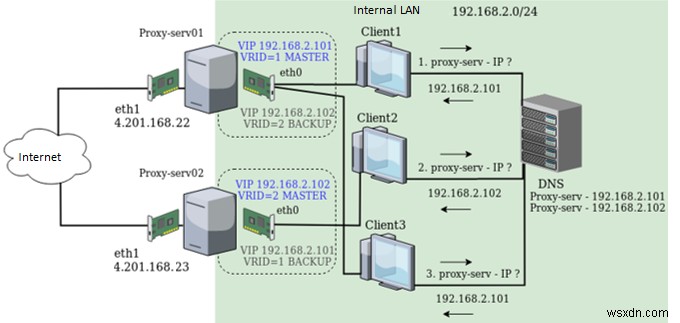
แต่ละ Linux Server มี Physical Network Interfaces 2 ตัว: eth1 ด้วย Public (White) IP Address และ eth0 ใน Local Network
Real Server IP Addresses:
192.168.2.251 — for proxy-server01
192.168.2.252 — for proxy-server02
Virtual IP Addresses ที่ Switch ระหว่าง Servers อัตโนมัติกรณี Failure:
192.168.2.101
192.168.2.102
สำคัญ ตอน Config VRRP ห้ามใช้ Real Server IP Address เป็น Virtual IP เพราะถ้า Server Fail Address จะ Move ไป Server ถัดไป และหลัง Failback Server ตัวแรกอาจ Isolated จาก Network เพราะต้องส่ง VRRP Packets ไป Network แต่ไม่มี IP Address ส่งได้
ติดตั้ง keepalived บนทั้ง 2 Servers ด้วย yum Package Manager (หรือ dnf บน CentOS 8):
# yum install keepalived
หลังติดตั้งเสร็จทั้ง 2 Servers เปลี่ยน Keepalived Config File บนทั้ง 2 Servers:
# nano /etc/keepalived/keepalived.conf
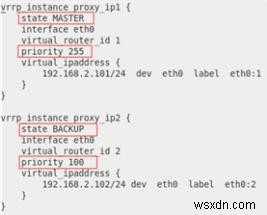
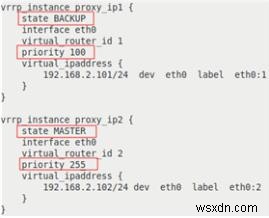
บรรทัดที่มี Parameter ต่างกันไฮไลท์:
| proxy-serv01 | proxy-serv02 |
|---|---|
 |
 |
อธิบาย Options รายละเอียด:
- vrrp_instance <name> — Section ที่ Define VRRP Instance
- state <MASTER|BACKUP> — Initial Node State ตอน Startup
- interface <interface name> — Interface ที่ VRRP รันอยู่
- virtual_router_id <number 0-255> — Unique VRRP Instance Identifier ต้องเหมือนกันทุก Servers
- priority <number 0-255> — ตั้ง Server Priority Server ที่ Priority สูงกว่าเป็น MASTER
- virtual_ipaddress — Block ของ Virtual IP Addresses ที่ Active บน Server ใน MASTER State ต้องเหมือนกันทุก Servers ใน VRRP Instance
Note พบหลายตัวอย่างใช้ Option authentication ใน VRRP Config แต่ Keepalived Documentation กล่าวว่า Authentication ถูกลบออกจาก VRRPv2 ใน RFC3768 Spec (https://tools.ietf.org/html/rfc3768) ในปี 2004 เนื่องจากไม่ให้ Real Security ไม่แนะนำให้ใช้ Option นี้
หาก Network Config ปัจจุบันไม่รองรับ Multicast keepalived มี Unicast Option คือ VRRP Heartbeat Packets จะส่งไป Servers โดยตรงตาม List ต้องใช้ Options:
- unicast_src_ip — Source Address สำหรับ VRRP Packets
- unicast_peer — Block ของ Server IP Addresses ที่ VRRP Packets จะส่งไป
Config ของเรากำหนด 2 VRRP Instances คือ proxy_ip1 และ proxy_ip2 ในการทำงานปกติ proxy-serv01 จะเป็น MASTER สำหรับ Virtual IP 192.168.2.101 และ BACKUP สำหรับ 192.168.2.102 และในทางกลับกัน proxy-serv02 จะเป็น MASTER สำหรับ 192.168.2.102 และ BACKUP สำหรับ 192.168.2.101
หาก Firewall Active บน Server ต้อง Add Allow Rules สำหรับ Multicast Traffic และ VRRP ด้วย iptables:
# iptables -A INPUT -i eth0 -d 224.0.0.0/8 -j ACCEPT
# iptables -A INPUT -p vrrp -i eth0 -j ACCEPT
Enable keepalived Service สำหรับ Autostart บน Boot และ Run บนทั้ง 2 Servers
# systemctl enable keepalived
# systemctl start keepalived
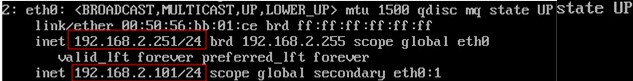
หลัง keepalived Start แล้ว Virtual IP Addresses จะ Assign ให้ Interfaces จาก Config File มาดู Current eth0 IP Addresses ของ Servers:
# ip a show eth0
บน proxy-serv01:
บน proxy-serv02:
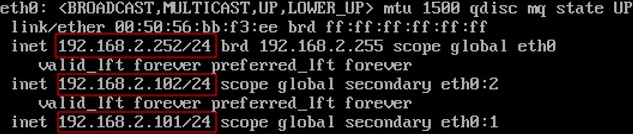
วิธี Healthcheck App หรือ Interface ด้วย Keepalived
VRRP Protocol ให้ Server State Monitoring เช่นกรณี Physical Server Failure หรือ Switch/Server NIC Port แต่อย่างอื่นอาจเกิดขึ้น:
- Proxy Server (หรือ App อื่น) Error — Clients เข้าถึง Virtual Address ของ Server จะได้ Error ใน Browser ว่า Proxy Server Unavailable
- Internet Access Failure ของ Interface ตัวที่สอง — Clients ได้ Error ว่า Connection Could Not Be Established
เพื่อ Handle สถานการณ์ด้านบน ใช้ Options:
- track_interface — Monitor Interface State และ Set FAULT State สำหรับ VRRP Instance หาก Interface ใน List เป็น DOWN
- track_script — Healthcheck HA App ด้วย Script ที่ Return 0 ถ้า Check สำเร็จ หรือ 1 ถ้า Check Failed
Update Config เพิ่ม eth1 Interface Monitoring (โดย Default VRRP Instance จะ Check Interface ที่ Bind ไว้ คือ eth0 ใน Config ปัจจุบัน)
track_interface { eth1 }
Track_script Directive รัน Script ด้วย Parameters ที่กำหนดโดย vrrp_script Block ใน Format:
vrrp_script <name> {
  script "<path to executable file>"
  interval <number, seconds> - Periodicity รัน Script, 1 วินาที Default
  fall <number> - จำนวนครั้งที่ Script Return ค่าต่างจาก 0 เพื่อ Switch ไป FAULT State
  rise <number> - จำนวนครั้งที่ Script Return 0 เพื่อออกจาก FAULT State (Failback)
  timeout <number> - เวลารอจน Script Return Result (ถ้า Timeout Script Return Non-zero)
  weight <number> - ค่าที่ Server Priority จะลดลงกรณีได้ FAULT State Default 0 หมายถึง Server ได้ FAULT State หลัง Script Failed จำนวนครั้งใน Fall Parameter
}
Config Squid Proxy Health Checking ด้วยคำสั่งตรวจสอบว่า Squid Process Active:
# squid -k check
สร้าง vrrp_script รันทุก 3 วินาที Block นี้ Define นอก vrrp_instance Blocks:
vrrp_script chk_squid_service {
  script "/usr/sbin/squid -k check"
  interval 3
}
เพิ่ม Script เข้า Monitoring ในทั้ง 2 vrrp_instance Blocks:
track_script { chk_squid_service }
หาก Squid Fail Virtual IP Address จะ Switch ไป Server อื่น
สามารถระบุ Additional Actions ที่ทำเมื่อ Server State เปลี่ยน:
หาก Squid Config รับ Connections จาก Interface ใดๆ คือ http_port 0.0.0.0:3128 จะไม่มีปัญหาเวลา Virtual IP Switch และ Squid จะรับ Connections ที่ Address ใหม่ แต่ถ้า Config Specific IP Addresses เช่น:
http_port 192.168.2.101:3128
http_port 192.168.2.102:3128
Squid จะไม่รู้ว่า Address ใหม่ปรากฏในระบบให้ Listen Client Requests เพื่อ Handle สถานการณ์ที่ต้อง Additional Actions เวลา Virtual IP Switch keepalived อนุญาตรัน Script ถ้า Server State เปลี่ยน เช่น MASTER เป็น BACKUP หรือกลับกัน ใช้ Option:
notify "path to executable file"
ทดสอบ Keepalived Failover กรณี Failure
หลัง Config Virtual IPs ตรวจสอบว่า Failures ถูก Handle ถูกต้อง Check แรก Simulation Server Failure Disable eth0 บน proxy-serv01 จะหยุดส่ง VRRP Heartbeat Packets proxy-serv02 ต้อง Activate Virtual IP 192.168.2.101 Check ด้วย:
# ip a show eth0
บน proxy-serv01:

บน proxy-serv02:
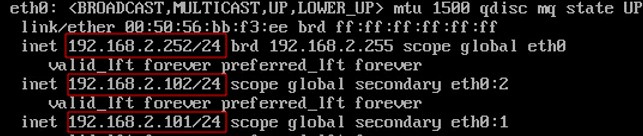
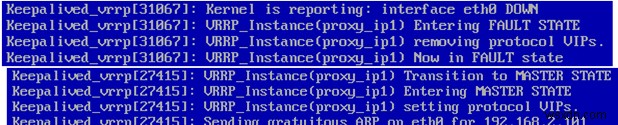
ตามคาด proxy-serv02 Activate Virtual IP 192.168.2.101 ดู Logs:
cat /var/log/messages | grep -i keepalived
| on proxy-serv01 | on proxy-serv02 |
|---|---|
Keepalived_vrrp[xxxxx]: Kernel is reporting: interface eth0 DOWN Keepalived_vrrp[xxxxx]: VRRP_Instance(proxy_ip1) Entering FAULT STATE Keepalived_vrrp[xxxxx]: VRRP_Instance(proxy_ip1) removing protocol VIPs. Keepalived_vrrp[xxxxx]: VRRP_Instance(proxy_ip1) Now in FAULT state |
Keepalived_vrrp[xxxxx]: VRRP_Instance(proxy_ip1) Transition to MASTER STATE |
| Keepalived ได้ Signal eth0 DOWN Set FAULT State proxy_ip1 VRRP Instance ปลด VIPs | Keepalived Set MASTER State proxy_ip1 Activate IP 192.168.2.101 บน eth0 ส่ง Gratuitous ARP |
ตรวจสอบว่า Enable eth0 บน proxy-serv01 อีกครั้ง Virtual IP 192.168.2.101 Switch กลับ
| on proxy-serv01 | on proxy-serv02 |
|---|---|
Keepalived_vrrp[xxxxx]: VRRP_Instance(proxy_ip1) forcing a new MASTER election Keepalived_vrrp[xxxxx]: VRRP_Instance(proxy_ip1) Transition to MASTER STATE Keepalived_vrrp[xxxxx]: VRRP_Instance(proxy_ip1) Entering MASTER STATE Keepalived_vrrp[xxxxx]: VRRP_Instance(proxy_ip1) setting protocol VIPs. Keepalived_vrrp[xxxxx]: Sending gratuitous ARP on eth0 for 192.168.2.101 |
Keepalived_vrrp[xxxxx]: VRRP_Instance(proxy_ip1) Received advert with higher priority 255, ours 100 Keepalived_vrrp[xxxxx]: VRRP_Instance(proxy_ip1) Entering BACKUP STATE Keepalived_vrrp[xxxxx]: VRRP_Instance(proxy_ip1) removing protocol VIPs. |
| Keepalived ได้ Signal eth0 Back เริ่มเลือก MASTER proxy_ip1 VRRP Instance หลังได้ MASTER State Activate IP 192.168.2.101 ใน eth0 ส่ง Gratuitous ARP | Keepalived ได้ Packet Priority สูงกว่า proxy_ip1 Switch เป็น BACKUP State ปลด IPs |
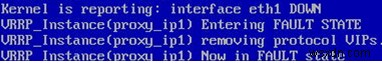
Check ที่ 2 Simulation External Network Interface Failure Disable eth1 บน proxy-serv01 ดูผลใน Logs
| on proxy-serv01 | on proxy-serv02 |
|---|---|
Keepalived_vrrp[xxxxx]: Kernel is reporting: interface eth1 DOWN Keepalived_vrrp[xxxxx]: VRRP_Instance(proxy_ip1) Entering FAULT STATE Keepalived_vrrp[xxxxx]: VRRP_Instance(proxy_ip1) removing protocol VIPs. Keepalived_vrrp[xxxxx]: VRRP_Instance(proxy_ip1) Now in FAULT state |
Keepalived_vrrp[xxxxx]: VRRP_Instance(proxy_ip1) Transition to MASTER STATE Keepalived_vrrp[xxxxx]: VRRP_Instance(proxy_ip1) Entering MASTER STATE Keepalived_vrrp[xxxxx]: VRRP_Instance(proxy_ip1) setting protocol VIPs. Keepalived_vrrp[xxxxx]: Sending gratuitous ARP on eth0 for 192.168.2.101 |
| Keepalived ได้ Signal eth1 DOWN Set FAULT State proxy_ip1 ปลด VIPs | Keepalived Set MASTER State proxy_ip1 Activate IP 192.168.2.101 ใน eth0 ส่ง Gratuitous ARP |
Check ที่ 3 Simulation Squid Failure หยุด Service Manual:
# systemctl stop squid
ดูผลใน Logs:
| on proxy-serv01 | on proxy-serv02 |
|---|---|
Keepalived_vrrp[xxxxx]: VRRP_Script(chk_squid_service) failed Keepalived_vrrp[xxxxx]: VRRP_Instance(proxy_ip1) Entering FAULT STATE Keepalived_vrrp[xxxxx]: VRRP_Instance(proxy_ip1) removing protocol VIPs. Keepalived_vrrp[xxxxx]: VRRP_Instance(proxy_ip1) Now in FAULT state |
Keepalived_vrrp[xxxxx]: VRRP_Instance(proxy_ip1) Transition to MASTER STATE Keepalived_vrrp[xxxxx]: VRRP_Instance(proxy_ip1) Entering MASTER STATE Keepalived_vrrp[xxxxx]: VRRP_Instance(proxy_ip1) setting protocol VIPs. Keepalived_vrrp[xxxxx]: Sending gratuitous ARP on eth0 for 192.168.2.101 |
| Script Check Squid Activity Return Error Keepalived Set FAULT State proxy_ip1 ปลด VIPs | Keepalived Set MASTER State proxy_ip1 Activate IP 192.168.2.101 ใน eth0 ส่ง Gratuitous ARP |
ทั้ง 3 Checks ผ่านสำเร็จ keepalived Config ถูกต้อง ภายหลังจะ Config HA Cluster ด้วย Pacemaker และเปรียบเทียบ Features
Final Config File /etc/keepalived/keepalived.conf สำหรับ proxy-serv01:
vrrp_script chk_squid_service {
  script "/usr/sbin/squid -k check"
  interval 3
}
vrrp_instance proxy_ip1 {
  state MASTER
  interface eth0
  virtual_router_id 1
  priority 255
  virtual_ipaddress {
    192.168.2.101/24 dev eth0 label eth0:1
  }
  track_interface { eth1 }
  track_script { chk_squid_service }
}
vrrp_instance proxy_ip2 {
  state BACKUP
  interface eth0
  virtual_router_id 2
  priority 100
  virtual_ipaddress {
    192.168.2.102/24 dev eth0 label eth0:2
  }
  track_interface { eth1 }
  track_script { chk_squid_service }
}
Final Config File /etc/keepalived/keepalived.conf สำหรับ proxy-serv02:
vrrp_script chk_squid_service {
  script "/usr/sbin/squid -k check"
  interval 3
}
vrrp_instance proxy_ip1 {
  state BACKUP
  interface eth0
  virtual_router_id 1
  priority 100
  virtual_ipaddress {
    192.168.2.101/24 dev eth0 label eth0:1
  }
  track_interface { eth1 }
  track_script { chk_squid_service }
}
vrrp_instance proxy_ip2 {
  state MASTER
  interface eth0
  virtual_router_id 2
  priority 255
  virtual_ipaddress {
    192.168.2.102/24 dev eth0 label eth0:2
  }
  track_interface { eth1 }
  track_script { chk_squid_service }
}
