

คำสั่ง Get-ADUser ใน PowerShell ช่วยให้คุณดึงข้อมูลผู้ใช้ Active Directory ได้ รวมถึงแอตทริบิวต์ต่างๆ และการค้นหาผู้ใช้ในโดเมน นี่เป็นหนึ่งใน Cmdlet ยอดนิยมสำหรับการดึงข้อมูลจาก AD โดย Get-ADUser สามารถดึงค่าแอตทริบิวต์ใดๆ ของบัญชีผู้ใช้ AD แสดงรายการผู้ใช้พร้อมแอตทริบิวต์ ส่งออกรายงานเป็นไฟล์ CSV และกรองผู้ใช้ด้วยเกณฑ์ต่างๆ ได้
Cmdlet Get-ADUser ในโมดูล Active Directory PowerShell
Cmdlet Get-ADUser อยู่ในโมดูลเฉพาะสำหรับจัดการ Active Directory คือ Active Directory Module for Windows PowerShell Cmdlet ของโมดูล RSAT-AD-PowerShell ช่วยให้คุณดำเนินการกับออบเจ็กต์ AD ได้หลากหลาย
หมายเหตุ ก่อนหน้านี้การดูแอตทริบิวต์บัญชีผู้ใช้ AD ต้องใช้เครื่องมือหลายอย่าง: คอนโซล ADUC (รวมถึงคิวรี AD ที่บันทึกไว้) สคริปต์ VBS, dsquery เป็นต้น ทั้งหมดนี้สามารถแทนที่ด้วย Get-ADUser ได้อย่างง่ายดาย
ในตัวอย่างนี้ เราจะแสดงวิธีใช้ Get-ADUser เพื่อดูข้อมูลเวลาที่เปลี่ยนรหัสผ่านล่าสุด วันหมดอายุของรหัสผ่าน และคุณสมบัติอื่นๆ ของผู้ใช้
เพื่อใช้โมดูล RSAT-AD-PowerShell ให้เปิด PowerShell ด้วยสิทธิ์ผู้ดูแลระบบและนำเข้าโมดูลด้วยคำสั่ง:
Import-Module ActiveDirectory
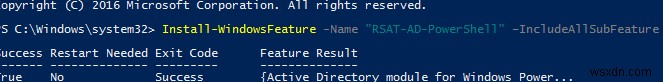
โมดูล RSAT-AD-PowerShell ติดตั้งโดยอัตโนมัติบน Windows Server 2012 (และใหม่กว่า) เมื่อปรับใช้บทบาท AD DS บนเซิร์ฟเวอร์ที่เป็นสมาชิกโดเมน ให้รันคำสั่ง:
Install-WindowsFeature -Name "RSAT-AD-PowerShell" –IncludeAllSubFeature
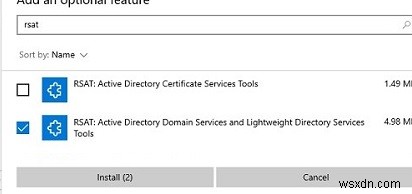
สำหรับ Windows 10/11 ให้ติดตั้ง RSAT 版本ที่เหมาะสม ผ่าน Settings > Apps > Optional Features > Add a feature > RSAT: Active Directory Domain Services and Lightweight Directory Services Tools
หรือติดตั้งผ่าน PowerShell:
Add-WindowsCapability –online –Name "Rsat.ActiveDirectory.DS-LDS.Tools~~~~0.0.1.0"
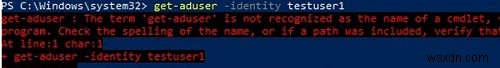
หากไม่ได้ติดตั้งโมดูล จะเกิดข้อผิดพลาด:
Get-ADUser: The term 'get-aduser' is not recognized as the name of a cmdlet, function, script file, or operable program. Check the spelling of the name, or if a path was included, verify that the path is correct and try again.
ตรวจสอบการติดตั้งและนำเข้าโมดูล:
Import-Module ActiveDirectory
ยังมีวิธีใช้โมดูล AD PowerShell โดยไม่ติดตั้ง RSAT คือ คัดลอกไฟล์โมดูลหลักและนำเข้า:
Import-Module "C:\PS\AD\Microsoft.ActiveDirectory.Management.dll"
 Import-Module "C:\PS\AD\Microsoft.ActiveDirectory.Management.resources.dll"
ดูอาร์กิวเมนต์ทั้งหมดของ Get-ADUser ได้ด้วย:
help Get-ADUser
ค้นหาผู้ใช้ AD และแสดงคุณสมบัติด้วย Get-ADUser
การใช้ Get-ADUser ไม่จำเป็นต้องรันด้วยสิทธิ์ Domain Admin ผู้ใช้โดเมนทั่วไปสามารถดูค่าแอตทริบิวต์ส่วนใหญ่ได้ (ยกเว้นข้อมูลที่เป็นความลับ เช่น LAPS) หากต้องการรันด้วยบัญชีอื่น ใช้พารามิเตอร์ -Credential
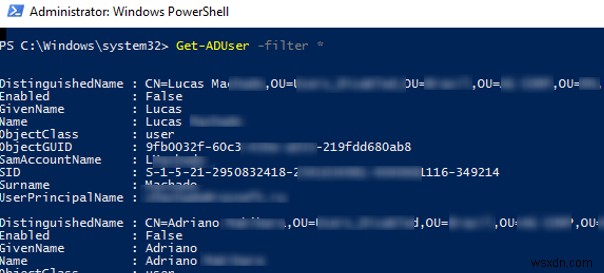
แสดงบัญชีผู้ใช้ทั้งหมดในโดเมน:
Get-ADUser -filter *
สำคัญ ไม่แนะนำให้รันคำสั่งนี้ในโดเมนที่มีจำนวนผู้ใช้มาก เพราะอาจทำให้โดเมนคอนโทรลเลอร์ทำงานหนักเกินไป
ใช้ Set-ADUser เพื่อแก้ไขแอตทริบิวต์ผู้ใช้
แสดงคุณสมบัติของผู้ใช้เฉพาะคน ใช้พารามิเตอร์ –Identity ซึ่งสามารถเป็นชื่อผู้ใช้, SAMAccountName, DN, SID หรือ GUID ได้:
Get-ADUser –Identity b.smith
 Get-ADUser –Identity "CN=Brian Smith,OU=Users,OU=Berlin,DC=woshub,DC=loc"
 Get-ADUser –Identity "Brian Smith"
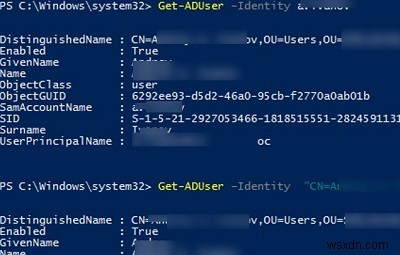
โดยค่าเริ่มต้น Get-ADUser คืนค่าแค่ 10 แอตทริบิวต์พื้นฐาน (จาก 120+ คุณสมบัติ) เช่น DistinguishedName, SamAccountName, Name, SID, UserPrincipalName, ObjectClass, สถานะบัญชี (Enabled: True/False) ไม่รวมข้อมูลเวลาเปลี่ยนรหัสผ่านล่าสุด
สอบถามบนโดเมนคอนโทรลเลอร์เฉพาะ ใช้ -Server:
Get-ADUser –Server DC01.woshub.com –Identity tstuser
ดึงข้อมูลจากโดเมนอื่น ต้องระบุโดเมนคอนโทรลเลอร์และข้อมูลประจำตัว:
$ADcred = Get-Credential
 Get-ADUSer tstuser -Server DC01.contoso.com -Credential $ADcred
แสดงแอตทริบิวต์ทั้งหมดของผู้ใช้:
Get-ADUser -identity tuser -properties *
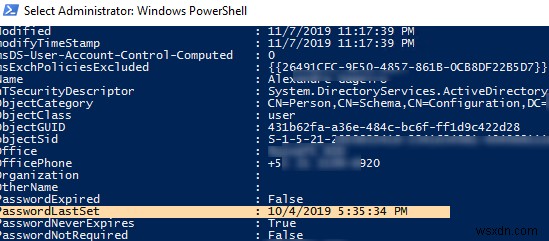
สวิตช์ Properties * แสดงแอตทริบิวต์ทั้งหมดรวมถึงค่าว่าง คล้ายกับแท็บ Attribute Editor ใน dsa.msc
จัดรูปแบบเอาต์พุตให้แสดงเฉพาะคุณสมบัติที่ต้องการ เช่น:
- PasswordExpired
- PasswordLastSet
- PasswordNeverExpires
- LastLogonTimestamp
รันคำสั่ง:
Get-ADUser tuser -properties PasswordExpired, PasswordLastSet, PasswordNeverExpires, lastlogontimestamp
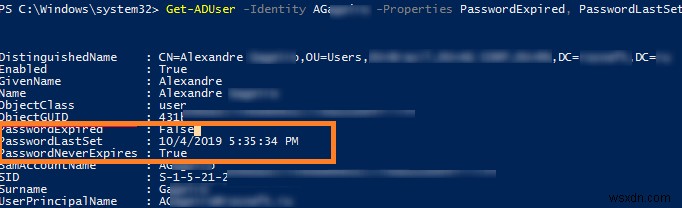
แสดงในรูปตารางสะดวกกว่า ใช้ Select-Object –Property และ Format-Table:
Get-ADUser -filter * -properties PasswordExpired, PasswordLastSet, PasswordNeverExpires | ft Name, PasswordExpired, PasswordLastSet, PasswordNeverExpires
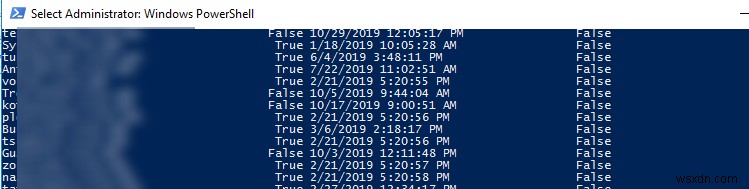
Get-ADUser -SearchBase: ดึงผู้ใช้จาก OU เฉพาะ
แสดงผู้ใช้จากคอนเทนเนอร์เฉพาะ (OU) ใช้พารามิเตอร์ –SearchBase:
Get-ADUser -SearchBase 'OU=London,DC=woshub,DC=loc' -filter * -properties PasswordExpired, PasswordLastSet, PasswordNeverExpires | ft Name, PasswordExpired, PasswordLastSet, PasswordNeverExpires
เลือกผู้ใช้จากหลาย OU พร้อมกัน:
$OUs = "OU=NY,DC=woshub,DC=com","OU=LA,DC=woshub,DC=com","OU=MA,DC=woshub,DC=com"
 $OUs | foreach {Get-ADUser -SearchBase $_ -Filter * |select Name, Enabled}
ดึงที่อยู่อีเมลผู้ใช้จาก AD ด้วย PowerShell
ที่อยู่อีเมลเป็นแอตทริบิวต์ของออบเจ็กต์ผู้ใช้ ต้องเพิ่มฟิลด์ EmailAddress ใน Properties:
Get-ADUser -filter * -properties EmailAddress -SearchBase 'OU=Paris,OU-Fr,DC=woshub,DC=com'| select-object Name, EmailAddress
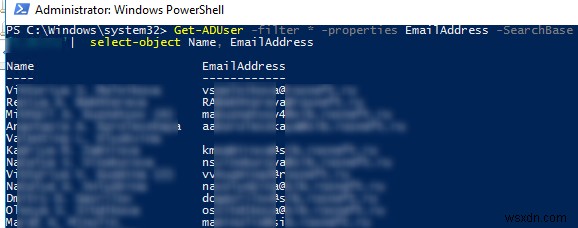
รายการบัญชีที่เปิดใช้งานพร้อมอีเมล:
Get-ADUser -Filter {(mail -ne "null") -and (Enabled -eq "true")} -Properties Surname,GivenName,mail | Select-Object Name,Surname,GivenName,mail | Format-Table
รายการผู้ใช้ที่ไม่มีอีเมล:
Get-ADUser -Filter * -Properties EmailAddress | where -Property EmailAddress -eq $null
ส่งออกรายการอีเมลบริษัทเป็น CSV เพื่อนำเข้า Outlook หรือ Thunderbird:
Get-ADUser -Filter {(mail -ne "null") -and (Enabled -eq "true")} -Properties Surname,GivenName,mail | Select-Object Name,Surname,GivenName,mail | Export-Csv -NoTypeInformation -Encoding utf8 -delimiter "," $env:temp\adress_list.csv
Get-ADUser: ส่งออกรายการผู้ใช้ AD เป็น CSV ด้วย PowerShell
ส่งออกเป็นไฟล์ข้อความ:
Get-ADUser -filter * -properties PasswordExpired, PasswordLastSet, PasswordNeverExpires | ft Name, PasswordExpired, PasswordLastSet, PasswordNeverExpires > C:\temp\users.txt
หรือส่งออกเป็น CSV:
Get-ADUser -filter * -properties PasswordExpired, PasswordLastSet, PasswordNeverExpires | where {$_.name –like "*Dmitry*"} | sort-object PasswordLastSet | select-object Name, PasswordExpired, PasswordLastSet, PasswordNeverExpires | Export-csv -path c:\tmp\user-passwords-expires.csv -Append -Encoding UTF8
ยังสามารถส่งออกตรงไปยังไฟล์ Excel ได้อีกด้วย
ตัวอย่างการใช้ Filter ใน Get-ADUser
ใช้สวิตช์ –Filter กรองบัญชีผู้ใช้ตามแอตทริบิวต์หนึ่งหรือหลายค่า เหมาะสำหรับค้นหาผู้ใช้ที่ตรงตามเกณฑ์ ระบุค่าแอตทริบิวต์เป็นอาร์กิวเมนต์ของพารามิเตอร์นี้
ตัวอย่าง: รายการบัญชีที่เปิดใช้งาน (Enabled) และชื่อมีคำว่า "Dmitry" ใช้เงื่อนไขหลายอย่างร่วมด้วย -and:
Get-AdUser -Filter "(Name -like '*Dmitry*') -and (Enabled -eq 'True')" -Properties * |select name,enabled
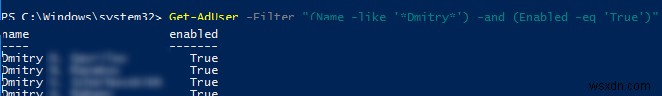
ใช้โอเปอเรเตอร์ตรรกะ PowerShell ได้ทั้งหมด (-eq, -ne, -gt, -ge, -lt, -le, -like, -notlike, -and, -or ฯลฯ)
จัดเรียงผลลัพธ์ด้วย Sort-Object หรือกรองเพิ่มเติมด้วย Where-Object:
Get-ADUser -filter * -properties PasswordExpired, PasswordLastSet, PasswordNeverExpires -SearchBase 'OU=NY,DC=woshub,DC=com'| where {$_.name –like "*Dmitry*" -and $_.Enabled -eq $true} | sort-object PasswordLastSet | select-object Name, PasswordExpired, PasswordLastSet, PasswordNeverExpires
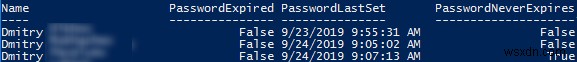
ค้นหาผู้ใช้ด้วยหลายแอตทริบิวต์พร้อมกัน (legacyExchangeDN, proxyAddresses, SAMAccountName ฯลฯ) ใช้คุณสมบัติ Ambiguous Name Resolution (ANR):
Get-ADUser -Filter {anr -eq 'John'} | select Name
เคล็ดลับ จากมุมมองประสิทธิภาพ การระบุเกณฑ์ด้วย Filter ดีกว่าการส่งต่อไปยัง Where-Object เพราะการกรองเกิดขึ้นบนโดเมนคอนโทรลเลอร์ ลดข้อมูลที่ส่งผ่านเครือข่าย
ใช้ LDAP filter ได้ด้วยพารามิเตอร์ –LdapFilter:
Get-ADUser -LDAPFilter '(&(department=it)(title=sysops))'
ตัวอย่าง PowerShell Get-ADUser เพิ่มเติม
คำสั่งที่มีประโยชน์สำหรับการสอบถามผู้ใช้ AD ด้วยตัวกรองต่างๆ สามารถรวมกันใช้ได้:
- ผู้ใช้ที่ชื่อขึ้นต้นด้วย "Joe":
Get-ADUser -filter {name -like "Joe*"} - นับจำนวนบัญชีผู้ใช้ทั้งหมด:
Get-ADUser -Filter {SamAccountName -like "*"} | Measure-Object - ค้นหาบัญชีที่ถูกปิดใช้งาน:
Get-ADUser -Filter {Enabled -eq "False"} | Select-Object SamAccountName,Name,Surname,GivenName | Format-Table - ตรวจสอบวันที่สร้างบัญชี:
get-aduser -Filter * -Properties Name, WhenCreated | Select name, whenCreated - ผู้ใช้ที่สร้างใหม่ใน 24 ชั่วโมงล่าสุด:
$lastday = ((Get-Date).AddDays(-1)); Get-ADUser -filter {(whencreated -ge $lastday)} - บัญชีที่รหัสผ่านหมดอายุ:
Get-ADUser -filter {Enabled -eq $True} -properties name,passwordExpired| where {$_.PasswordExpired}|select name,passwordexpired - สร้างกลุ่ม AD แบบไดนามิกตามเมือง ตำแหน่ง แผนก ร่วมกับ Add-ADGroupMember
- อ่านรายการบัญชีจากไฟล์ข้อความ ดึงชื่อบริษัทจาก AD บันทึกเป็น CSV:
Import-Csv c:\ps\users_list.csv | ForEach { Get-ADUser -identity $_.user -Properties Name, Company | Select Name, Company | Export-CSV c:\ps\users_ad_list.csv -Append -Encoding UTF8 } - ผู้ใช้ที่ไม่ได้เปลี่ยนรหัสผ่าน 90 วัน:
$90_Days = (Get-Date).adddays(-90); Get-ADUser -filter {(passwordlastset -le $90_days)} - บัญชีที่ไม่ได้เข้าสู่ระบบ 180 วัน (ใช้ lastLogonTimestamp):
$LastLogonDate= (Get-Date).AddDays(-180); Get-ADUser -Properties LastLogonTimeStamp -Filter {LastLogonTimeStamp -lt $LastLogonDate } | ?{$_.Enabled –eq $True} | Sort LastLogonTimeStamp| FT Name, @{N='lastlogontimestamp'; E={[DateTime]::FromFileTime($_.lastlogontimestamp)}} -AutoSize - ดึงรูปภาพผู้ใช้จาก AD บันทึกเป็น JPG:
$usr = Get-ADUser sjoe -Properties thumbnailPhoto; $usr.thumbnailPhoto | Set-Content sjoe.jpg -Encoding byte - รายการกลุ่ม AD ที่ผู้ใช้เป็นสมาชิก:
Get-AdUser sjoe -Properties memberof | Select memberof -expandproperty memberof - ผู้ใช้ใน OU ที่เป็นสมาชิกกลุ่มความปลอดภัยเฉพาะ:
Get-ADUser -SearchBase 'OU=Rome,OU=Italy,DC=woshub,DC=com' -Filter * -properties memberof | Where-Object {($_.memberof -like "*CEO*")} - ผู้ใช้ใน OU ยกเว้นสมาชิกกลุ่มเฉพาะ:
$Users = Get-ADUser -filter * -SearchBase ‘OU=Berlin,DC=woshub,DC=com’ -properties memberOf; ForEach ($User In $Users) { $Groups = -join @($User.memberOf); If ($Groups -notlike '*Domain Admins*') { $User.Name } } - ส่งออกรายการพร้อมชื่อ OU ไป Out-GridView:
get-aduser -filter * -Properties cn,canonicalname | select name,userprincipalname,@{Name="OU";expression={$_.Canonicalname.substring(0,$_.canonicalname.length-$_.cn.length)}}| Out-GridView - ตรวจสอบว่าบัญชีมีอยู่จริง:
$SamAccountName='jbrown'; if (@(Get-ADUser -Filter { SamAccountName -eq $SamAccountName }).Count -eq 0) { Write-Host "User $SamAccountName doesn’t exist" } - คอมพิวเตอร์ที่อนุญาตให้เข้าสู่ระบบ (LogonWorkstations):
Get-ADUser jbrown -Properties LogonWorkstations | Format-List Name, LogonWorkstations
เคล็ดลับ ใช้ Get-ADComputer สำหรับค้นหาข้อมูลคอมพิวเตอร์จาก AD
