

เคยอยากทิ้งค่าอินเทอร์เน็ตแพงและใช้ wifi เพื่อนบ้านที่ไม่ปลอดภ? สิ่งเดียวที่ขวางคือ Honeybadger single-factor auth flow? มีข่าวดีให้ฟัง
ประกาศ: Two Factor Authentication (2FA)
ขอเลิกเล่นจริงๆ เรานำความปลอดภมากจริง เราตื่นเต้นที่จะให้ tool สำคัญนี้ช่วยเก็บ users และข้อมูลของพวกเขาให้ปลอดภขึ้น
ผมคิดแค่อธิบายวิธี enable 2FA แต่น่าเบื่อ ไม่อยากรู้ว่ามันทำงานยังไง? มาดูกันโลก cryptography แบบ light-hearted ว่า 2FA ทำงานอย่างไร
ถ้า fun ไมใช่เรื่องคุณ ข้ามไป "How to enable" ได้ ผมไม่แคร์
⚠️ Warning: มีทฤษฎีด้านล่าง
หลาย 2FA implementations สร้างบน algorithm ชื่อ Time-Based One-Time Password (TOTP) พูดง่าย
One-Time?
ใช่ ความสวยงามคือคุณไม่ส่ง "password" เดียวกันทุกครั้งที่ login ใช้ authenticator application one-time "password" ถูก generate และ valid ระยะสั้น (ปกติ 30 วินาที) ซึ่ง dilute effectiveness ของ man-in-the-middle attack มาก
แม้มีบางส่วนซับซ้อน implementation โดยรวมค่อนข้าง simple
The Secret (ความลับ)
Key point เกี่ยวกับ TOTP คือ server (verifier) และ authenticator (prover) ต้องมี shared secret นี่คือ real "password" แต่ส่งแค่ครั้งเดียว (one-time ด้วย)!
วิธีแนะนำ consume secret คือ QR code ตอน scan QR code เข้า smartphone secret encoded ใน standard URI แบบนี้:
otpauth://totp/Honeybadger.io:inigo@honeybadger.io?secret=base32-secret-keyประโยชน์ของ QR code (เทียบ plaintext secret):
- ใครมีเวลาพิมพ์ code 32 ตัวอักษร?
- Authenticator app ให้ helpful labels สำหรับ one-time password (อ้างอิง email และ issuer ใน URI) มีประโยชน์ตอนใช้ 2FA หลาย services
- สุดท้ายมี good reason ใช้ QR code!
มี additional parameters สำหรับ otpauth scheme ที่ส่วนใหญ่ ignored ดูได้ที่นี่
MAC and Me
ตอน secrets agreed 🤝 คุณจะถูกขอ (บางจุด) ให้ One-Time Password นี่คือจุดที่จริงจัง
TOTP สร้างบน algorithm อีกตัว HMAC-Based One-Time Password (HOTP) ซึ่งสร้างบน Hash-based Message Authentication Code (HMAC) มันคือ crypto onion ใหญ่
TOTP & HOTP แตกต่างกันที่ message ไหนถูก hash HMAC คือที่ magic เกิด HMAC produces digest output ของการรัน value ผ่าน hashing algorithm มาดูกับ Ruby code:
OpenSSL::HMAC.digest("SHA1", "my-secret-key", "the-earth-is-flat")
=> "R\xABp\xCB\xEC\xFEJ\r#\x02\xC8\xAB\x96\xB68\v\xDA0\xD7z"
Wow ดู binary string นั้น! นั่นคือ Message Authentication Code (MAC)
เราเลือก SHA1 เป็น hashing function (เหมือน TOTP implementation ของเรา) มี functions อื่นมาก แต่ละตัวมี security และ performance implications อะไร radical ของ hashing algorithm คือ any input ให้ same output ทุกครั้ง! และผลลัพธ์ แตกต่างและ unique อย่างมาก จากการเปลี่ยน input เล็กน้อย (ขึ้นกับ hashing function แต่เราไม่ concerned with collisions)
มันเรียก Message Authentication Code เพราะใช้พิสูจน์ว่า received message เป็น authentic ถ้าคุณและผมรู้ secret (my-secret-key) ผมส่ง message the-earth-is-flat พร้อม MAC คุณแค่รัน digest function เดียวกัน input เดียวกัน ถ้า MACs match คุณ authenticated message! รู้ว่ามันไม่ถูก tamper และมาจากผมเท่านั้น!
😎
Timecode
กลับมาที่ TOTP เวลาพูดถึง time ใน TOTP แทน digest preposterous message อย่าง the-earth-is-flat เราใช้ time step count (แปลงเป็น string) เป็น input เปิด authenticator app ดูตอน codes เปลี่ยน จะสังเกต pattern ใช่ พูดไปด้วยกัน: "มันเปลี่ยนที่นาทีและครึ่งนาที" ดีมาก
ทำให้คำนวณ message ง่ายขึ้น ใช้ rounded down count ของ 30 วินาที (time step) นับจากต้นเวลา (unix time) ใน Ruby:
Time.now.to_i / 30 => 51772900Ah hah! นั่นคือ Message ของเรา
ใน Authenticator app ใช้ digest function ได้ HMAC ใหม่:
hmac = OpenSSL::HMAC.digest("SHA1", "avwe8aw71j2boib23jkbjk32", "51772900")
=> "H\x7F\xC1\xACL\xDA\xDB\xE7DQ\x91kE\x1C\xE3,c\nH\xA0"
get_otp_code(hmac) => "332204"
ขั้นสุดท้าย ดึง number code จาก binary string เนื่องจากต้อง bit manipulation ผมซ่อนใน anonymous get_otp_code function หากสนใจ อ่านใน HOTP Spec
ตอน submit code ไป server มันทำ digest operation เดียวกัน และ compare codes ตรงกัน = เข้าได้! เนื่องจากทำงานกับเวลา latency เป็น factor มี strategies account สำหรับ delays เป็น homework ถ้าอยากรู้
นั่นคือ gist ของ Time-Based One-Time Passwords!! 🎉 ส่ง email ขอบคุณผมได้ถ้าใช้ info นี้เป็น life of dinner party ถัดไป!
Implementation (การนำไปใช้)
ผมคิดสำคัญที่เข้าใจการทำงาน แตेढาว่าจะ roll-your-own anything crypto related หนึ่งในสิ่งดีของ Ruby/Rails ecosystem คือหา gem ได้บ่อย (บางครั้งหลาย gems) แก้ปัญหา
เราใช้ devise ที่ Honeybadger มี devise plugin ยอดเยี่ยมชื่อ two_factor_authentication มี 2FA implementations หลายตัว เหตุผลเราเลือกตัวนี้:
- Simple setup (migration, config & initializers)
- อนุญาต One-Time code ใส่หน้าแยก (หลัง user/password valid)
- Acceptable defaults, แต่งง่าย
- มี max login attempts check แนะนำโดย spec
วิธี Enable
Setup ง่าย: ไป User Settings > Authentication เลือก "Set Up Two Factor Authentication" ตาม directions sync secret ด้วย Authy หรือ Google Authenticator (หรือ TOTP app อื่นๆ)
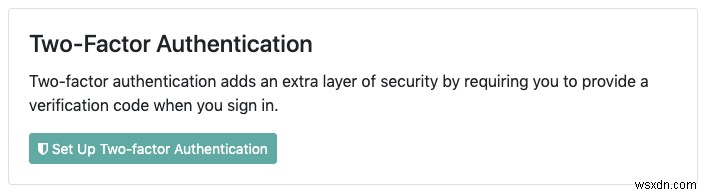
แค่นี้! ครั้งหน้า login เราจะขอ authenticator code ใส่แล้วไปด้วย peace of mind เต็มที่ 🧘
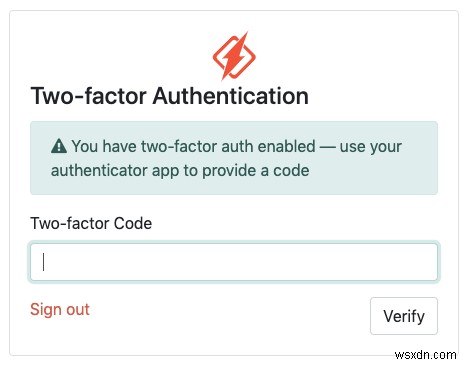
Security และ simplicity? ดีกว่านี้ได้ไหม?
อีกอย่างสุดท้าย: Pwned Password Check
มีอย่างรวดสำหรับผู้สนับสนุน weak passwords เรา integrate กับ devise-pwned_password gem ตั้งแต่ตอนนี้ เวลาทำ operation ที่ต้อง password เราเช็คว่า proposed password ไม prevalent ใน known data breaches ถ้าเพิ่ม password ใหม่ fail check เราไม่อนุญาต
ถ้ายังไม่ได้ใช้ เรา แนะนำอย่างยิ่ง ใช้ password manager (1Password ahem)
ส่วนน่าสนใจของ Pwned Password คือ password อยู่ปลอดภแม้ check กับ database จาก 3rd party service เรียกว่า k-Anonymity อ่าน overview ได้ที่นี่
นี่คือทั้งหมดตอนนี้ Until next time! 👋
