

บทนำ
Blog ครอบคลุม Essentials ของการใช้ Advanced Security Option เพื่อ Secure Sensitive Data ภายใน Oracle® Database ด้วย Transparent Data Encryption (TDE) Feature นี้ Enable การ Encrypt Database Columns และ Manage Encryption Keys
Introduction
TDE Enable การ Encrypt Sensitive Database Data ที่ Stored ใน OS Files ให้ Secure Storage และ Management ของ Encryption Keys ใน Security Module นอก Database
Encrypted Data ถูก Transparently Decrypted สำหรับ Database User ที่มี Access ไป Data TDE Store Encryption Keys ใน Security Module External to Database
Why Use TDE?
ถ้าโจรขโมย Backup Tapes ของ Database และ Restore บน Server ของตัวเอง พวกเขาจะ Access Most Sensitive Data ของ Company นี่คือ Unacceptable Risk รูปแบบ Regulations และ Guidelines ของ Company ส่วนใหญ่ Consider Protecting Database Data เป็น Compliance Requirement คุณจะ Protect Database จาก Vulnerability นี้อย่างไร?
Solution หนึ่งคือ Encrypt Sensitive Data ใน Database และ Store Encryption Keys ใน Separate Location โดยไม่มี Keys ข้อมูลที่ถูกขโมยจะ Worthless
TDE ทำงานอย่างไร
TDE เป็น Key-based Access Control System แม้ Encrypted Data ถูก Retrieve ก็ Useless โดยไม่มี Authorized Decryption ซึ่งเกิดขึ้น Auto สำหรับ Users ที่ Authorized Access Table
สำหรับ Tables ที่มี Encrypted Columns Encryption Key เรียกว่า Column Encryption Key แต่ละ Table's Column Encryption Key ถูก Encrypt ด้วย Database Server's Master Key Master Encryption Key Stored Outside Database ใน Oracle Wallet
Encrypted Table Keys วางใน Data Dictionary เมื่อ User Enter Data เข้า Column ที่ Defined เป็น Encrypted Oracle ทำ:
- Retrieve Master Key จาก Wallet
- Decrypt Encryption Key สำหรับ Table นั้นจาก Data Dictionary
- Use Encryption Key นั้นบน Input Value
- Store Encrypted Data ใน Database
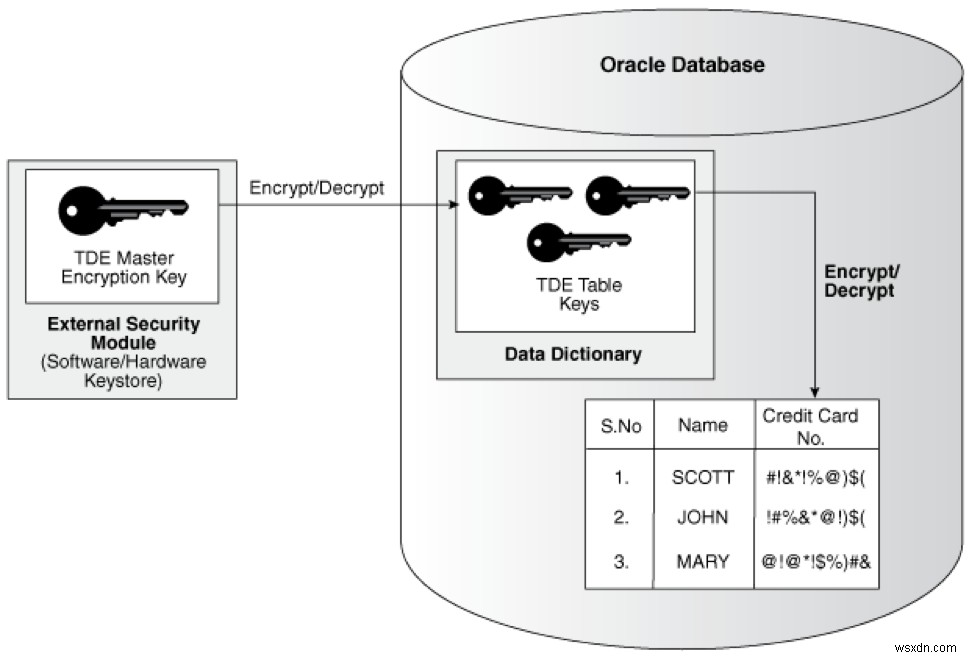
Image source: https://docs.oracle.com/database/121/ASOAG/img/GUID-5FD3A3BB-441C-4C42-A520-1248974627B0-default.png
TDE Encrypt Data ใน Database Files ต่อไปนี้:
- The Datafile
- The Redo Log และ Archive Log Files
- Memory
- The File Backup
Managing Oracle Wallet
Section อธิบาย Create, Open, และ Close Wallet
Create the Wallet
ตอน Enable TDE ครั้งแรก ต้อง Create Wallet ที่ Master Key Stored
Default Wallet Created ใน $ORACLE_BASE/admin/$ORACLE_SID/wallet แต่ Set Different Location ได้ โดย Specify ใน sqlnet.ora:
ENCRYPTION_WALLET_LOCATION = (SOURCE = (METHOD = FILE) (METHOD_DATA = (DIRECTORY =D:\oracle\product\Wallet)))Run Command Create Wallet:
ALTER SYSTEM SET ENCRYPTION KEY [certificate_ID] IDENTIFIED BY password;
- Password Case Sensitive Enclose ใน Double Quotes (" ")
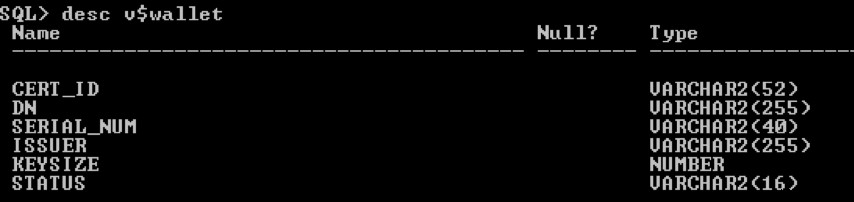
- certificate_ID Optional String มี Unique Identifier ของ Certificate ใน Oracle Wallet Search ได้โดย Query V$WALLET Fixed View เมื่อ Wallet Open
Open และ Close the Wallet
หลัง Create Wallet และ Set Password ต้อง Open Wallet Explicitly ด้วย SYS, SYSTEM, หรือ SYSDBA Accounts ทุกครั้งที่ Start Database
Example Run Command:
alter system set encryption wallet open identified by "oracle12345";Important: เพื่อ Perform Any Action บน Database ต้อง Open Wallet
Example Database Operation ที่ Database Up แต่ Wallet Closed:
alter system set encryption wallet close;
ตอนนี้ถ้า Retrieve Data จาก Encrypted Column Error Message แสดง เพราะ Wallet Closed
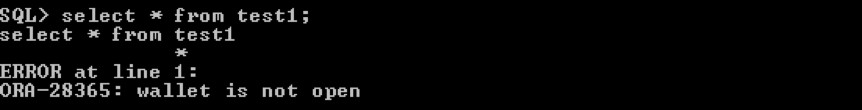
เพื่อ Retrieve Data จาก Encrypted Column ต้อง Open Wallet:
alter system set encryption wallet open identified by "oracle12345";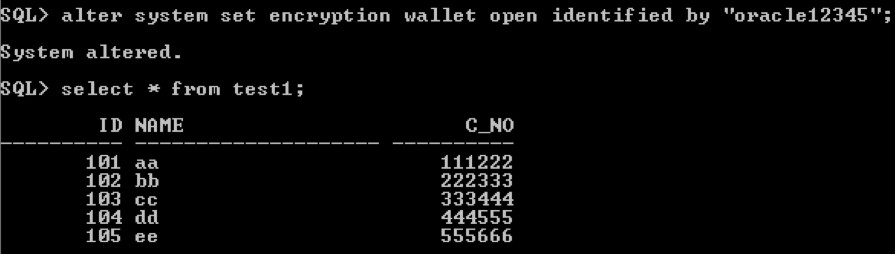
ตอนนี้ Retrieve Data จาก Encrypted Columns ได้แล้ว เพราะ Wallet Open
Create Tables with an Encrypted Column
Command สร้าง Table พร้อม Encrypted Column:
CREATE TABLE test2 (id number, name varchar2(20), s_s_num number ENCRYPT);
Create Tables ใช้ Non-default Algorithm และ NO SALT Option
SALT คือ Random String เพิ่มใน Data ก่อน Encrypt ทำให้ Secure และ Harder to Hack Default TDE Add SALT ใน Cleartext ก่อน Encrypt
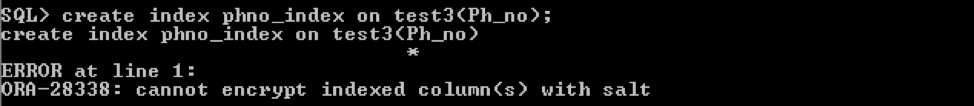
ไม่สามารถ Create Index บน Column ที่ Encrypted ด้วย SALT Option ถ้าต้องการ Add Index บน Encrypted Column ต้องใช้ NO SALT Option:
CREATE TABLE test3 (id number, name varchar2(20), s_s_num number ENCRYPT NO SALT, Ph_no number ENCRYPT USING '3DES168');
ที่นี่ S_S_NUM Column Encrypted ด้วย NO SALT Option และ PH_NO Column สร้างด้วย Default SALT Option
Example แสดงว่าไม่สามารถ Create Index บน PH_NO Column ได้ เพราะสร้างด้วย SALT Option โดย Default
Encrypt Columns ใน Existing Tables
Command Encrypt Column ใน Existing Table:
ALTER TABLE test1 ADD (ssn VARCHAR2(11) ENCRYPT);
Disable Encryption บน Column
Command Disable Encryption บน Column:
ALTER TABLE test1 MODIFY (ssn DECRYPT);
Restrictions on Using TDE
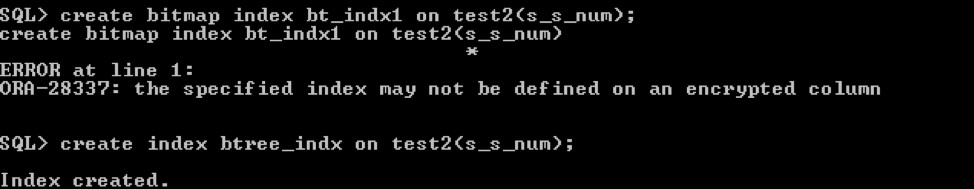
- Cannot Create Index อื่นนอกจาก B-tree บน Encrypted Column
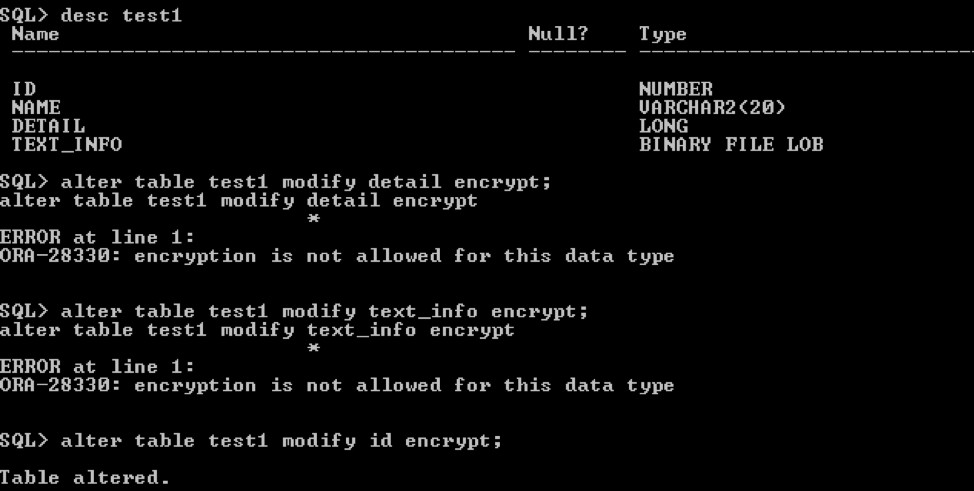
- Encryption Not Allowed บน External Large Objects (BFILE)
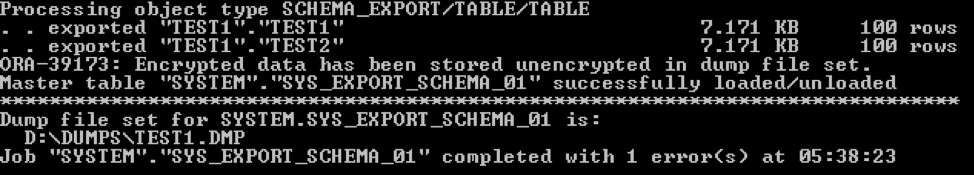
- Cannot Perform Import/Export Operations ถ้า Wallet Closed
Error เพราะ Wallet Closed

Success เพราะ Wallet Open
สรุป
ถ้าต้องการ Secure Sensitive Data จาก Unauthorized หรือ Back-door Access ใช้ TDE Security Option Feature นี้ให้ Data Encryption และ Compliance ทันทีโดยไม่มี Coding และ Key Management Complexity ช่วยให้ Focus บน Strategic Efforts มากขึ้น
ใช้แท็บ Feedback เพื่อแสดงความคิดเห็นหรือถามคำถาม
เพิ่มประสิทธิภาพสภาพแวดล้อมด้วยบริการผู้เชี่ยวชาญ
ผู้เชี่ยวชาญ Rackspace Application Services (RAS) ให้บริการ Professional และ Managed Services ครอบคลุม Portfolio หลากหลาย:
- Platform สำหรับ eCommerce และ Digital Experience
- Enterprise Resource Planning (ERP)
- Business Intelligence
- Salesforce Customer Relationship Management (CRM)
- Databases
- Email Hosting และ Productivity
เรามอบ:
- Unbiased Expertise: ลดความซับซ้อนและนำทางการ Modernization เน้นความสามารถที่สร้างคุณค่าทันที
- Fanatical Experience™: รวมแนวทาง Process First. Technology Second.® พร้อม Technical Support ให้ Soluation ครบวงจร
- Unrivaled Portfolio: ประยุกต์ประสบการณ์ Cloud มากมายช่วยเลือกและ Deploy เทคโนโลยีที่เหมาะสมบน Cloud ที่เหมาะสม
- Agile Delivery: ตรงจุดที่คุณอยู่ในการเดินทางและทำให้ความสำเร็จของเราสอดคล้องกับคุณ
แชทตอนนี้เพื่อเริ่มต้น
