

บริการ Linux หลายตัว (apache, nginx, ฯลฯ) สามารถใช้ไฟล์ keytab สำหรับ Kerberos Authentication ใน Active Directory โดยไม่ต้องใส่ Password Keytab File เก็บชื่อ Kerberos Principals และ Encrypted Keys ที่สอดคล้องกัน (ได้มาจาก Kerberos Passwords) ในบทความนี้เราจะแสดงวิธีสร้าง Keytab File สำหรับ SPN ของ Linked Active Directory Account โดยใช้ Tool ktpass
บ่อยที่สุด จะสร้าง Active Directory User Account แยกต่างหากสำหรับ Service ที่ต้องการใช้ Keytab File อย่างไรก็ตาม คุณยังสามารถใช้ Computer Object เพื่อทำได้ จากนั้น Service Name จะถูก Bind ไปยัง Account (ServicePrincipalName — SPN) SPN ถูกใช้โดย Kerberos Authentication เพื่อ Map Service Instance ไปยัง AD Account (นี่คือเหตุผลที่ Apps อาจ Authenticate ในฐานะ Services แม้จะไม่รู้ Username)
ขั้นแรก สร้าง Service Account ใน AD และตั้งค่า Known Password ให้ คุณสามารถสร้าง Account จาก Graphic ADUC Console (dsa.msc) หรือใช้ New-ADUser Cmdlet ใน PowerShell (จาก PowerShell Active Directory Module):
New-ADUser -Name "web" -GivenName "nginx web app" -SamAccountName "web" -UserPrincipalName "web@test.com" -Path "OU=Services,OU=Munich,OU=DE,DC=test,DC=com" –AccountPassword (ConvertTo-SecureString “Sup6r!Pa$s” -AsPlainText -force) -Enabled $true
Enable ตัวเลือก "User cannot change password" และ "Password never expires" สำหรับ Service Account ใน Graphic Console หรือใน PowerShell:
Get-ADUser web|Set-ADUser -PasswordNeverExpires:$True -CannotChangePassword:$true
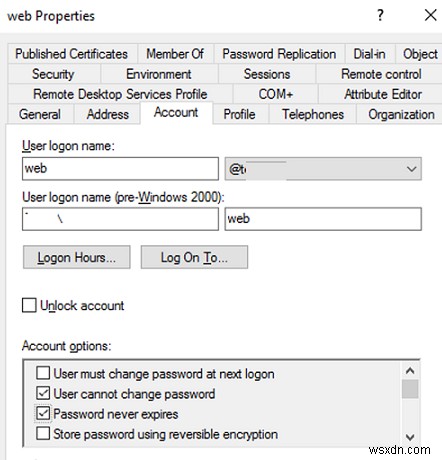
ขั้นตอนต่อไป Bind Service Principal Name (SPN) ไปยัง User Account คุณไม่จำเป็นต้องทำ Step นี้แยกต่างหาก เนื่องจาก ktpass ทำมันอัตโนมัติเมื่อสร้าง Keytab File (ผมทำเพื่อให้คุณเข้าใจกระบวนการดีขึ้น)
Bind SPN Record ต่อไปนี้ไปยัง Account web:
setspn -A HTTP/www.test.com@test.com web
แสดงรายการ SPN Records ที่เกี่ยวข้องกับ AD User:
setspn -L web
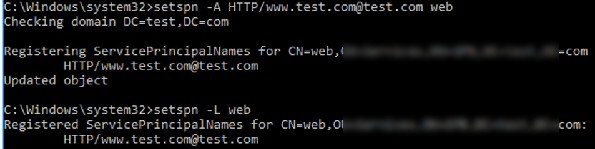
เพื่อสร้าง Keytab File ใช้คำสั่งต่อไปนี้:
ktpass -princ HTTP/www.test.com@TEST.COM -mapuser web -crypto ALL -ptype KRB5_NT_PRINCIPAL -pass Sup6r!Pa$s -target mundc01.test.com -out c:\share\web.keytab
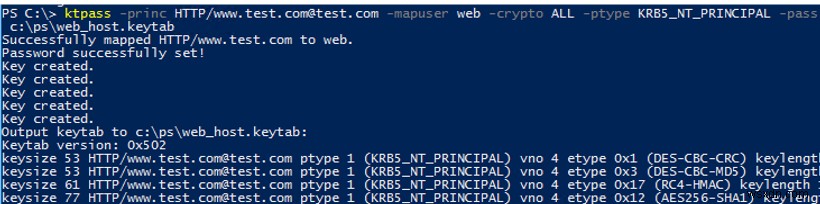
Successfully mapped HTTP/www.test.com to web. Password successfully set! Key created. Output keytab to c:\share\webt.keytab: Keytab version: 0x502 keysize 53 HTTP/www.test.com@test.com ptype 1 (KRB5_NT_PRINCIPAL) vno 4 etype 0x1 (DES-CBC-CRC) keylength 8 (0x73f868856e046449)
คำสั่งได้สร้าง Keytab File (c:\share\webt.keytab) สำหรับ SPN Record ของ Service HTTP/www@test.com SPN Record ผูกกับ Web Account ด้วย Password ที่ระบุ
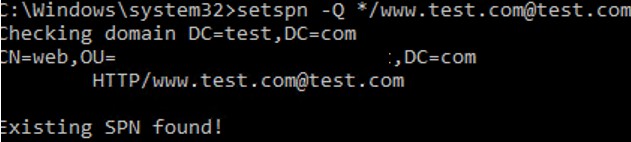
ตรวจสอบว่า SPN Record สำหรับ Service ถูกสร้างสำเร็จแล้ว (หากคุณไม่ได้สร้างด้วยตนเอง):
setspn -Q */www.test.com@test.com
คุณเห็นว่า SPN Record ถูกพบ (Existing SPN found!) มัน Bind กับ Web Account
Windows ไม่มี Built-in Tools เพื่อดู Contents ของ Keytab File แต่หาก Java JRE ติดตั้งบน Computer ของคุณ คุณสามารถใช้ klist.exe ที่รวมอยู่ใน Java Distribution Package
cd "c:\Program Files\Java\jre1.8.0_181\bin"
 klist.exe -K -e -t -k c:\PS\web_host.keytab
Key tab: c:\PS\web_host.keytab, 5 entries found.
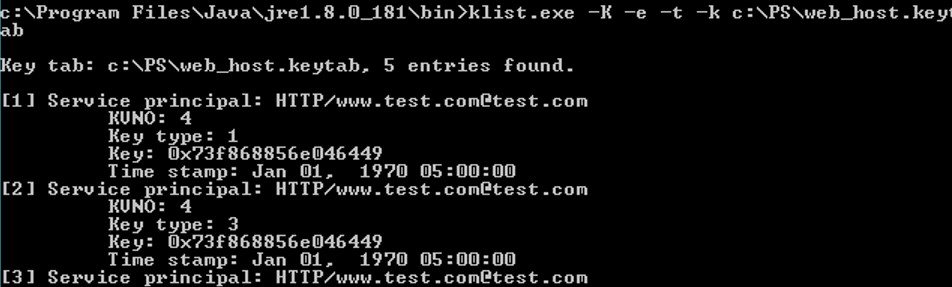
มาดู Contents ของ Keytab File SPNs, Keys, Timestamps, Encryption Algorithm และ Key Version (KVNO — Key Version Number) ถูกระบุที่นี่
เมื่อสร้าง Keytab File ktpass เพิ่มค่า Attribute msDS-KeyVersionNumber ของ User Account (คุณเห็นได้ใน AD Attribute Editor) และใช้ค่าเป็น KVNO ใน Keytab Table
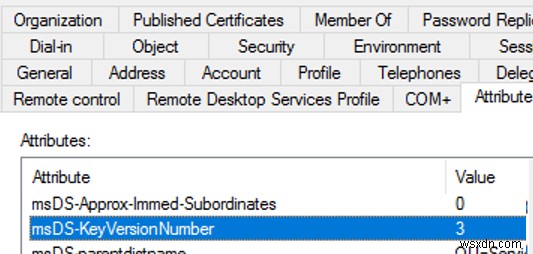
หากคุณเปลี่ยน Account Password Attribute Value จะเพิ่มขึ้น 1 และ Keytab Entries ทั้งหมดด้วย KVNO ก่อนหน้าจะกลายเป็น Invalid (แม้ New Password จะ Match กับ Old Password ทุกประการ) หาก User Password ใน AD เปลี่ยน คุณจะต้อง Generate Keytab File ใหม่อีกครั้ง
Keytab File อาจเก็บ Keys ของ SPNs ที่ต่างกัน Additional SPNs และ Keys ถูกเพิ่มเข้าไปใน Keytab File โดยใช้ Parameters ของ ktpass (-in,-setupn,-setpass)
การใช้งาน Keytab File ที่คุณได้ต่อไป ขึ้นอยู่กับ Service ที่มันถูกนำไปใช้ ตัวอย่างเช่น ที่นี่คุณสามารถเรียนรู้วิธีใช้ Keytab File สำหรับ Transparent SSO User Authentication ใน Zabbix นอกจากนี้ อย่าลืมเก็บ Keytab Files ให้ปลอดภัย (ใครก็ตามที่อ่าน Contents ของ Keytab File ได้ จะสามารถใช้ Keys ใดๆ จากมันได้)
