

ในบทความนี้เราจะแสดงวิธีแก้ไข Trust Relationship ที่เสียหายระหว่าง Workstation และ Active Directory Domain เมื่อ User ไม่สามารถ Logon เข้าสู่ Domain Computer ของพวกเขาได้ มาพิจารณา Root Cause ของปัญหาและวิธีง่ายๆ ในการซ่อมแซม Trust ระหว่าง Computer และ Domain Controller ผ่าน Secure Channel โดยไม่ต้อง Reboot Computer และ Rejoin Domain
The Trust Relationship Between This Workstation and the Primary Domain Failed
ปัญหาแสดงออกเมื่อ User พยายาม Logon เข้าสู่ Workstation หรือ Member Server โดยใช้ Domain Credentials และ Error ต่อไปนี้เกิดขึ้นหลังจากใส่ Password:
The trust relationship between this workstation and the primary domain failed.
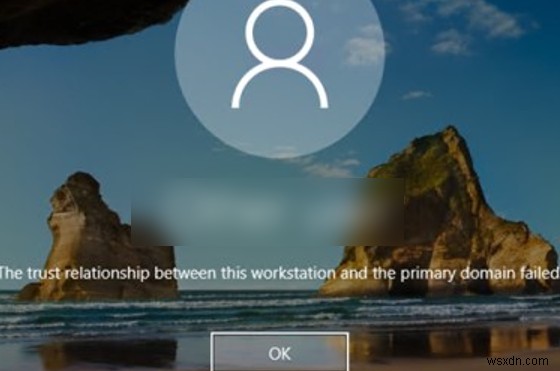
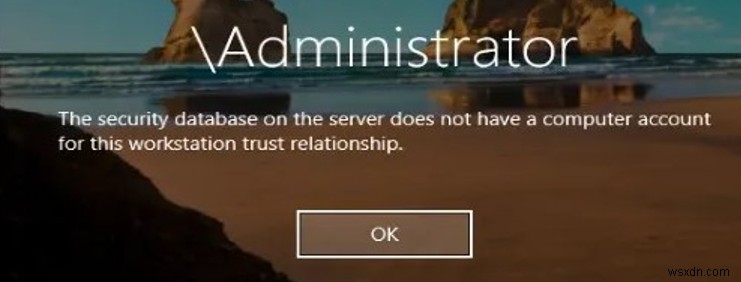
Error อาจมีลักษณะดังนี้:
The security database on the server does not have a computer account for this workstation trust relationship.
Machine (Computer) Account Password ใน Active Directory Domain
เมื่อ Computer Join เข้าสู่ Active Directory Domain บัญชี Computer แยกต่างหากจะถูกสร้างขึ้นสำหรับมัน คล้ายกับ Users แต่ละ Computer มี Password ของตัวเองเพื่อ Authenticate Computer ใน Domain และสร้าง Trusted Connection กับ Domain Controller อย่างไรก็ตาม ไม่เหมือน User Passwords Computer Passwords ถูกตั้งค่าและเปลี่ยนอัตโนมัติ
นี่คือสิ่งสำคัญบางอย่างเกี่ยวกับ Computer Account Passwords ใน AD:
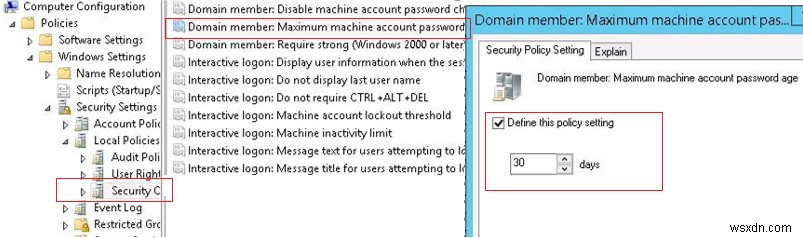
- Computer Passwords ใน AD ต้องเปลี่ยนเป็นประจำ (ทุก 30 วันโดย Default) Tip คุณสามารถตั้งค่า Maximum Computer Password Age โดยใช้ Policy Domain member: Maximum machine account password age ที่ตั้งอยู่ภายใต้ Computer Configuration-> Windows Settings-> Security Settings-> Local Policies-> Security Options Computer Password Lifetime อาจอยู่ระหว่าง 0 ถึง 999 วัน (30 วันโดย Default)
- ไม่เหมือน User Passwords Computer Password ไม่สามารถ Expire ได้ การเปลี่ยน Password เริ่มต้นโดย Computer ไใช่ Domain Controller Computer Password ไม่ได้อยู่ภายใต้นโยบาย Domain Password Policy แม้ Computer จะถูกปิดไว้ 30 วันหรือมากกว่า คุณสามารถเปิดมันได้ และมันจะ Authenticate บน DC ของคุณด้วย Password เก่า จากนั้น Local Netlogon Service จะเปลี่ยน Computer Password ใน Local Database ของมัน (Password จัดเก็บใน Registry
HKLM\SECURITY\Policy\Secrets\$machine.ACC) และจากนั้นจะ Update Computer Account Password ใน Active Directory - Computer Password เปลี่ยนบน Nearest DC การเปลี่ยนแปลงไม่ถูกส่งไปยัง Domain Controller ที่มี PDC Emulator FSMO Role (คือ หาก Computer เปลี่ยน Password บน DC หนึ่ง มันจะไม่สามารถ Authenticate บน DC อีกตัวได้จนกว่าการ Replicate AD Changes จะเสร็จ)
หาก Hash ของ Password ที่ Computer ส่งไปยัง Domain Controller ไม่ Match กับ Computer Account Password ใน AD Database Computer จะไม่สามารถสร้าง Secure Connection กับ DC และคืนค่า Trusted Connection Errors
ทำไมปัญหาจึงเกิดขึ้น:
- Computer ถูก Restore จาก Restore Point เก่าหรือ Snapshot (ในกรณีของ Virtual Machine) ที่สร้างก่อนที่ Computer Password จะถูกเปลี่ยนใน AD หากคุณ Roll Back Computer ไปสู่ Previous State มันจะพยายาม Authenticate บน DC โดยใช้ Old Password นี่คือ Issue ที่พบบ่อยที่สุด;
- Computer ที่มีชื่อเดียวกันถูกสร้างใน AD หรือใครสบางคน Reset Computer Account ใน Domain โดยใช้ ADUC Console (
dsa.msc);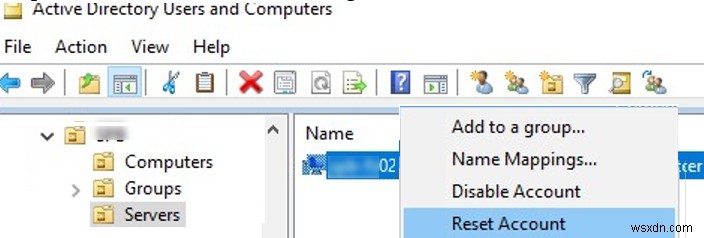
- Computer Account ใน Domain ถูก Disable โดย Administrator (ตัวอย่างเช่น ระหว่างขั้นตอนปกติของการ Disable Inactive AD Objects);
- กรณีที่พบน้อย ที่ System Time บน Computer ผิด
นี่คือ Classical Way ในการซ่อมแซม Trust Relationship ระหว่าง Computer และ Domain:
- Reset Computer Account ใน AD;
- ย้าย Computer จาก Domain ไป Workgroup ภายใต้ Local Administrator;
- Reboot;
- Rejoin Computer เข้าสู่ Domain;
- Restart Computer อีกครั้ง
วิธีนี้ดูง่าย แต่ clumsy มาก ต้อง Restart Computer อย่างน้อย 2 ครั้ง และใช้เวลา 10-30 นาที อาจเจอปัญหากับการใช้ Old Local User Profiles
มีวิธีที่ฉลาดกว่าในการซ่อมแซม Trust Relationship โดยใช้ PowerShell โดยไม่ต้อง Rejoin Domain หรือ Restart Computer
ตรวจสอบและกู้คืน Trust Relationship ระหว่าง Computer และ Domain โดยใช้ PowerShell
หากคุณไม่สามารถ Authenticate บน Computer ภายใต้ Domain Account และ Error ต่อไปนี้ปรากฏ: The trust relationship between this workstation and the primary domain failed คุณต้อง Logon เข้าสู่ Computer โดยใช้ Local Administrator Account คุณยังสามารถ Unplug Network Cable และ Authenticate บน Computer ด้วย Domain Account ที่ Login เข้าคอมพิวเตอร์เมื่อเร็วๆ นี้โดยใช้ Cached Credentials
เปิด Elevated PowerShell Console และใช้ Cmdlet Test-ComputerSecureChannel เพื่อตรวจสอบว่า Local Computer Password Match กับ Password ที่จัดเก็บใน AD หรือไม่
Test-ComputerSecureChannel –verbose

หาก Passwords ไม่ Match และ Computer ไม่สามารถสร้าง Trust Relationship กับ Domain คำสั่งจะคืนค่า False – The Secure channel between the local computer and the domain woshub.com is broken
เพื่อ Force Reset Computer Account Password ใน AD ให้รันคำสั่งนี้:
Test-ComputerSecureChannel –Repair –Credential (Get-Credential)
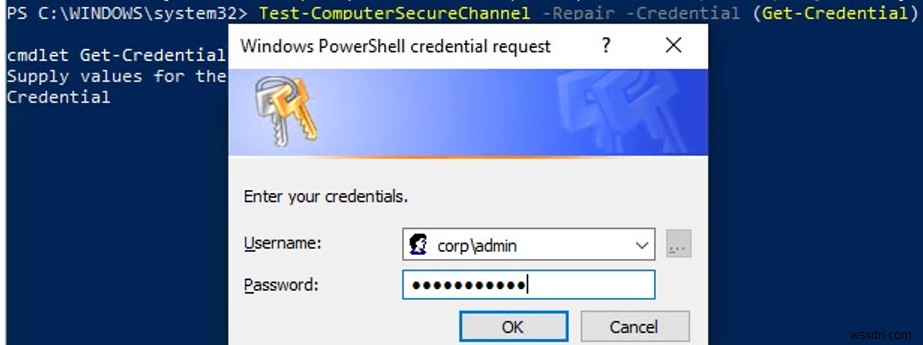
เพื่อ Reset Password ให้ใส่ Credentials ของ User Account ที่มีสิทธิ์ Reset Computer Account Password User ต้องถูก Delegate Permissions จัดการ Computers ใน Active Directory (คุณอาจใช้ Domain Admins Group Member ได้เช่นกัน)
จากนั้นรัน Test-ComputerSecureChannel อีกครั้งเพื่อให้แน่ใจว่าคืนค่า True (The Secure channel between the local computer and the domain woshub.com is in good condition)
ดังนั้น Computer Password ถูก Reset แล้วโดยไม่ต้อง Restart หรือ Manual Domain Rejoin ตอนนี้คุณสามารถ Logon เข้าสู่ Computer โดยใช้ Domain Account ของคุณได้
นอกจากนี้ เพื่อ Force Reset Password คุณอาจใช้ Cmdlet Reset-ComputerMachinePassword
Reset-ComputerMachinePassword -Server mun-dc01.woshub.com -Credential woshub\adm_user1
mun-dc01.woshub.com คือชื่อ DC ที่ใกล้ที่สุดสำหรับเปลี่ยน Computer Password
ควร Reset Computer Password ทุกครั้งก่อนสร้าง Virtual Machine Snapshot หรือ Computer Restore Point จะทำให้ Roll Back ไปสู่ Previous Computer State ง่ายขึ้น
หากคุณมี Development หรือ Test Environment ที่คุณต้อง Recover Previous VM State จาก Snapshot บ่อยครั้ง คุณอาจต้องการ Disable Password Change ใน Domain สำหรับ Computers เหล่านี้โดยใช้ GPO ในการทำเช่นนั้น ให้ตั้งค่า Policy Domain member: Disable machine account password changes ที่ตั้งอยู่ใน Computer Configuration -> Policies -> Windows Settings -> Security Settings -> Local Policies -> Security Options คุณสามารถ Target Policy ไปยัง OU ที่มี Test Computers หรือใช้ GPO WMI Filters
โดยใช้ Cmdlet Get-ADComputer (จาก Active Directory Module สำหรับ Windows PowerShell) คุณสามารถตรวจสอบวันที่เปลี่ยน Computer Password ล่าสุดใน AD ได้:
Get-ADComputer –Identity mun-wks5431 -Properties PasswordLastSet
Cmdlets Test-ComputerSecureChannel และ Reset-ComputerMachinePassword พร้อมใช้งานตั้งแต่ PowerShell Version 3.0 คุณจะต้อง Update PowerShell Version ใน Windows 7/Windows Server 2008 R2
คุณยังสามารถตรวจสอบว่ามี Secure Channel ระหว่าง Computer และ DC หรือไม่โดยใช้คำสั่งนี้:
nltest /sc_verify:woshub.com
บรรทัดต่อไปนี้ยืนยันว่า Trust ถูกซ่อมแซมสำเร็จแล้ว:
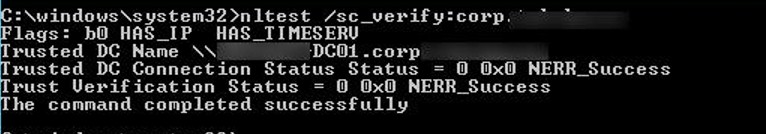
Trusted DC Connection Status = 0 0x0 NERR_Success Trust Verification Status = 0 0x0 NERR_Success
ซ่อมแซม Domain Trust โดยใช้ Netdom
ใน Windows 7/2008R2 และ Windows Versions ก่อนหน้าที่ไม่มี PowerShell 3.0 คุณไม่สามารถใช้ Test-ComputerSecureChannel และ Reset-ComputerMachinePassword Cmdlets เพื่อ Reset Computer Password และซ่อมแซม Trust Relationship กับ Domain ได้ ในกรณีนี้ ให้ใช้ Tools netdom.exe เพื่อกู้คืน Secure Channel กับ Domain Controller
Netdom รวมอยู่ใน Windows Server 2008 หรือใหม่กว่า และสามารถติดตั้งบน Users Computers จาก RSAT (Remote Server Administration Tools) เพื่อซ่อมแซม Trust Relationship ให้ Login ภายใต้ Local Administrator Credentials (โดยพิมพ์ .\Administrator บน Logon Screen) และรันคำสั่งต่อไปนี้:
Netdom resetpwd /Server:DomainController /UserD:Administrator /PasswordD:Password
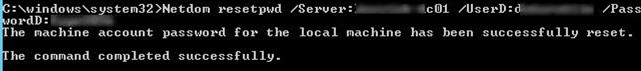
The machine account password for the local machine has successfully reset.
- Server คือชื่อ Domain Controller ใดๆ ที่พร้อมใช้งาน
- UserD คือชื่อ User ที่มี Domain Administrator Permissions หรือมี Delegated Privileges บน OU ที่มี Computer Account
- PasswordD User Password
Netdom resetpwd /Server:mun-dc01 /UserD:jsmith /PasswordD:Pra$$w0rd
หลังจากรันคำสั่ง คุณไม่ต้อง Reboot Computer: เพียง Log Off และ Log On อีกครั้งโดยใช้ Domain Account ของคุณ
ตามที่คุณเห็น การซ่อมแซม Trust ระหว่าง Computer และ Domain ทำได้ค่อนข้างง่าย
