

เมื่อ Domain User Log On เข้า Windows Credentials ของพวกเขาจะถูกบันทึกบน Local Computer โดยค่าเริ่มต้น (Cached Credentials: User Name และ Password Hash) สิ่งนี้ช่วยให้ User สามารถ Logon เข้าคอมพิวเตอร์ได้แม้ AD Domain Controllers จะไม่พร้อมใช้งาน Powered Off หรือ Network Cable ถูกถอดออกจากคอมพิวเตอร์ Domain Account Credentials Caching สะดวกสำหรับ Laptop Users ที่สามารถเข้าถึง Local Data บน Device ได้เมื่อ Corporate Network ไม่พร้อมใช้งาน
การ Cache Domain User Credentials บน Windows
Cached Credentials อาจถูกใช้เพื่อ Logon เข้า Windows หาก User เคย Authenticate บนคอมพิวเตอร์นี้อย่างน้อย 1 ครั้ง และ Domain Password ของพวกเขายังไม่ถูกเปลี่ยนแปลงตั้งแต่นั้นมา User Password ใน Cached Credentials ไม่มีวันหมดอายุ หาก Domain Password Policy บังคับให้ User เปลี่ยน Password Saved Password ใน Local Cache จะไม่เปลี่ยนจนกว่าจะ Log On ด้วย Password ใหม่ หาก User Password ใน AD ถูกเปลี่ยนหลัง Log On ครั้งล่าสุดไปยังคอมพิวเตอร์ และคอมพิวเตอร์อยู่ Offline (ไม่มีการเข้าถึง Domain Network) User จะสามารถ Login Computer ด้วย Old Password ได้
หาก Active Directory Domain ไม่พร้อมใช้งาน Windows จะตรวจสอบว่า Username และ Password ที่ป้อนตรงกับ Local Cache หรือไม่ และอนุญาต Local Logon เข้าคอมพิวเตอร์
Cached Credentials จัดเก็บใน Registry Under Reg Key HKEY_LOCAL_MACHINE\Security\Cache (%systemroot%\System32\config\SECURITY) Saved Hash แต่ละตัวจัดเก็บใน Parameter NL$x (ที่ x คือ Cached Data Index) โดยค่าเริ่มต้น แม้ Administrator ก็ไม่สามารถดู Contents ของ Registry Key นี้ได้ แต่คุณสามารถเข้าถึงได้หากจำเป็น
Password Hash ถูกปรับเปลี่ยนด้วย salt berdasarkan User Name และบันทึกลง Registry
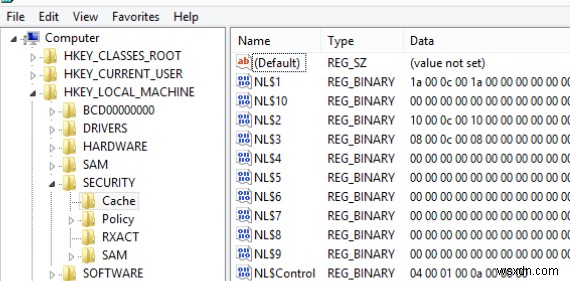
หากคุณ Clear ค่า NL$x Cached User Credentials จะถูกลบ
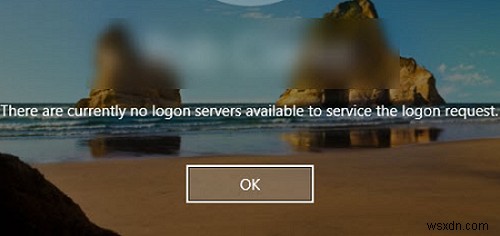
หากไม่มี Cached Credentials ใน Local Cache คุณจะเห็นข้อความต่อไปนี้เมื่อพยายาม Log On เข้า Offline Computer:
There are currently no logon servers available to service the logon request.
การกำหนดค่า Cached Credentials ด้วย Group Policy
คุณสามารถตั้งค่าจำนวน Unique Users ที่ Credentials อาจถูกบันทึกใน Local Cache บน Domain Computers ด้วย GPO Option สำหรับ User Credentials ที่จะจัดเก็บใน Local Cache User ต้อง Log On เข้าคอมพิวเตอร์อย่างน้อย 1 ครั้ง
โดยค่าเริ่มต้น Windows 10 และ Windows Server 2016 จัดเก็บ Credentials ของ 10 Recently Logged Users ล่าสุด คุณสามารถเปลี่ยนค่านี้ด้วย GPO Option ต่อไปนี้ – Interactive logon: Number of previous logons to cache (in case domain controller is not available) คุณสามารถหาได้ใน Computer Configuration -> Policies -> Windows Settings -> Security Settings -> Local Policies -> Security Options คุณสามารถตั้งค่าได้ตั้งแต่ 0 ถึง 50
หากตั้งค่า 0 จะป้องกันไม่ให้ Windows Cache User Credentials ในกรณีนี้ เมื่อ Domain ไม่พร้อมใช้งานและ User พยายาม Log On พวกเขาจะเห็น Error: There are currently no logon servers available to service the logon request
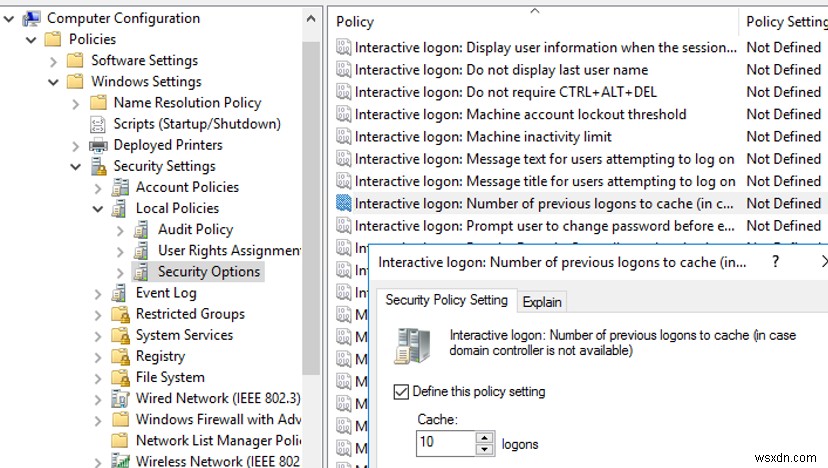
คุณยังสามารถกำหนดค่าตัวเลือกนี้ผ่าน Registry Parameter CashedLogonsCount REG_SZ ใน HKLM\Software\Microsoft\Windows NT\CurrentVersion\Winlogon
หาก User Log On ด้วย Saved Credentials พวกเขาไม่เห็นว่า Domain Controller ไม่พร้อมใช้งาน ใช้ GPO คุณสามารถแสดง Notification ของการใช้ Cached Credentials เพื่อ Log On ได้ โดย Enable GPO Option Report when logon server was not available during user logon Policy Under Computer Configuration -> Policies -> Administrative Templates -> Windows Components -> Windows Logon Options
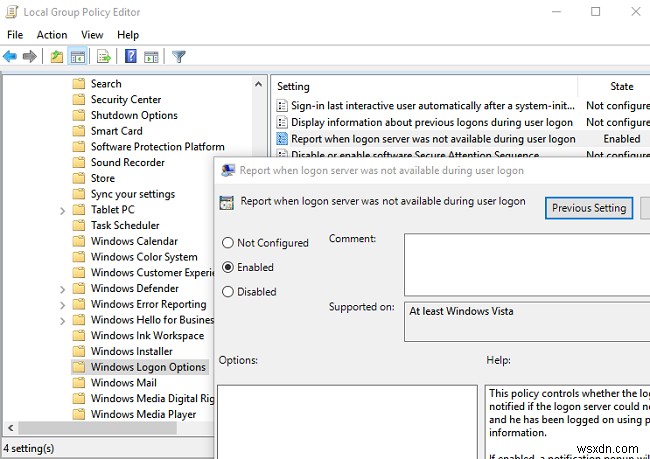
จากนั้น Notification ต่อไปนี้จะปรากฏใน Tray หลัง User Logon:
A domain controller for your domain could not be contacted. You have been logged on using cached account information. Changes to your profile since you last logged on might not be available.
ตัวเลือกนี้สามารถ Enable ผ่าน Registry ได้:
HKEY_LOCAL_MACHINE/SOFTWARE/Microsoft/Windows NT/Current Version/Winlogon
- ValueName:
ReportControllerMissing - Data Type:
REG_SZ - Value:
1
Security Risks ของ Cached Windows Credentials
Local Credential Caching มี Security Risks บ้าง หลังจากได้ Physical Access ไปยัง Computer/Laptop ที่มี Cached Data Attacker สามารถ Decrypt Password Hash ของคุณโดยใช้ Brute-force Attack ขึ้นอยู่กับความยาวและความซับซ้อนของ Password หาก Password ซับซ้อน จะใช้เวลามากมายในการ Brute Password ดังนั้นจึงไม่แนะนำให้ใช้ Caching สำหรับ Users ที่มี Local Administrator Permissions (หรือ Domain Admin Account)
เรียนรู้เพิ่มเติมเกี่ยวกับวิธีรักษาความปลอดภัย Administrator Accounts บน Windows Domain Network
เพื่อลด Security Risks คุณสามารถ Disable Credential Caching บน Office และ Administrator Computers แนะนำให้ลดจำนวน Cached Accounts บน Mobile Devices เหลือ 1 หมายความว่าแม้ Administrator จะ Log On เข้าคอมพิวเตอร์และ Data ของพวกเขาถูก Cache Password Hash ของ Administrator จะถูก Overwrite หลังจาก Device Owner Log On
สำหรับ AD Domains ที่มี Functional Level Windows Server 2012 R2 หรือใหม่กว่า คุณสามารถเพิ่ม Domain Administrator Accounts เข้าไปใน Group Protected Users Local Credential Caching ถูกห้ามสำหรับ Security Group นี้
คุณสามารถสร้าง GPOs แยกต่างหากใน Domain ของคุณเพื่อควบคุมการใช้ Cached Credentials สำหรับ Devices และ User Categories ต่างๆ (เช่น ใช้ GPO Security Filters, WMI Filters หรือ Deploy CashedLogonsCount Registry Parameter โดยใช้ GPP Item Level Targeting)
- สำหรับ Mobile (Laptop) Users:
CashedLogonsCount = 1 - สำหรับ Office Desktops:
CashedLogonsCount = 0
Policies แบบนี้จะลดโอกาสในการได้ Privileged User Hashes จาก Domain Joined Devices
