

บทความนี้จะแสดงวิธีใช้ SSL/TLS certificates ที่เชื่อถือได้เพื่อรักษาความปลอดภัยการเชื่อมต่อ RDP ไปยังคอมพิวเตอร์หรือเซิร์ฟเวอร์ Windows ในโดเมน Active Directory เราจะใช้ trusted SSL certs แทน self-signed RDP certificates เริ่มต้น (เมื่อใช้ self-signed RDP certificate ผู้ใช้จะได้รับคำเตือนว่า certificate ไม่ได้รับความไว้วางใจเมื่อเชื่อมต่อกับโฮสต์) ในตัวอย่างนี้ เราจะกำหนดค่า custom RDP certificates template ใน Certificate Authority และ Group Policy เพื่อออกและผูก SSL/TLS certificate ให้กับ Remote Desktop Services อัตโนมัติ
คำเตือน Self-Signed Certificate ของ Remote Desktop Connection (RDP)
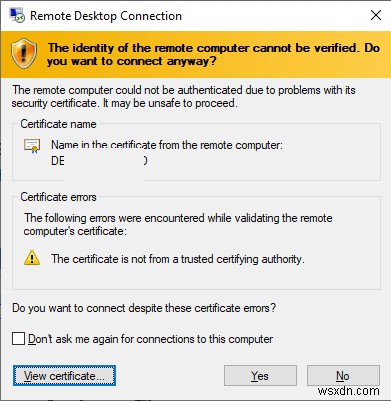
โดยค่าเริ่มต้น เพื่อรักษาความปลอดภัยเซสชัน RDP Windows สร้าง self-signed certificate ขึ้นมา ระหว่างการเชื่อมต่อครั้งแรกกับโฮสต์ RDP/RDS โดยใช้ไคลเอนต์ mstsc.exe ผู้ใช้จะเห็นคำเตือนต่อไปนี้:
The remote computer could not be authenticated due to problems with its security certificate. It may be unsafe to proceed. Certificate error: The certificate is not from a trusted certifying authority.
เพื่อดำเนินการต่อและสร้างการเชื่อมต่อ RDP ผู้ใช้ต้องคลิก Yes เพื่อป้องกันไม่ให้คำเตือน RDP cert ปรากฏทุกครั้ง คุณสามารถติ๊กตัวเลือก "Don't ask me again for connections to this computer"
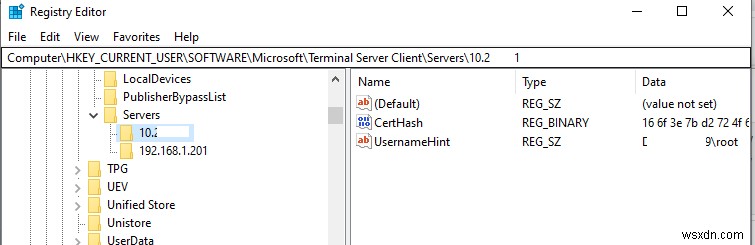
ในกรณีนี้ RDP certificate thumbprint จะถูกบันทึกในพารามิเตอร์ CertHash ของคีย์รีจิสทรีที่มีประวัติการเชื่อมต่อ RDP บนไคลเอนต์ (HKEY_CURRENT_USER\Software\Microsoft\Terminal Server Client\Servers\) หากคุณซ่อนคำเตือนว่าไม่สามารถยืนยัน RDP server ได้ ให้ลบ certificate thumbprint ออกจากรีจิสทรีเพื่อรีเซ็ตการตั้งค่า
แม้จะใช้ self-signed certificate เพื่อสร้างการเชื่อมต่อ เซสชัน RDP ของคุณก็ปลอดภัยและทราฟฟิกของคุณถูกเข้ารหัส
สร้าง RDP Certificate Template ใน Certificate Authority (CA)
ลองใช้ SSL/TLS certificate ที่เชื่อถือได้ซึ่งออกโดย corporate certificate authority เพื่อรักษาความปลอดภัยการเชื่อมต่อ RDP โดยใช้ certificate นี้ ผู้ใช้สามารถยืนยันตัวตน RDP server เมื่อเชื่อมต่อ สมมติว่า corporate Microsoft Certificate Authority ถูกปรับใช้ในโดเมนของคุณแล้ว ในกรณีนี้ คุณสามารถกำหนดค่าการออกและการเชื่อมต่อ certificate ให้กับคอมพิวเตอร์และเซิร์ฟเวอร์ Windows ทั้งหมดในโดเมนได้อย่างอัตโนมัติ
คุณต้องสร้างประเภท certificate template ใหม่สำหรับโฮสต์ RDP/RDS ใน CA ของคุณ:
- รันคอนโซล Certificate Authority และไปที่ส่วน Certificate Templates;
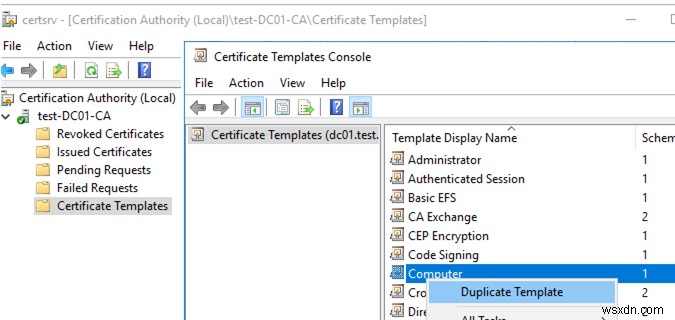
- Duplicate Computer certificate template (Certificate Templates -> Manage -> Computer -> Duplicate);
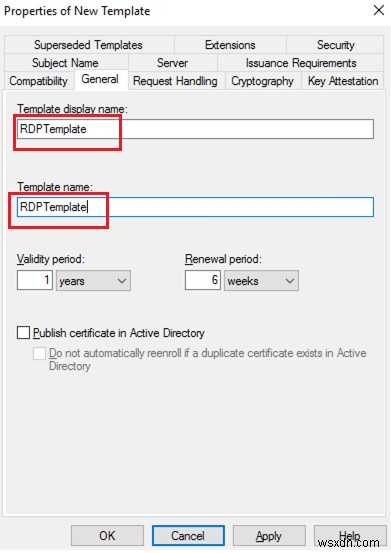
- ในแท็บ General ระบุชื่อ certificate template ใหม่ – RDPTemplate ตรวจสอบให้แน่ใจว่าค่าในฟิลด์ Template Name ตรงกับ Template display name;
- ในแท็บ Compatibility ระบุ minimum client version ที่ใช้ในโดเมนของคุณ (ตัวอย่าง Windows Server 2008 R2 สำหรับ CA และ Windows 7 สำหรับไคลเอนต์) ดังนั้น อัลกอริทึมเข้ารหัสที่แข็งแกร่งกว่าจะถูกใช้;
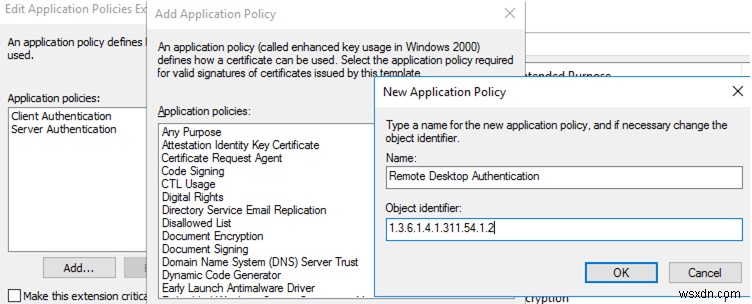
- จากนั้น ในส่วน Application Policy ของแท็บ Extensions จำกัดขอบเขตการใช้งาน certificate ให้เหลือ Remote Desktop Authentication เท่านั้น (ป้อน object identifier ดังนี้ — 1.3.6.1.4.1.311.54.1.2) คลิก Add -> New สร้างนโยบายใหม่และเลือกมัน;
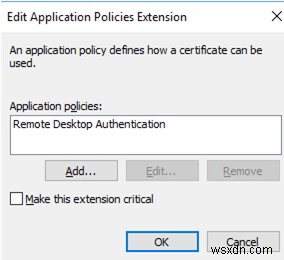
- ในการตั้งค่า certificate template (Application Policies Extension) ลบ policies ทั้งหมดยกเว้น Remote Desktop Authentication;
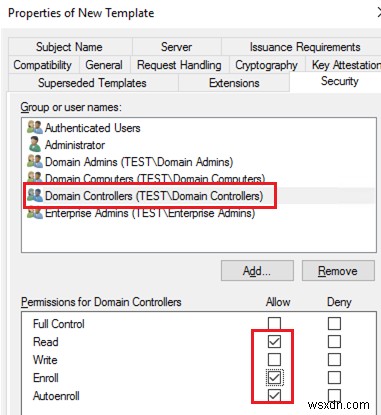
- เพื่อใช้ RDP certificate template นี้บนโดเมนคอนโทรลเลอร์ของคุณ ให้เปิดแท็บ Security เพิ่มกลุ่ม Domain Controllers และเปิดใช้งานตัวเลือก Enroll และ Autoenroll สำหรับมัน;
- บันทึก certificate template;
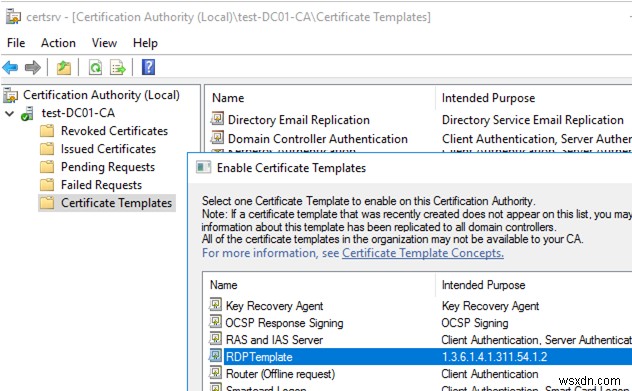
- จากนั้นใน Certificate Authority mmc snap-in คลิกโฟลเดอร์ Certificate Templates และเลือก New -> Certificate Template to Issue -> เลือก template ที่คุณสร้าง (RDPTemplate);
วิธีปรับใช้ RDP SSL/TLS Certificates โดยใช้ Group Policy?
ตอนนี้คุณต้องกำหนดค่า domain GPO เพื่อมอบหมาย RDP certificates ให้กับคอมพิวเตอร์/เซิร์ฟเวอร์โดยอัตโนมัติตาม template ที่กำหนดค่าไว้
สมมติว่าคอมพิวเตอร์โดเมนทั้งหมดเชื่อถือ corporate Certificate Authority นั่นคือ root certificate ถูกเพิ่มเข้าไปใน Trusted Root Certificate Authorities โดยใช้ GPO
- เปิดคอนโซล Domain Group Policy Management (gpmc.msc) สร้าง GPO object ใหม่และเชื่อมโยงกับ OU ที่มีเซิร์ฟเวอร์ RDP/RDS หรือคอมพิวเตอร์เพื่อออก TLS certificates อัตโนมัติเพื่อรักษาความปลอดภัยการเชื่อมต่อ RDP;
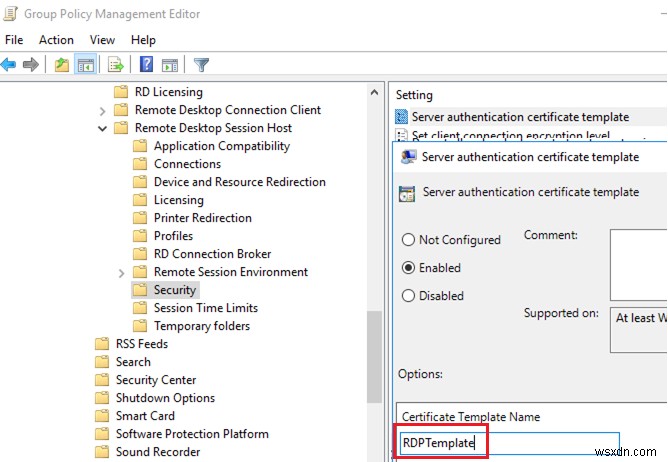
- ไปที่ส่วน GPO ต่อไปนี้ Computer Configuration -> Policies -> Administrative Templates -> Windows Components -> Remote Desktop Services -> Remote Desktop Session Host -> Security . เปิดใช้งานนโยบาย Server Authentication Certificate Template ระบุชื่อ CA template ที่คุณสร้างก่อนหน้านี้ (RDPTemplate);
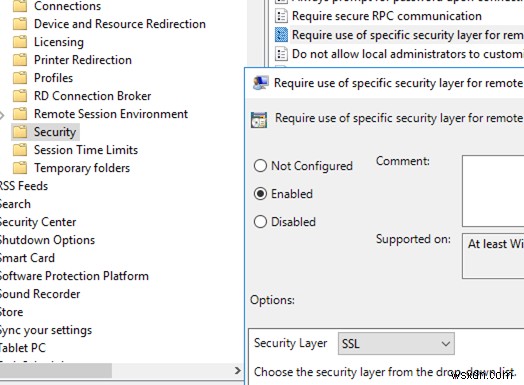
- จากนั้นในส่วน GPO เดียวกัน เปิดใช้งานนโยบาย Require use of specific security layer for remote (RDP) connections และตั้งค่า SSL สำหรับมัน;
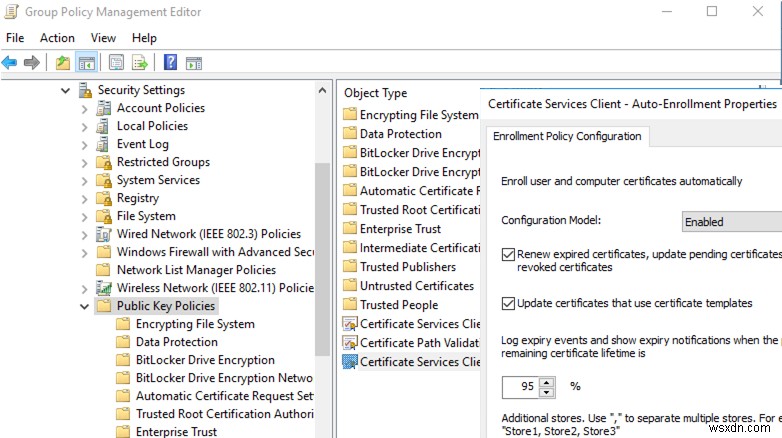
- เพื่อต่ออายุ RDP certificate อัตโนมัติ ไปที่ Computer configuration -> Windows settings -> Security Settings -> Public Key Policies ใน GPO และเปิดใช้งานนโยบาย Certificate Services Client – Auto-Enrollment Properties ติ๊ก "Renew expired certificates, update pending certificates and remove revoked certificates" และ "Update certificates that use certificate templates";
- หากคุณต้องการให้ไคลเอนต์ตรวจสอบ RDP server certificate เสมอ คุณต้องกำหนดค่านโยบาย Configure Authentication for Client = Warn me if authentication fails (Computer Configuration -> Policies -> Administrative Templates -> Windows Components -> Remote Desktop Settings -> Remote Desktop Connection Client);
- หากจำเป็น เปิดพอร์ต RDP เข้าขา TCP/UDP 3389 โดยใช้ firewall policies;
- จากนั้นอัปเดตการตั้งค่า group policy บนคอมพิวเตอร์ไคลเอนต์ เปิดคอนโซล computer certificate (
Certlm.msc) และตรวจสอบว่า Remote Desktop Authentication certificate ที่ออกโดย CA ของคุณปรากฏในส่วน Personal -> Certificates
หากการตั้งค่า Group Policy ใหม่ยังไม่ถูกนำไปใช้ ให้ใช้เครื่องมือ gpresult และบทความนี้เพื่อวินิจฉัย
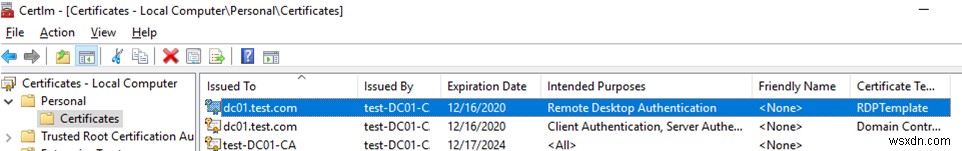
เพื่อนำ RDP certificate ใหม่ไปใช้ ให้รีสตาร์ท Remote Desktop Services:
Get-Service TermService -ComputerName mun-dc01| Restart-Service –force –verbose
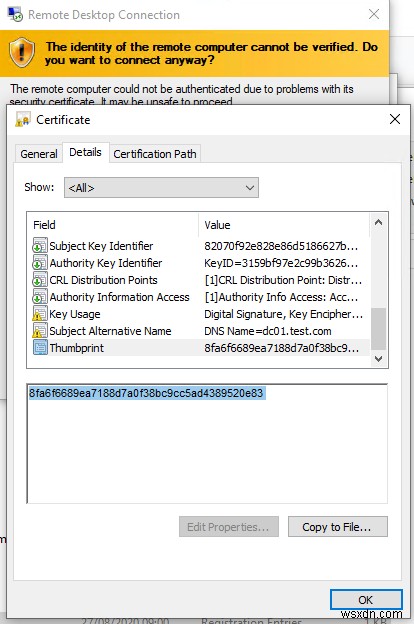
หลังจากนั้น เมื่อเชื่อมต่อกับเซิร์ฟเวอร์โดยใช้ RDP คุณจะไม่เห็นคำขอยืนยันว่า certificate ได้รับความไว้วางใจ (เพื่อดูคำขอ ให้เชื่อมต่อกับเซิร์ฟเวอร์ที่ certificate ออกให้โดยใช้ IP address แทน FQDN) คลิก View certificate ไปที่แท็บ Details และคัดลอกค่าในฟิลด์ Thumbprint
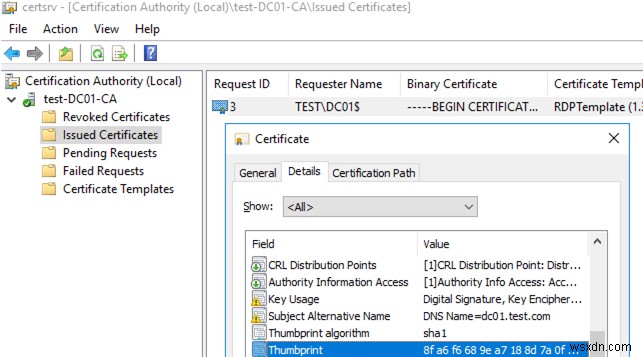
ในส่วน Issued Certificates ของคอนโซล Certification Authority คุณสามารถตรวจสอบได้ว่า RDPTemplate certificate ได้ถูกออกให้สำหรับ Windows server/computer เฉพาะตัว ยังตรวจสอบค่า Thumbprint ของ certificate:
จากนั้นเปรียบเทียบ thumbprint นี้กับ certificate thumbprint ที่ใช้โดย Remote Desktop Service คุณสามารถดูค่า RDS certificate thumbprint ในรีจิสทรี (HKLM:\SYSTEM\CurrentControlSet\Control\Terminal Server\WinStations, พารามิเตอร์ TemplateCertificate) หรือโดยใช้คำสั่ง PowerShell ต่อไปนี้:
Get-WmiObject -Class "Win32_TSGeneralSetting" -Namespace root\cimv2\terminalservices|select SSLCertificateSHA1Hash
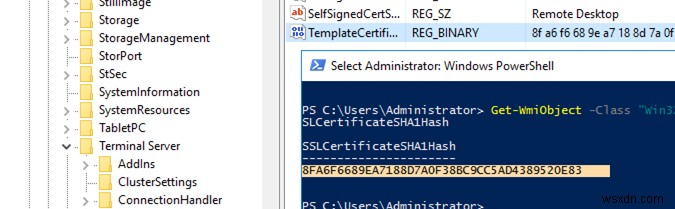
จากนั้น เมื่อเชื่อมต่อกับ remote desktop ของโฮสต์ Windows ใดๆ คุณจะไม่เห็นคำเตือนเกี่ยวกับ RDP certificate ที่ไม่น่าเชื่อถือ
การลงนามไฟล์ RDP ด้วย Trusted TLS Certificate Thumbprint
หากคุณไม่มี CA แต่คุณไม่ต้องการให้ผู้ใช้เห็นคำเตือนเมื่อพวกเขาเชื่อมต่อกับโฮสต์ RDP/RDS คุณสามารถเพิ่ม certificate เข้าไปใน trusted certificates บนคอมพิวเตอร์ผู้ใช้
รับค่า RDP certificate thumbprint ตามที่อธิบายข้างต้น:
Get-WmiObject -Class "Win32_TSGeneralSetting" -Namespace root\cimv2\terminalservices|select SSLCertificateSHA1Hash
ใช้ลายนิ้วมือนี้เพื่อลงนามไฟล์ .RDP ด้วยเครื่องมือ RDPSign.exe:
rdpsign.exe /sha256 25A27B2947022CC11BAFF261234567DEB2ABC21 "C:\ps\mun-dc01.rdp"
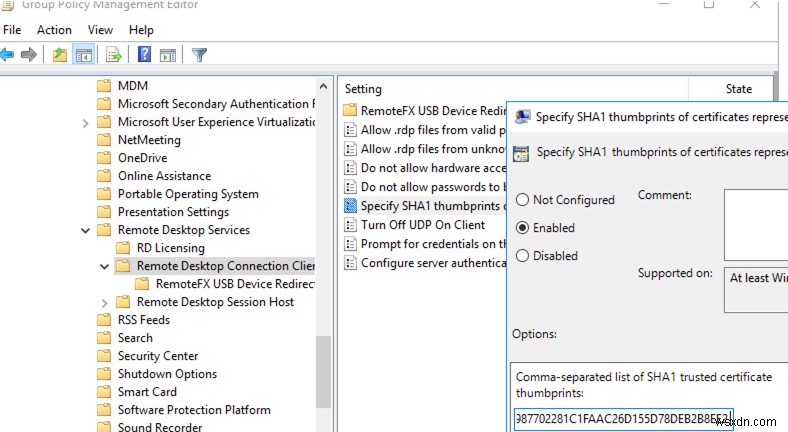
จากนั้นเพิ่ม thumbprint นี้เข้าไปใน trusted certificates บนคอมพิวเตอร์ผู้ใช้โดยใช้ GPO ระบุ thumbprints (คั่นด้วย semicolon) ในนโยบาย Specify SHA1 thumbprints of certificates representing trusted .rdp publishers ใน Computer Configuration -> Policies -> Administrative Templates -> Windows Components -> Remote Desktop Settings -> Remote Desktop Connection Client
เพื่อกำหนดค่าการล็อกอิน RDP แบบโปร่งใสโดยไม่ต้องใส่รหัสผ่าน (RDP Single Sign On) ให้กำหนดค่านโยบาย Allow delegation defaults credential และระบุโฮสต์เนม RDP/RDS ในมัน (ดูบทความนี้วิธีทำ)
