

เมื่อเชื่อมต่อกับเซิร์ฟเวอร์ VMWare vCenter ผ่านเว็บเบราว์เซอร์ จะมีคำเตือนเกี่ยวกับ Self-Signed Certificate ที่ออกโดย Certificate Authority ที่ไม่น่าเชื่อถือ ใน Firefox สามารถปิดคำเตือนได้โดยเพิ่มเว็บไซต์ vCenter เข้าไปในรายการข้อยกเว้น แตใน Internet Explorer ขั้นตอนซับซ้อนกว่า
SSL Certificates ที่ติดตั้งมาพร้อมกับ ESXi และ vCenter Servers เป็น Self-Signed ดังนั้นระบบอื่นๆ ไม่ไว้วिशวาเขาและแสดงคำเตือนหรือบล็อกการเชื่อมต่อกับเว็บไซต์เหล่านี้ เพื่อปิดคำเตือน Self-Signed Certificate สามารถเพิ่ม Self-Signed Certificate เข้าไปในรายการ Trusted Certificates หรือแทนที่ Certificate ด้วยของตัวเองที่ออกโดย CA ที่น่าเชื่อถือ เราจะพิจารณาวิธีแรก ขั้นตอนง่ายแต่มีรายละเอียดที่ไม่ชัดเจนบ้าง
ดังนั้น เมื่อเปิดหน้าเว็บ vCenter Server ในเบราว์เซอร์ จะปรากฏหน้าต่างคำเตือนดังนี้:
There is a problem with this website's security certificate.
The security certificate presented by this website was not issued by a trusted certificate authority.
The security certificate presented by this website was issued for a different website's address.
Security certificate problems may indicate an attempt to fool you or intercept any data you send to the server.
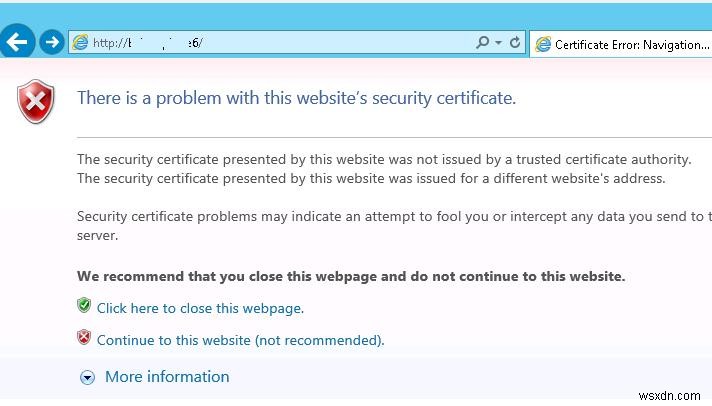
หมายเหตุ: คำเตือน The security certificate presented by this website was issued for a different website's address แสดงขึ้นเพราะในกรณีนี้ Host Name ต่างจากชื่อ CN ที่ Certificate ออกให้ เพื่อไม่ให้คำเตือนนี้แสดง ต้องเปิดชื่อ FQDN ของเซิร์ฟเวอร์ที่ Certificate ออกให้ในเบราว์เซอร์ สำหรับความสะดวก สามารถแทนที่ Certificate นี้ด้วยของตัวเองที่สร้างด้วย Cmdlet New-SelfSignedCertificate ซึ่งอนุญาตให้ออก Certificate สำหรับชุด CN ใดๆ
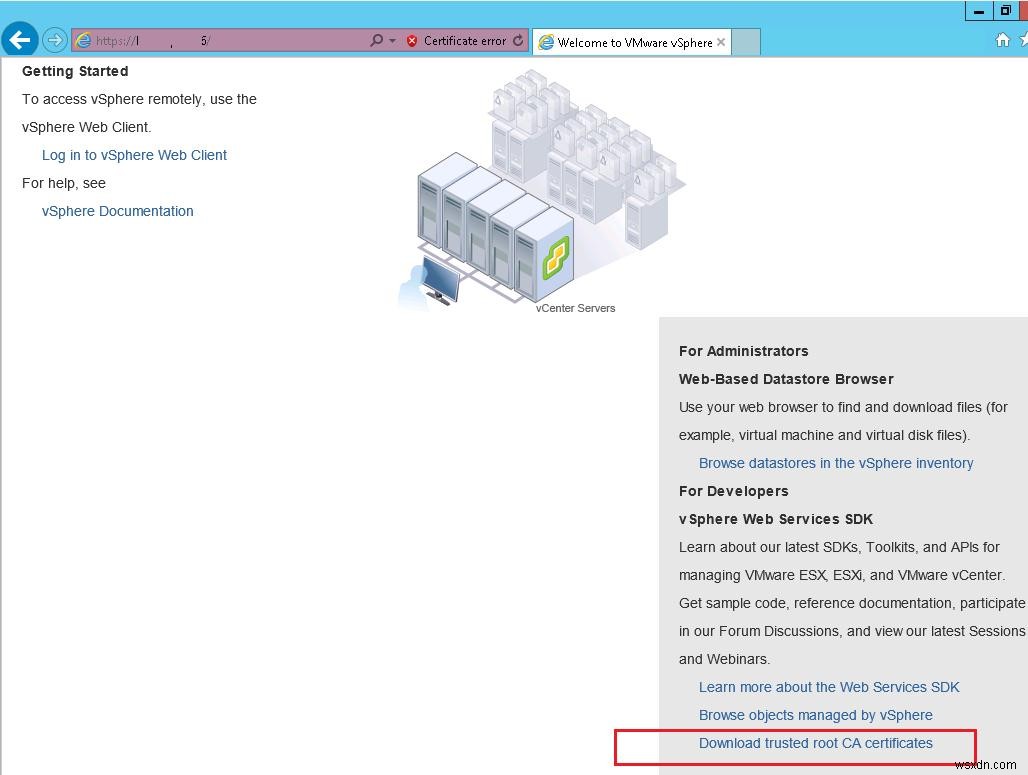
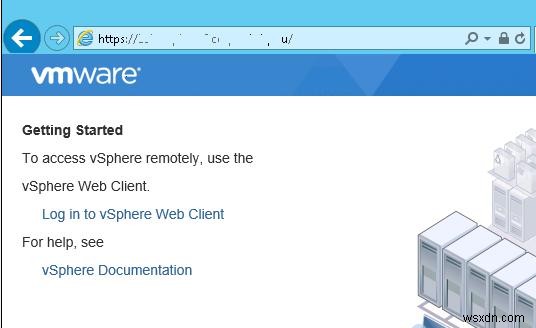
หลังคลิก Continue to this website link (not recommended) จะเข้าสู่หน้า Getting Started ของ vCenter เพื่อดาวน์โหลด Certificate คลิก Download trusted root CA certificates
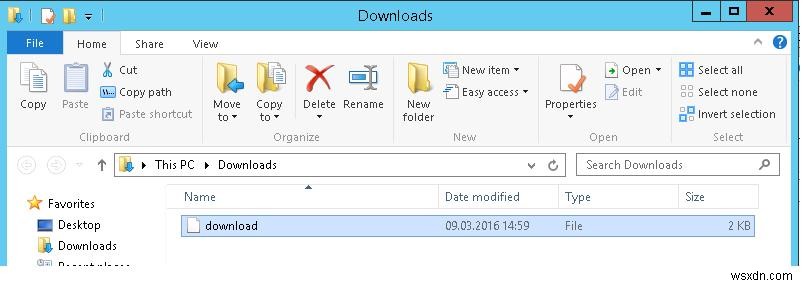
บันทึกไฟล์ไปไดเรกทอรีใดๆ ชื่อไฟล์คือ download (ไม่มี Extension)
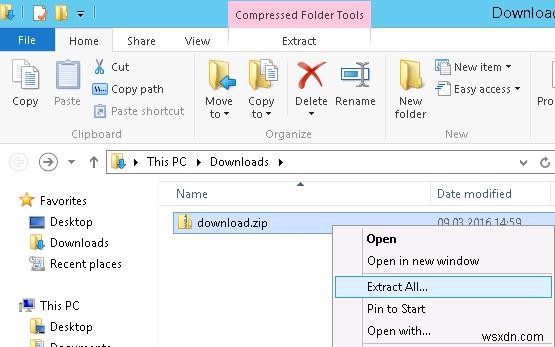
จากนั้นเปลี่ยน Extension ของ download เป็น download.zip และแตกไฟล์ด้วย Archiver built-in (Extract All)
Archive Cert มี 2 ไฟล์ ที่มี Extension .0 และ .r0 เปลี่ยน Extension .0 เป็น .cer
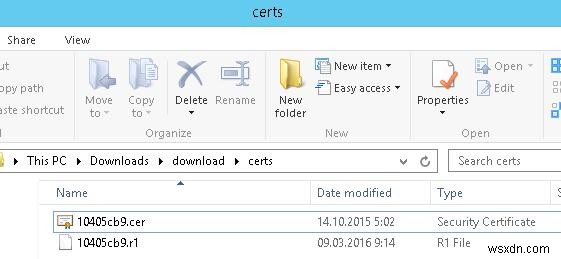
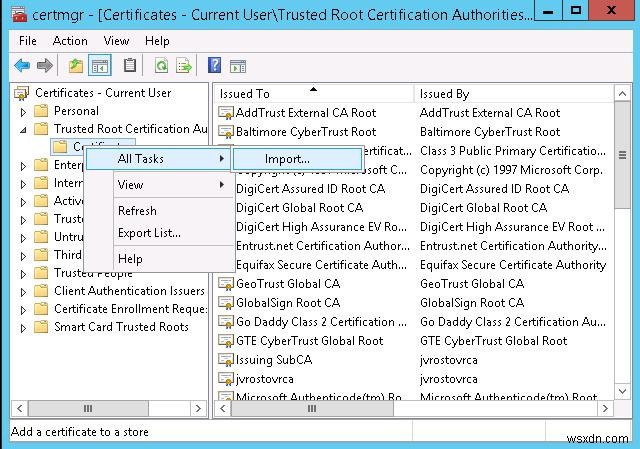
ตอนนี้เหลือแค่เพิ่ม Root CA Certificate นี้เข้าไปในรายการ Trusted Certificates สมมติ เราต้องการให้ Certificate นี้เชื่อถือได้เฉพาะบัญชีปัจจุบัน เปิดคอนโซล certmgr.msc ไปที่ Certificates > Trusted Root Certification Authorities และเปิด Wizard นำเข้า Certificate (Import) จากเมนู Context
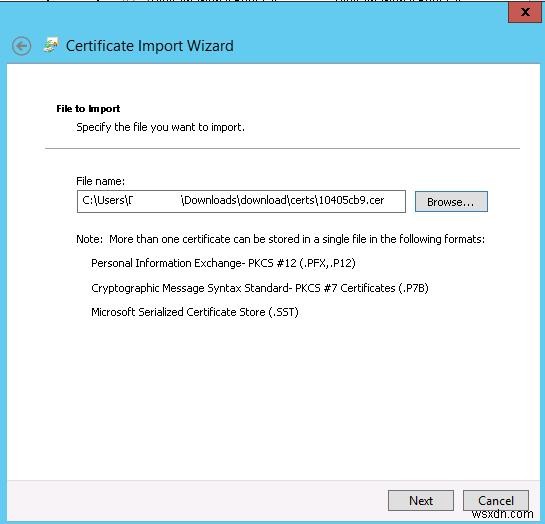
เลือกไฟล์ Certificate ที่ได้ก่อนหน้านี้ และวางไว้ใน Store Trusted Root Certification Authorities
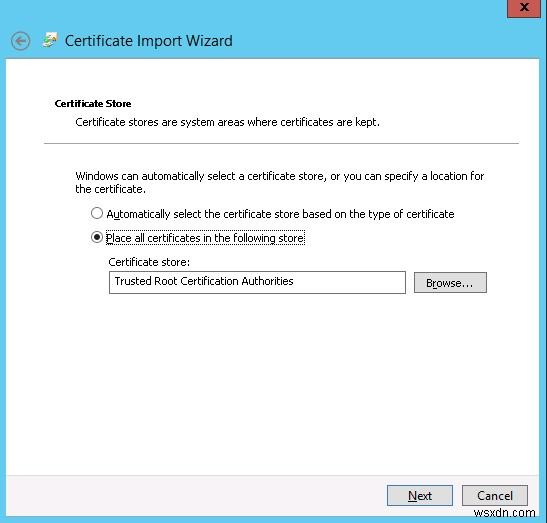
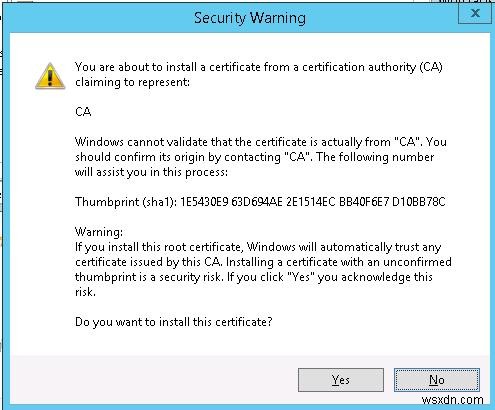
ยืนยันการเพิ่ม Certificate
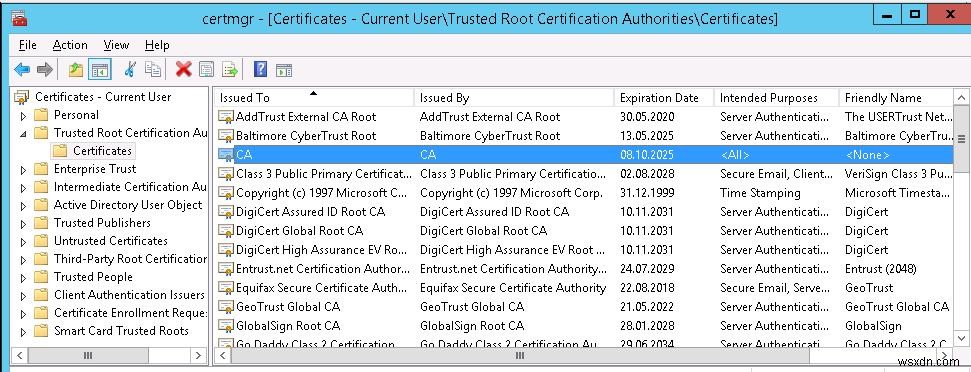
Certificate ใหม่ชื่อ CA จะปรากฏในรายการ
เปิดหน้าเว็บ vCenter ในเบราว์เซอร์อีกครั้ง คำเตือนจะไม่ปรากฏอีก
หมายเหตุ: หากต้องการขยาย Certificate นี้ไปยังคอมพิวเตอร์ในโดเมน สามารถใช้ฟีเจอร์ Group Policy (How to Install a Certificate on Domain Computers Using GPO)
แนวทางนี้ใช้ได้กับ vCenter Server Appliance หากใช้ Windows vCenter Server จะไม่สามารถดาวน์โหลดไฟล์ Certificate ได้ เนื่องจากไม่มี Link ดาวน์โหลด Archive พร้อม Certificate ไฟล์นี้เก็บอยู่บน vCenter Server (ที่รัน Windows) ใน C:\ProgramData\VMware\SSL\ (C:\Programdata\VMware\VMware VirtualCenter\SSL ในเวอร์ชันก่อนหน้า) Certificate จากไดเรกทอรีนี้ต้องนำเข้า (Import) บน Client ด้วยวิธีเดียวกัน
