

Last time tested system sandboxing software XP era remember programs like ShadowGuard if memory servers me well และ Deep Freeze designed create virtual filesystem layer changes made during active session next reboot scrubbed back clean state essence read-only system with selective modification ability
Applications may want something less complicated for those in need there was Sandboxie happens never really got try application not early days nor later after acquired but now tried Windows Defender Application Guard (unsuccessfully) Windows 10 Home decided give this program another look test and review Sandboxie let's build us a security castle!
Setup and configuration
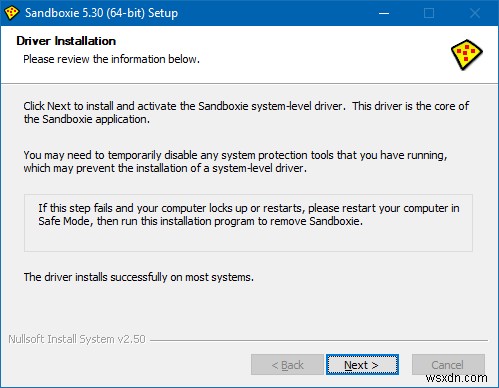
Installation not complicated but requires attention what you're doing principal part setup Sandboxie driver does all magic background no problem getting done Windows 10 Home box not using other security software except built-in Mitigation Protections
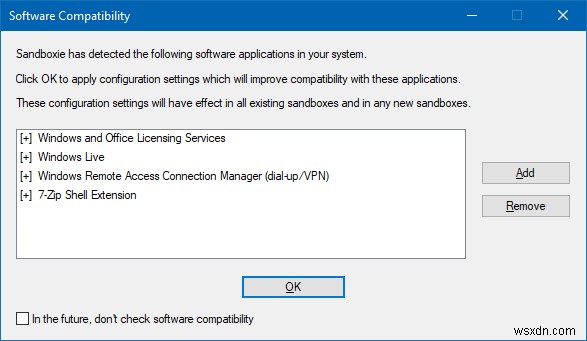
First run Sandboxie scanned software system asked whether apply various configuration settings not sure what this does at this point let step complete well not like you have option not click OK but can remove entries shown
Tutorial
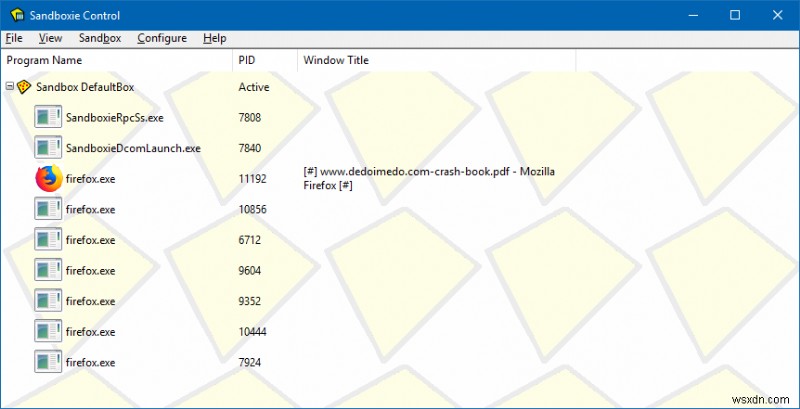
Because Sandboxie usage isn't trivial program starts with tutorial follow few steps familiar with how application works found wizard somewhat clunky only figured what gives after completed it so to speak TL;DR you will have Sandboxie-ed shortcut default Web browser on desktop run that browser (Firefox in this case) launches sandboxed main program interface task manager sort shows all sandboxed applications grouped by containers (later configure different sandboxes) program running under Sandboxie identify by [#] prefix suffix in title (not trivial not all programs show titles) and yellow border hover mouse over application window
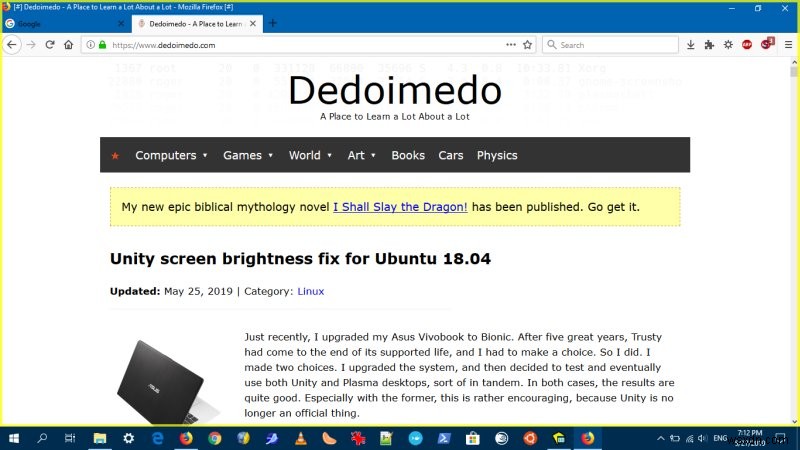
Playing in the sand
Started using program soon learned function called Immediate Recovery copy file into pre-defined folders "recover" them from sandbox into real system default Sandboxie isolates applications running inside from outside filesystem close them all changes lost (like downloads) like running browser Linux live session no persistence changes gone reboot don't know Linux ignore last sentence
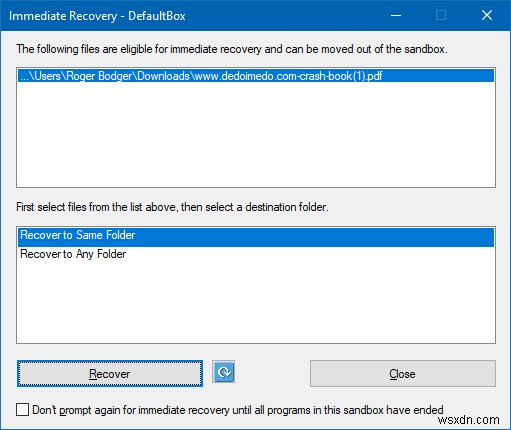
Close means simply keep file inside sandboxed session not intuitive
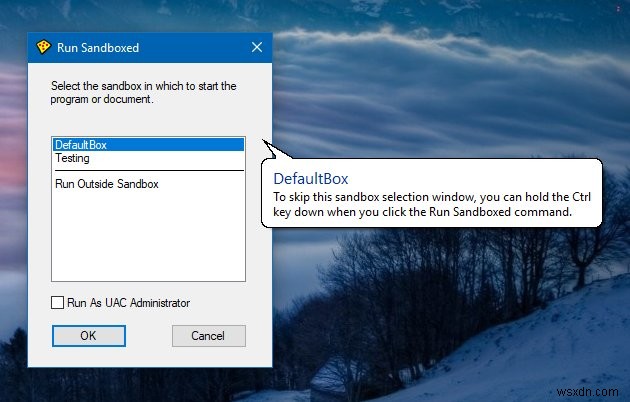
Default shortcut default browser but launch any program via right-click option select desired (sand)box
Program behaved well example couldn't see browsing history bookmarks either Firefox Chrome running sandboxed didn't notice performance degradation conflict plugins extensions media playback but Chrome no title no indication running sandboxed unless hover mouse cursor
Settings and more settings
Soon found multiple ways tweak Sandboxie configuration right-click process listed inside sandbox make changes how it behaves only effective current session then global settings somewhat confusing
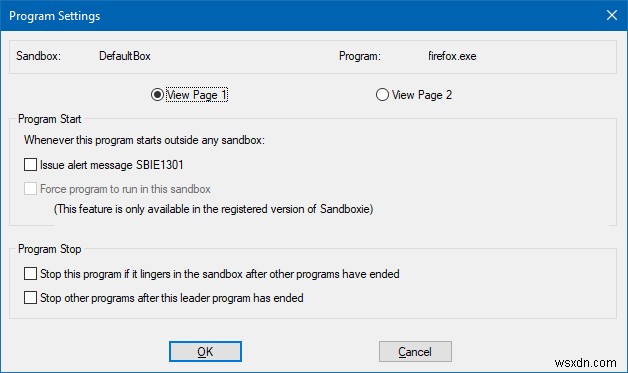
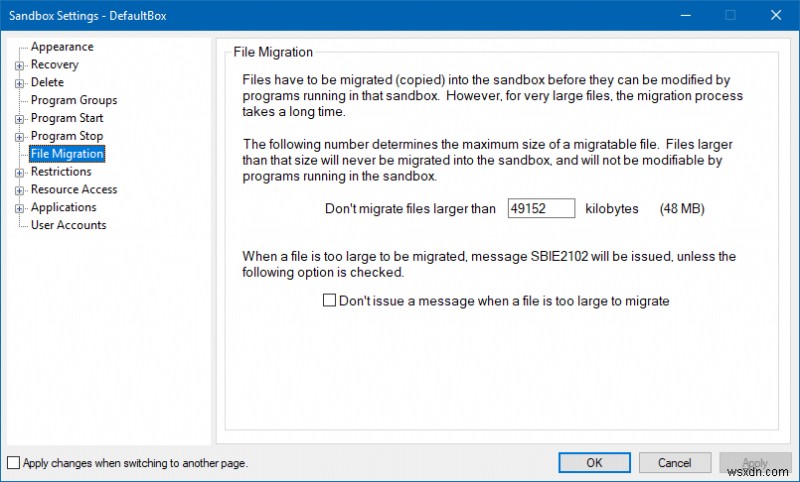
Hard finding per-sandbox global settings but find them did super-long list options tweak including look and feel how and if recover or delete files grouping programs (browsers based on Firefox Chromium) migration files into sandbox found some options tricky explanations use not format need put brain in reverse understand what actually happens
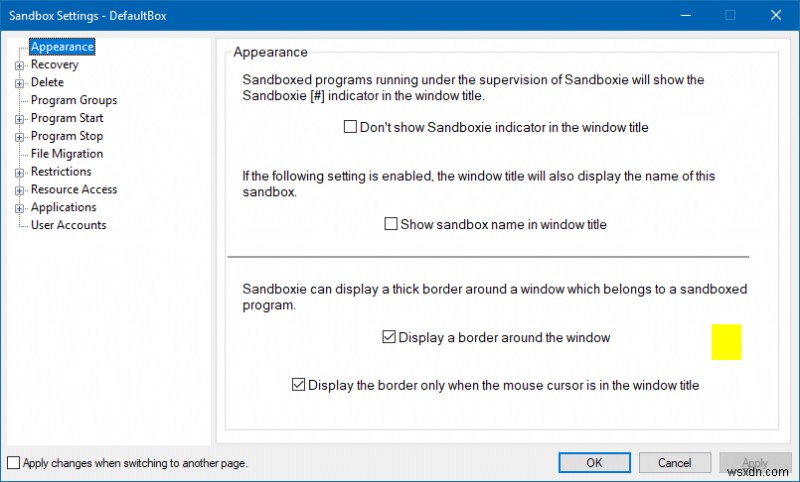
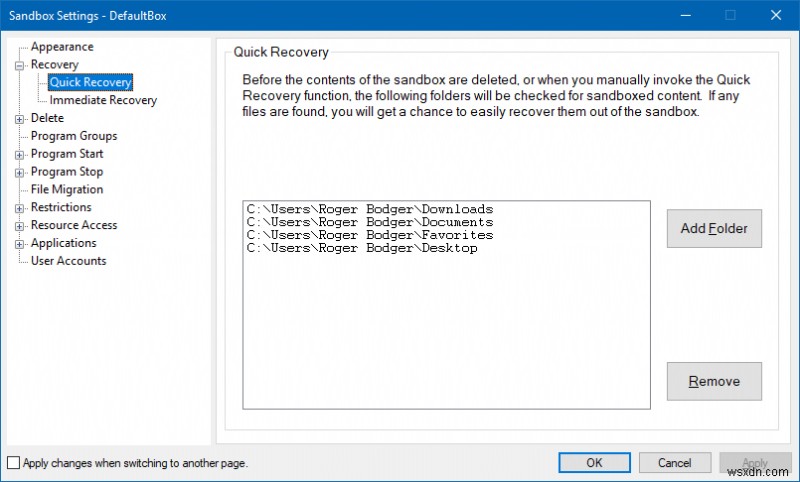
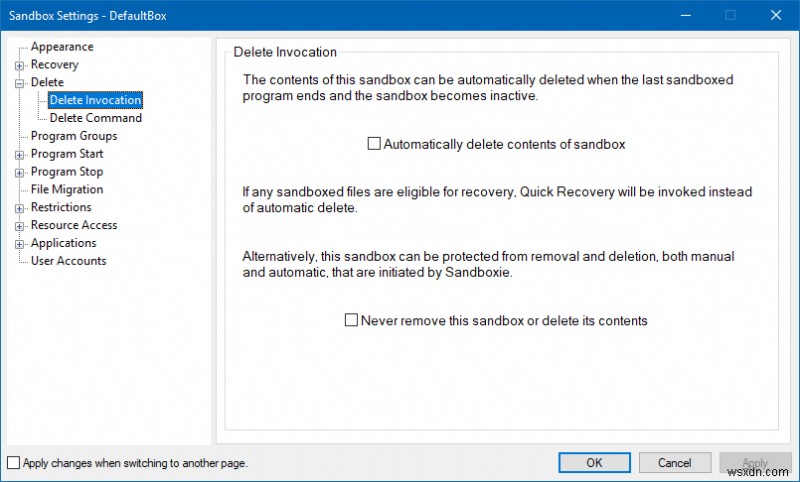
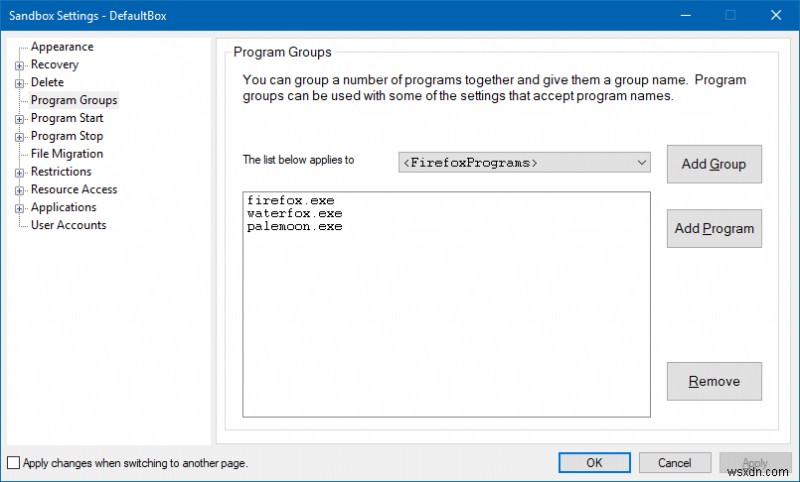
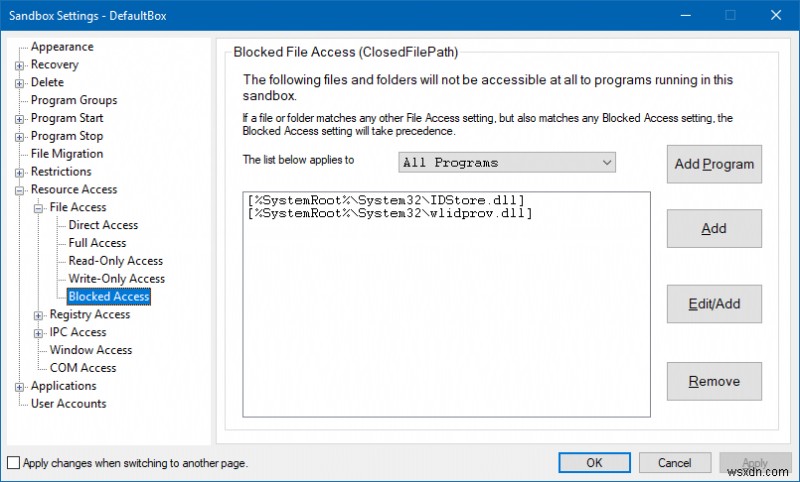
Long detailed list restrictions access rights decide resource types sandboxed applications have (particular box) fine-tuned list permissions including files read written files not accessible network ports more again Linux analogy similar writing AppArmor SELinux rules no trivial task really need good understanding system internals make changes without compromising security breaking applications or even system yes not careful lock yourself out Windows instance listed DLLs below what mean ordinary user?
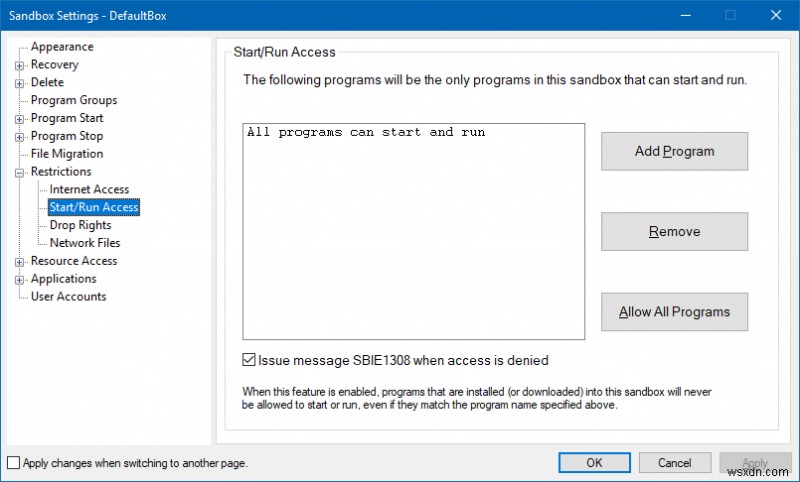
Things more complicated Registry, IPC, COM true nerdy territory unless fully understand typical Windows process memory mapping shouldn't even looking this section
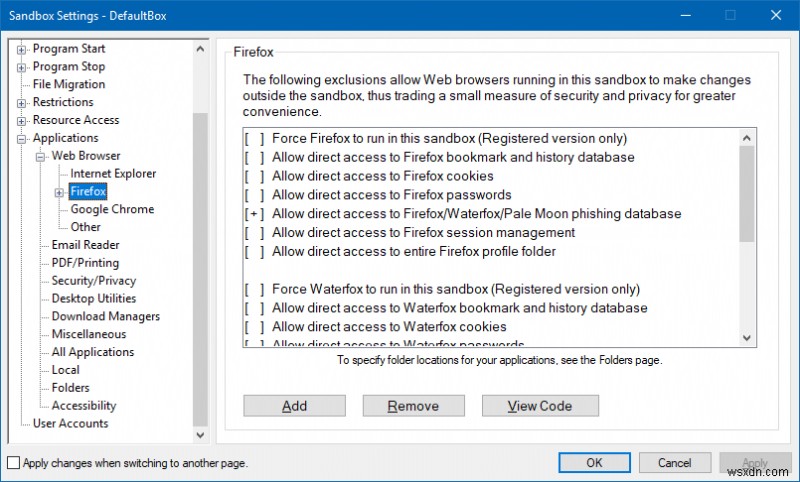
Applications option opens super-long list categories various default rules add remove configure browsers email readers PDF software many other applications tools separately again found lots rules/explanations difficult understand instance rule written no sign mean blocked? or just rule configure? Default exclusions Immediate Recovery what mean? file types locations recovered? or excluded?
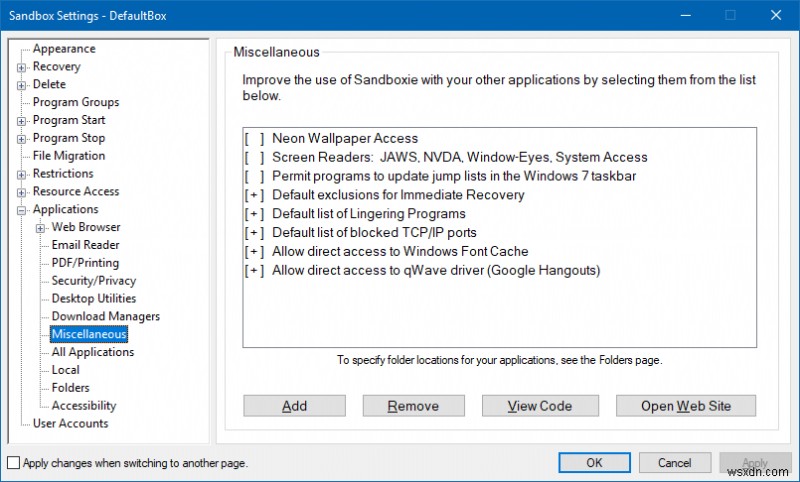
Option edit program configuration through ini file feels old school but there for those need speed geeky actions all in all configuration piece leaves lot desired emphasized how complex it is
How does this compare to other methods?
Well asking same question App Guard article if using browsers already have sandboxing capabilities using Exploit Protection using extension Noscript also possibly running under standard (limited) account how much value something like this?
First thing arbitrary execution code but all above definitely limit applicability second thing far more important where does sandbox model break? answer is user indeed testing noticed option save files unsandboxed folders therein lies problem allow bad file through eventually use unrestricted manner perhaps won't render damage isolated session but later especially don't notice "bad" symptoms convinced safe in fact presence powerful security tool may even lower sense self-preservation
Then option tinker sandbox settings make changes add remove file registry access define folders immediate recovery similar not deeply skilled potentially create gap sandbox isolation more apparent if actually have usability problem (result security restrictions) try work around it not Sandboxie issue general one paradox software security not skilled enough use software full potential not likely benefit but if you are then most likely don't need it
This why find EMET Exploit Guard extremely valuable may cripple usage some cases results applied mitigations (very rare but possible) but done without classifying software good or bad instead done much lower level good or bad instruction or memory access Exploit Guard does not discriminate between bad software and good software written badly
Similarly standard account limited what you can do nothing random hax0r trying pwn you rudimentary than that no privilege changing many system settings period doesn't matter deliberate mistake whatever not possible
Back to Sandboxie default does lot good stuff don't tinker should have reasonable extra security layer but Sandboxie does not limit what happens within sandbox will not prevent code running or prevent copying data out of sandbox moreover ability tinker change settings potentially open holes isolation mechanism from what tested Sandboxie good isolating Internet-facing programs from system but will not limit access Internet data like browsing activity
สรุป
Sandboxie nice robust program offers advanced users high degree flexibility setting up low-privilege containers untrusted Internet-facing software isolate applications manner somewhat similar mobile operating systems except Sandboxie did this ages ago furthermore don't like isolation mechanism working or one programs isn't behaving functioning correctly easily execute outside Sandboxie context Bob's your uncle
However Sandboxie limitations setup configuration far from trivial require solid level understanding system devices access alike can turn Sandboxie usage into burden lastly Sandboxie limits privileges but does not sanitize them means memory leak within context running application (illegal instruction some kind) Sandboxie will not stop that or prevent copying file downloaded Web out of container means Sandboxie makes sense when don't trust what you're doing rather than when you do believe value testing applications need roam wild Internet unchecked all in all recommended worth checking perhaps future versions simplified interface more intuitive access control flow take care
Cheers.
