

บทช่วยสอนนี้มีคำแนะนำแก้ไขข้อผิดพลาดขณะพยายามจัดการคอมพิวเตอร์ระยะไกลผ่าน Active Directory Users and Computers จาก AD Domain Server 2016: "Computer cannot be connected. Verify that the network path is correct, the computer is available on the network, and that the appropriate Windows Firewall rules are enabled on the target computer. To enable the appropriate rules Windows Firewall rules on the remote computer, open the Windows Firewall with Advanced Security snap-in and enable the following inbound rules: COM+ Network Access (DCOM-In)…"
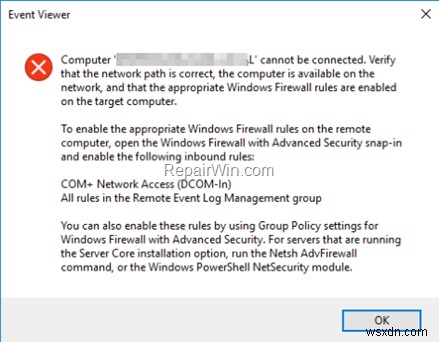
วิธีแก้ไข: ไม่สามารถจัดการคอมพิวเตอร์จาก Active Directory Users and Computers – Computer cannot be connected (Active Directory 2016/2019)
ข้อความ "Computer cannot be connected" ใน Active Directory อาจเกิดจาก:
เหตุผลที่ 1. คอมพิวเตอร์ไม่มีอยู่บนเครือข่ายหรือปิดเครื่องอยู่ ตรวจสอบว่าคอมพิวเตอร์เปิดอยู่
เหตุผลที่ 2. ไม่สามารถ Resolve IP Address ของคอมพิวเตอร์จาก Domain Controller ได้ ปัญหามักเกิดเมื่อคอมพิวเตอร์ใช้ DNS Server จาก Router (ISP) ให้ตรวจสอบว่าใช้ AD DNS
ขั้นตอนตรวจสอบ:
1. Ping คอมพิวเตอร์ด้วยชื่อ หรือใช้คำสั่ง NSLOOKUP เพื่อตรวจสอบว่าชื่อและ IP ถูก Resolve ถูกต้องจาก DNS Server
2. หาก AD Domain Controller ทำหน้าที่ DNS Server ไปที่ Control Panel > Administrative Tools > DNS > Forward Lookup Zones เพิ่ม Record ที่หายไป
เหตุผลที่ 3. การจัดการระยะไกลถูกบล็อกโดย Windows Firewall บนเครื่องเป้าหมาย (คอมพิวเตอร์ที่ต้องการจัดการ) สามารถแก้ไขได้โดยปิด Windows Firewall (ไม่แนะนำ) หรือเปิดใช้งาน COM+ Network Access ใน Windows Firewall บนเครื่องเป้าหมายหรือทั้งหมดใน AD โดยทำตามวิธีด้านล่าง:
- วิธีที่ 1: เปิดใช้งาน COM+ Network Access (DCOM-In) บนเครื่องเป้าหมาย
- วิธีที่ 2: เปิดใช้งาน COM+ Network Access (DCOM-In) สำหรับคอมพิวเตอร์ AD ทั้งหมด (Group Policy)
วิธีที่ 1: เปิดใช้งานกฎ COM+ Network Access บนเครื่องเป้าหมาย
เพื่ออนุญาตการจัดการระยะไกล (เปิดใช้งาน COM+ Network Access) ใน Windows Firewall บน Windows 10, 8, 7:
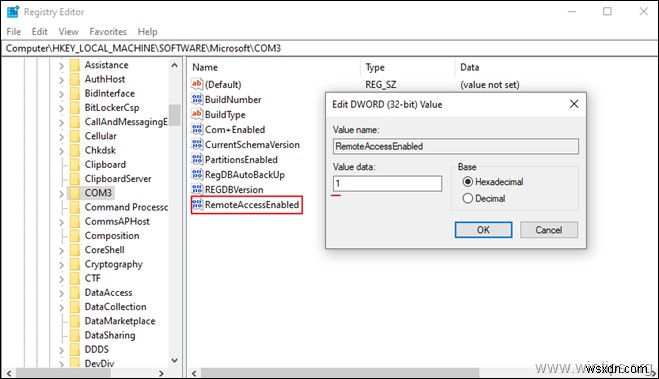
1. เปิด Registry Editor บนคอมพิวเตอร์ที่ต้องการเชื่อมต่อ/จัดการ ไปที่:
- Computer\HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\COM3
2. ทางขวา ดับเบิลคลิก RemoteAccessEnabled เปลี่ยนค่า Value data จาก 0 เป็น 1
3. คลิก OK และ ปิด Registry Editor
4. รีสตาร์ท คอมพิวเตอร์
วิธีที่ 2: อนุญาต "Remote administration" สำหรับคอมพิวเตอร์ AD ทั้งหมดผ่าน Domain Group Policy
เพื่อเปิดใช้งานกฎ COM+ Network Access (อนุญาต "Remote administration") บนคอมพิวเตอร์ทั้งหมดใน Active Directory:
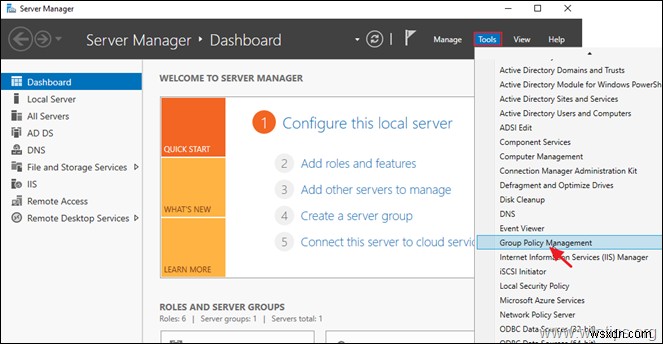
1. ใน Server 2016 AD Domain Controller เปิด Server Manager จากเมนู Tools เปิด Group Policy Management *
* หรือไป Control Panel -> Administrative Tools -> Group Policy Management
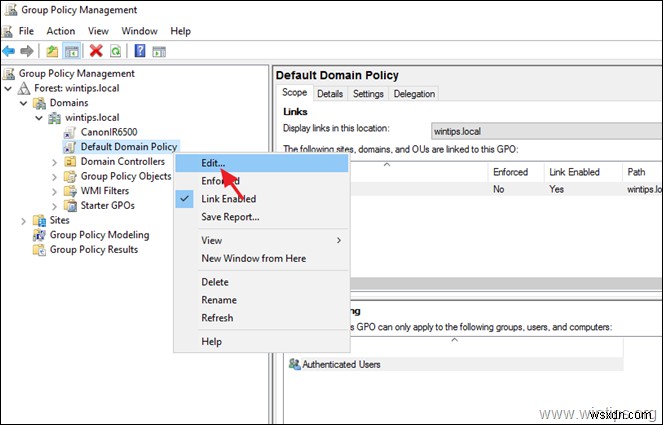
2. ภายใต้ Domains เลือก Domain ของคุณ แล้ว คลิกขวา ที่ Default Domain Policy เลือก Edit
3. ไปที่:
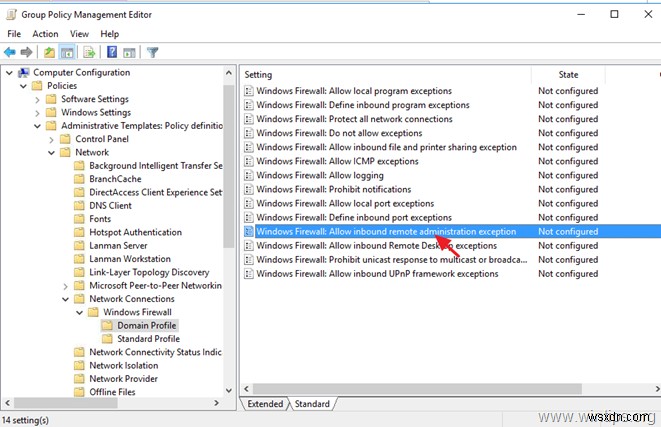
- Computer Configuration\Policies\Administrative Templates\Network\Network Connections\Windows Firewall\Domain Profile
4. ทางขวา ดับเบิลคลิก: Windows Firewall: Allow inbound remote administration exception
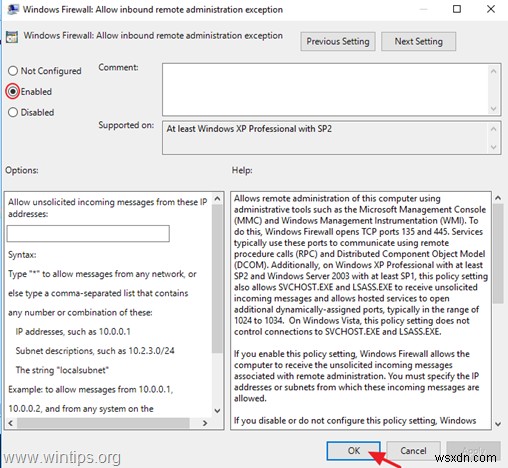
5. เลือก Enabled คลิก OK
6. ปิด Group Policy Management Editor
7. เปิด Command Prompt as Administrator ใช้คำสั่งอัปเดต Group Policy:
- gpupdate /force
เสร็จแล้ว! วิธีไหนใช้ได้กับคุณ?
แจ้งให้ทราบว่าคู่มือนี้ช่วยได้หรือไม่โดยทิ้งความคิดเห็น กดไลค์และแชร์เพื่อช่วยผู้อื่น
